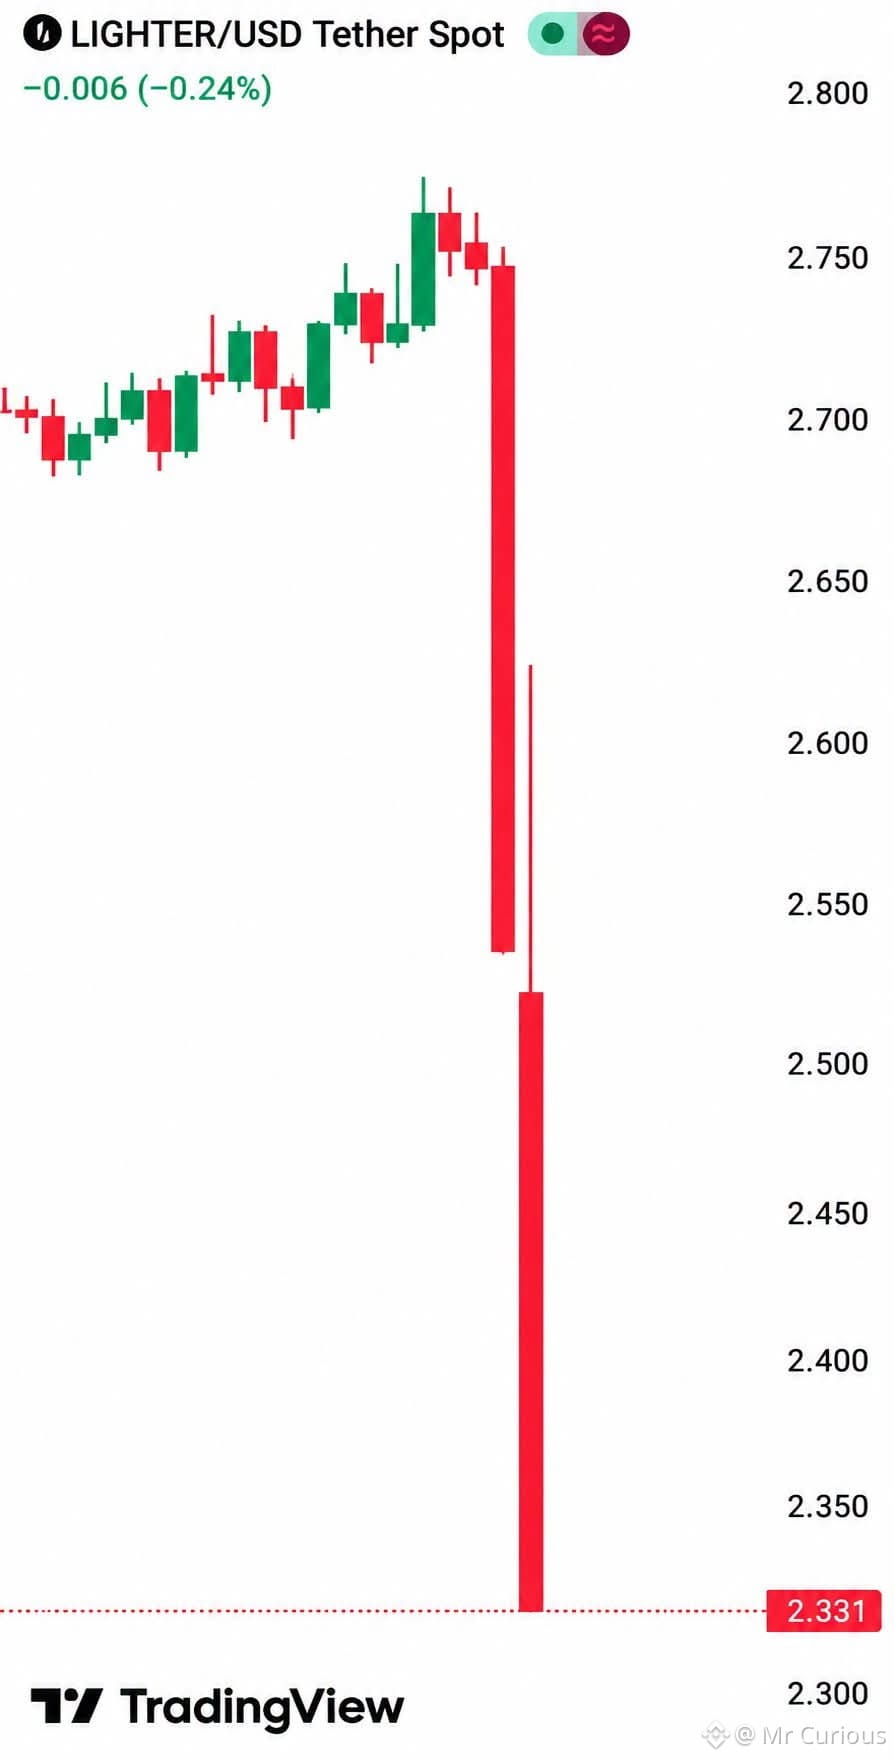
‼️SECURITY ALERT: Lighter's $LIT token has plunged more than 20% amid a suspected $15.5 MILLION theft involving compromised API keys.
Early analysis suggests attackers gained access to API keys belonging to two market-maker accounts and exploited the protocol's liquidity-pool mechanism to drain funds.
The attacker allegedly transferred victims' $USDC into a newly created pool, acquired nearly 100% of its shares, and then redeemed those shares to withdraw the funds.
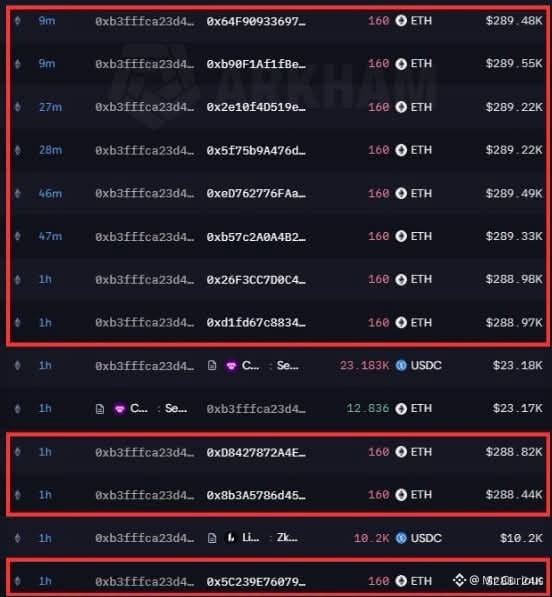
An associated wallet reportedly withdrew $10.39 million in USDC and converted it into approximately 5,750 ETH through CoW Swap.
Around 3,845 $ETH , worth approximately $6.91 million, reportedly remain.
Lighter says the incident appears to involve a single compromised external party. Withdrawals and new pool creation were suspended, while another potential $5 million withdrawal remained pending.
Importantly, the API-key explanation is still preliminary. A protocol-wide security breach has NOT been confirmed.
This incident highlights a serious risk in DeFi: even API permissions that cannot directly withdraw funds may create unexpected vulnerabilities when combined with other protocol features.
Early analysis suggests attackers gained access to API keys belonging to two market-maker accounts and exploited the protocol's liquidity-pool mechanism to drain funds.
The attacker allegedly transferred victims' $USDC into a newly created pool, acquired nearly 100% of its shares, and then redeemed those shares to withdraw the funds.
An associated wallet reportedly withdrew $10.39 million in USDC and converted it into approximately 5,750 ETH through CoW Swap.
Around 3,845 $ETH , worth approximately $6.91 million, reportedly remain.
Lighter says the incident appears to involve a single compromised external party. Withdrawals and new pool creation were suspended, while another potential $5 million withdrawal remained pending.
Importantly, the API-key explanation is still preliminary. A protocol-wide security breach has NOT been confirmed.
This incident highlights a serious risk in DeFi: even API permissions that cannot directly withdraw funds may create unexpected vulnerabilities when combined with other protocol features.