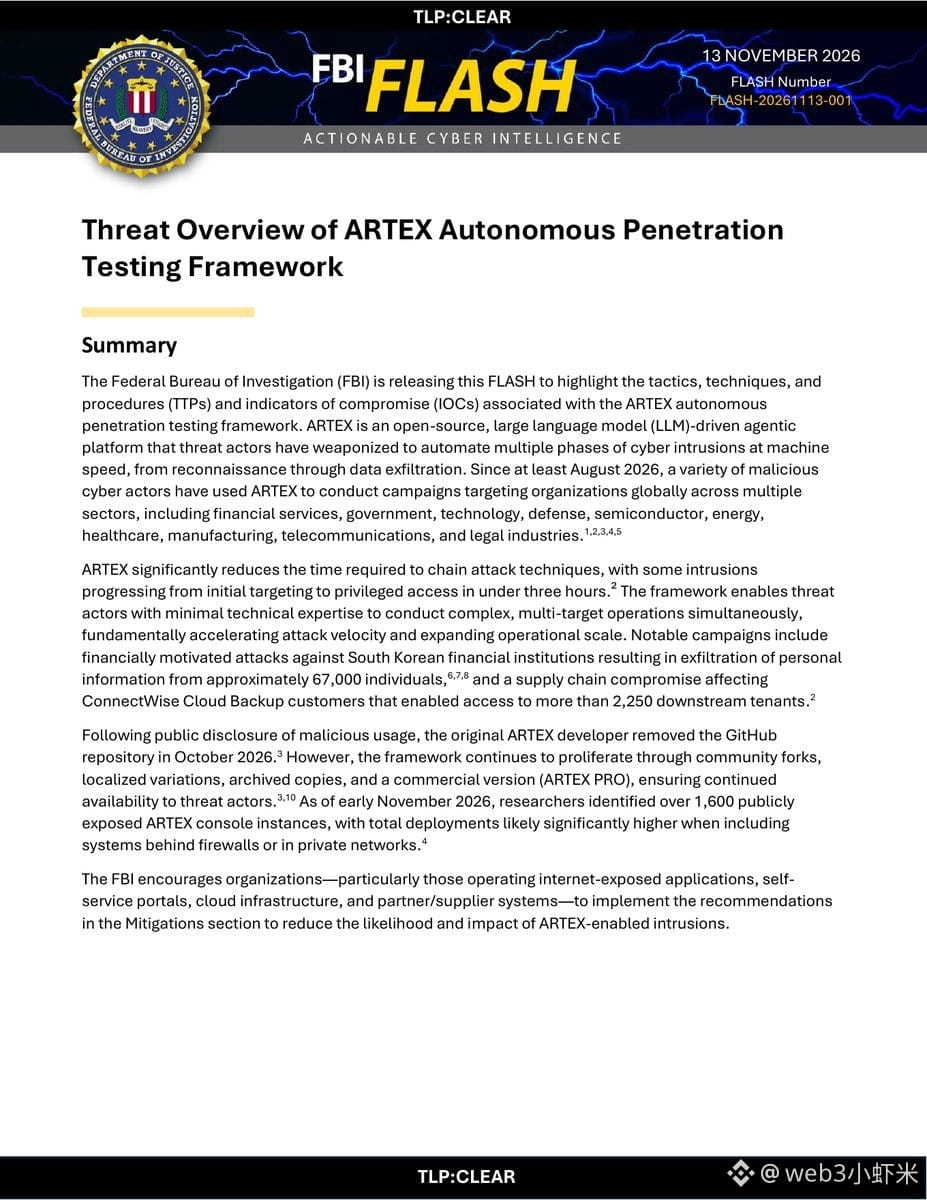
The FBI has just issued a FLASH alert dated November 13, numbered FLASH-20261113-001, specifically warning about an open-source automated penetration-testing framework called ARTEX.
According to the alert, the tool uses large language models to link together every stage of an attack, from reconnaissance to data theft. In some cases, attackers gained elevated privileges in less than three hours. Financial institutions in South Korea have already been hit, with personal information belonging to approximately 67,000 people stolen; a supply-chain incident involving ConnectWise Cloud Backup also affected more than 2,250 downstream tenants.
The original developer took down the GitHub repository in October this year, but the alert says community forks, archived copies, and the commercial ARTEX PRO edition are still circulating. As of early November, more than 1,600 publicly exposed control panels had been identified. The FBI recommends that organizations focus on the exposure of externally facing portals, self-service platforms, cloud systems, and supply-chain-related systems.
#FBI #网络安全 $AI
According to the alert, the tool uses large language models to link together every stage of an attack, from reconnaissance to data theft. In some cases, attackers gained elevated privileges in less than three hours. Financial institutions in South Korea have already been hit, with personal information belonging to approximately 67,000 people stolen; a supply-chain incident involving ConnectWise Cloud Backup also affected more than 2,250 downstream tenants.
The original developer took down the GitHub repository in October this year, but the alert says community forks, archived copies, and the commercial ARTEX PRO edition are still circulating. As of early November, more than 1,600 publicly exposed control panels had been identified. The FBI recommends that organizations focus on the exposure of externally facing portals, self-service platforms, cloud systems, and supply-chain-related systems.
#FBI #网络安全 $AI