5,324 SOL were stolen, and all 181 victims have been fully reimbursed
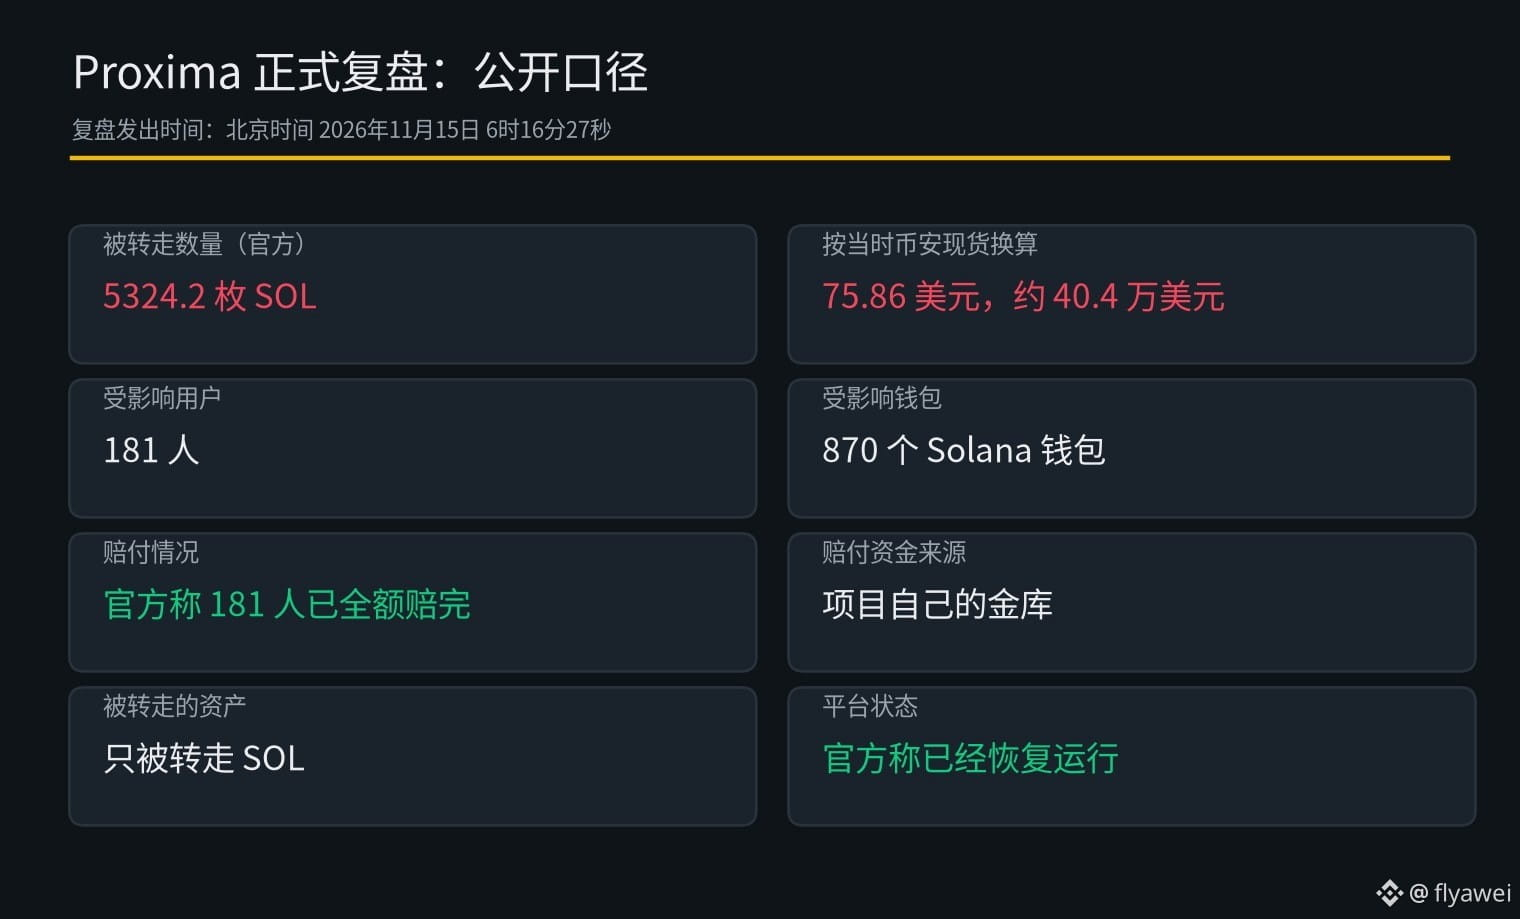
The Proxima project published its official postmortem at 6:16 a.m. Beijing time on November 15. From 11:22 a.m. to 1:42 p.m. on November 14, an attacker stole 5,324.2 SOL from 870 Solana wallets belonging to 181 users. At Binance’s spot price of $75.86 at the time, that was worth about $404,000. All 181 users have been fully reimbursed using funds from the project’s own treasury, and the platform is back up and running.
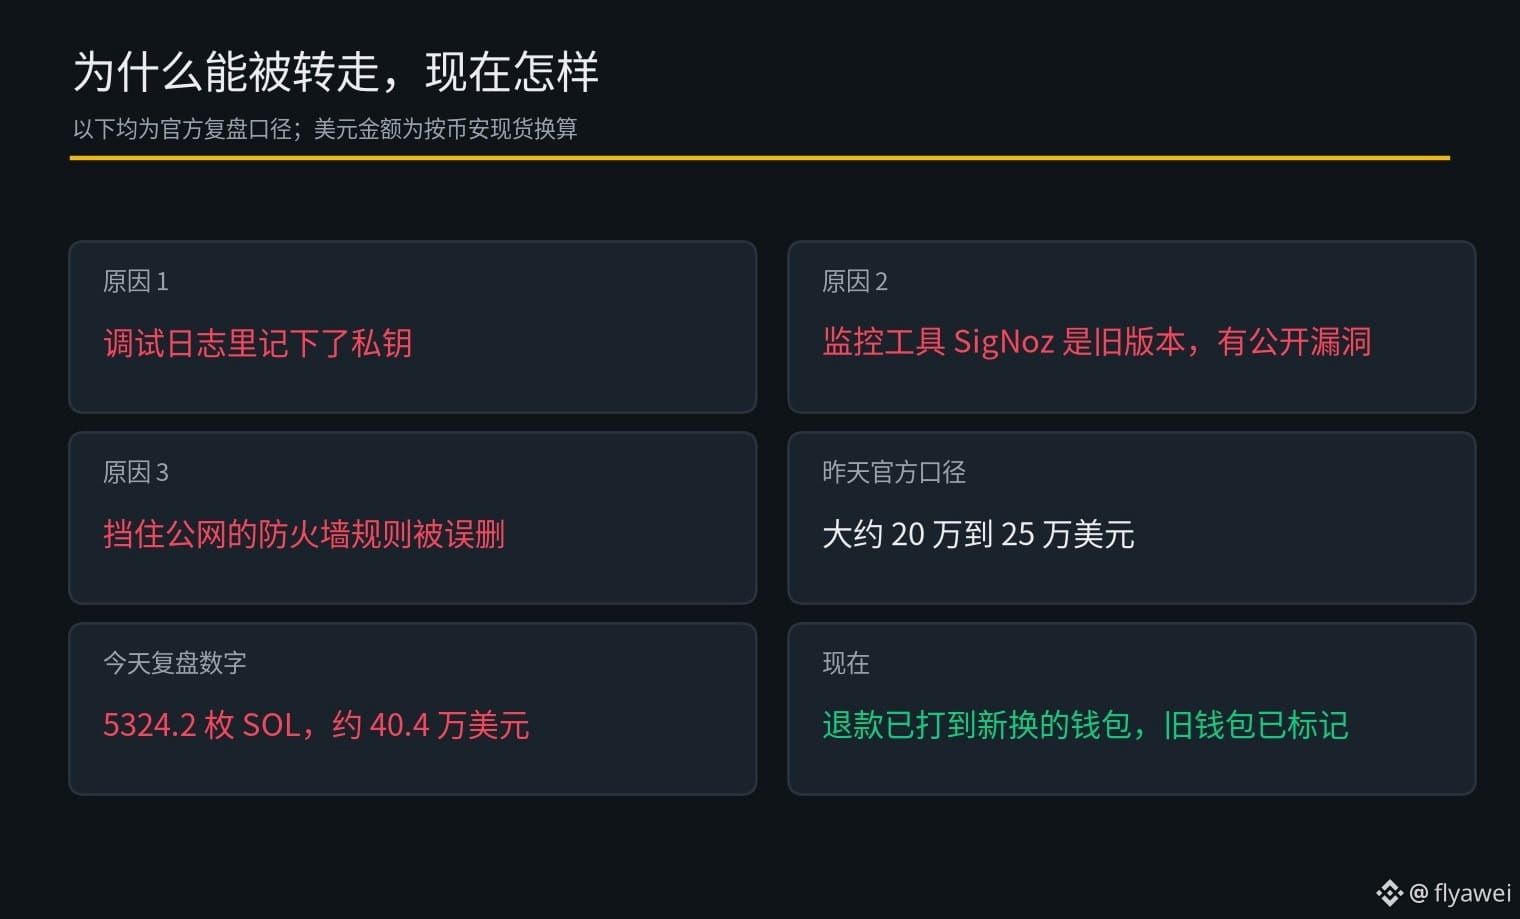
Yesterday, the project said the loss was around $200,000 to $250,000. Today’s figure of 5,324.2 SOL works out to quite a bit more than yesterday’s estimate.
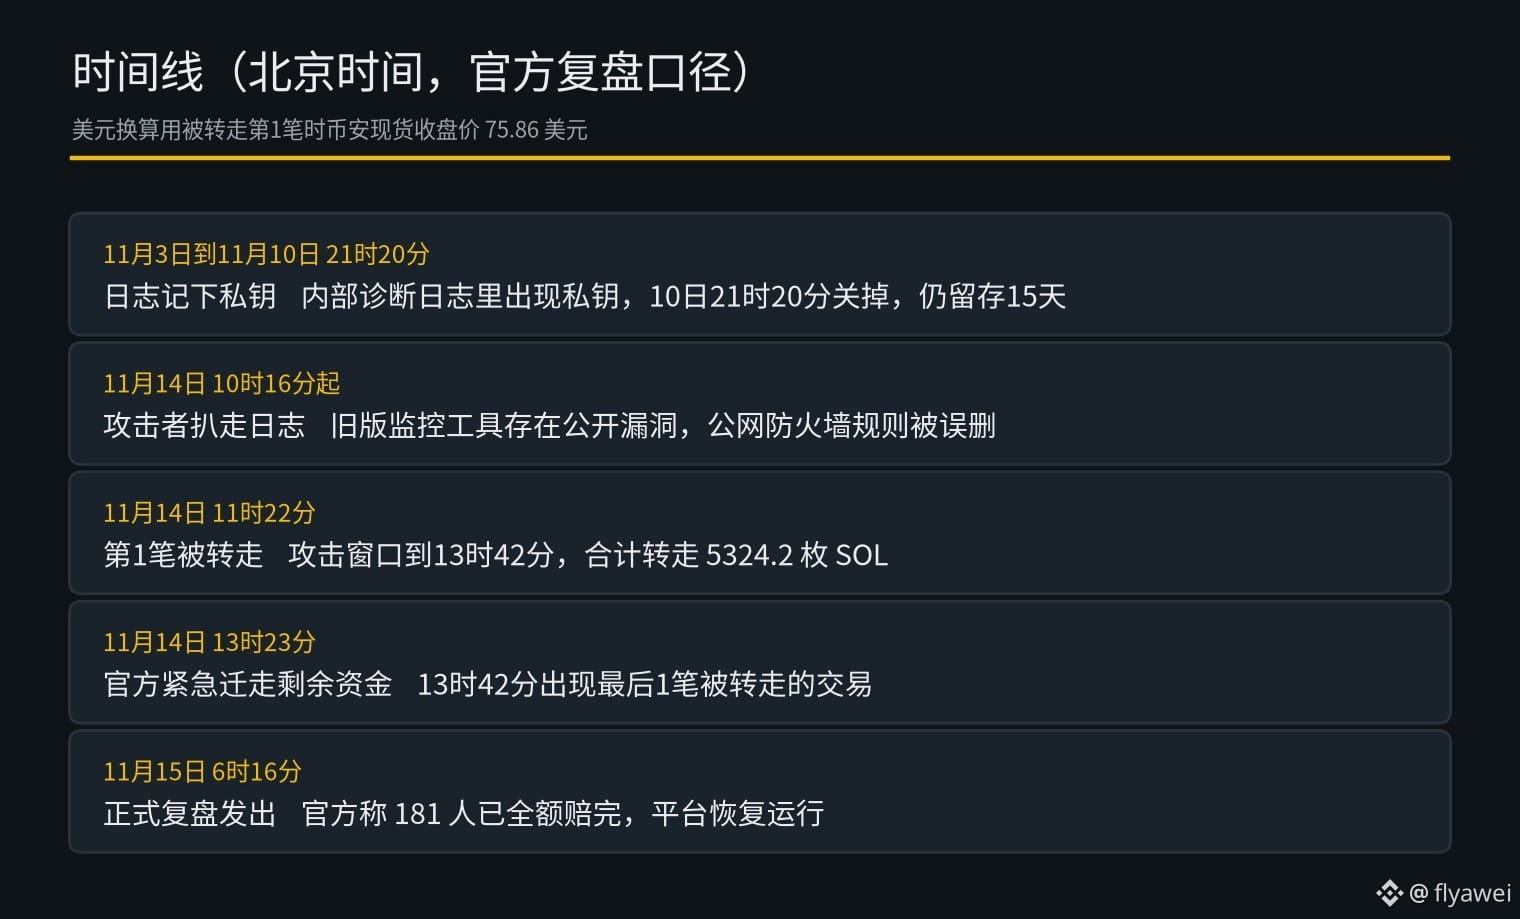
According to the postmortem, private keys were recorded in internal diagnostic logs between November 3 and 9:20 p.m. on November 10. These were debugging logs that made their way into the production environment. The logs were disabled on November 10, but their contents remained stored for a 15-day retention period. The monitoring tool they used, SigNoz, was an outdated version with a publicly known vulnerability, and a firewall rule blocking public internet access had also been accidentally deleted. Starting at 10:16 a.m. on November 14, the attacker scraped the logs while transferring the funds. The first transaction took place at 11:22 a.m. At 1:23 p.m., the project began moving the remaining funds, and the final transaction took place at 1:42 p.m.
The affected wallets have been flagged in the product. The project advises users not to send any more funds to those addresses. Refunds have been sent to newly created replacement wallets. In my view, private keys should never have appeared in monitoring logs in the first place. It’s good that the reimbursements have arrived, but don’t use the old wallets that have been flagged.
Beginners should observe more and trade less. If you’re buying crypto, stick to $BTC
The Proxima project published its official postmortem at 6:16 a.m. Beijing time on November 15. From 11:22 a.m. to 1:42 p.m. on November 14, an attacker stole 5,324.2 SOL from 870 Solana wallets belonging to 181 users. At Binance’s spot price of $75.86 at the time, that was worth about $404,000. All 181 users have been fully reimbursed using funds from the project’s own treasury, and the platform is back up and running.
Yesterday, the project said the loss was around $200,000 to $250,000. Today’s figure of 5,324.2 SOL works out to quite a bit more than yesterday’s estimate.
According to the postmortem, private keys were recorded in internal diagnostic logs between November 3 and 9:20 p.m. on November 10. These were debugging logs that made their way into the production environment. The logs were disabled on November 10, but their contents remained stored for a 15-day retention period. The monitoring tool they used, SigNoz, was an outdated version with a publicly known vulnerability, and a firewall rule blocking public internet access had also been accidentally deleted. Starting at 10:16 a.m. on November 14, the attacker scraped the logs while transferring the funds. The first transaction took place at 11:22 a.m. At 1:23 p.m., the project began moving the remaining funds, and the final transaction took place at 1:42 p.m.
The affected wallets have been flagged in the product. The project advises users not to send any more funds to those addresses. Refunds have been sent to newly created replacement wallets. In my view, private keys should never have appeared in monitoring logs in the first place. It’s good that the reimbursements have arrived, but don’t use the old wallets that have been flagged.
Beginners should observe more and trade less. If you’re buying crypto, stick to $BTC