The Keplr breach isn't over — it just moved to staked tokens, and that's the part nobody warned you about.
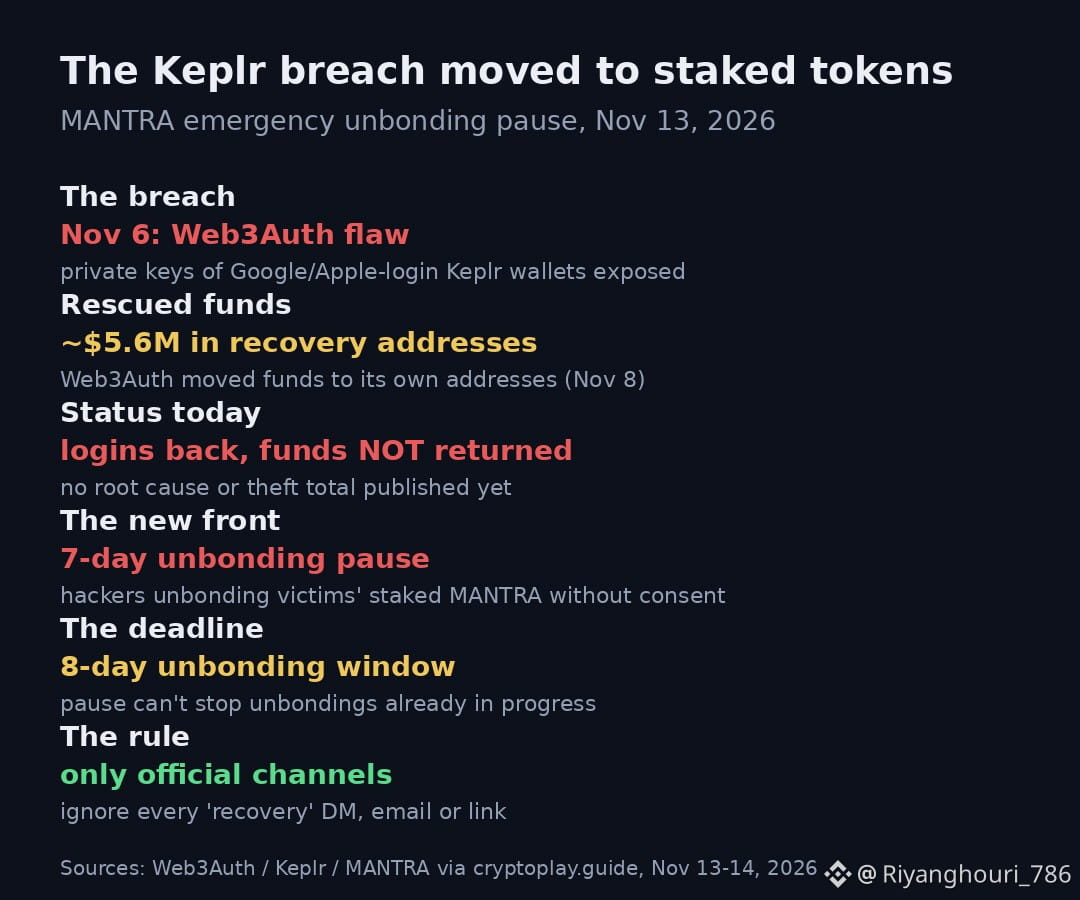
Web3Auth said today that logins are back for existing users, but the funds it rescued still haven't been returned. Meanwhile MANTRA announced yesterday that the attackers are using the exposed keys to unbond victims' staked tokens without consent — after already taking the liquid ones. MANTRA froze several of the hackers' wallets and hit pause on ALL unbonding for 7 days.
Here's the catch that matters if you stake: the pause doesn't stop unbondings that are already in progress. If your staked $OM is being unbonded by someone else, you have to redelegate before the 8-day window closes or those tokens are gone. That's a deadline, not a warning.
About $5.6 million was sitting in Web3Auth's published recovery addresses as of November 8, and neither company has published a root cause or a final theft total yet. If your Keplr wallet was made with a Google or Apple login, check it now — and if you staked MANTRA anywhere, check that too.
The breach happened on November 6. A week later the attackers are still finding new ways to pull money out. If your wallet was made with a social login and you haven't moved what's left yet — what's actually stopping you?
Web3Auth said today that logins are back for existing users, but the funds it rescued still haven't been returned. Meanwhile MANTRA announced yesterday that the attackers are using the exposed keys to unbond victims' staked tokens without consent — after already taking the liquid ones. MANTRA froze several of the hackers' wallets and hit pause on ALL unbonding for 7 days.
Here's the catch that matters if you stake: the pause doesn't stop unbondings that are already in progress. If your staked $OM is being unbonded by someone else, you have to redelegate before the 8-day window closes or those tokens are gone. That's a deadline, not a warning.
About $5.6 million was sitting in Web3Auth's published recovery addresses as of November 8, and neither company has published a root cause or a final theft total yet. If your Keplr wallet was made with a Google or Apple login, check it now — and if you staked MANTRA anywhere, check that too.
The breach happened on November 6. A week later the attackers are still finding new ways to pull money out. If your wallet was made with a social login and you haven't moved what's left yet — what's actually stopping you?