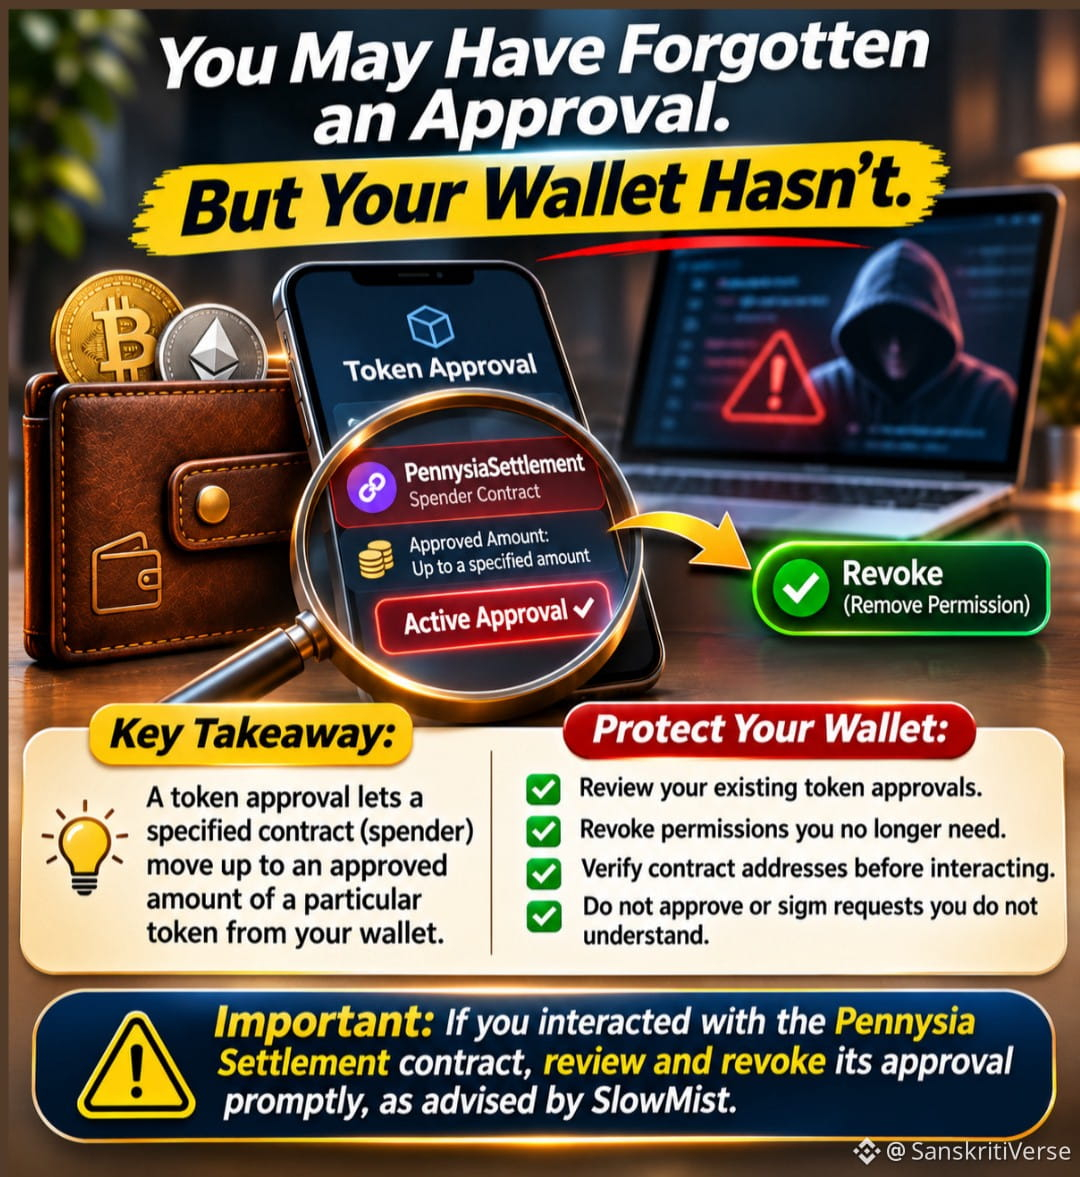
You May Have Forgotten an Approval. But Your Wallet Hasn't.
On November 12, 2026, PennysiaSettlement on Ethereum was exploited through an arbitrary external-call vulnerability in its executeSwap function, according to SlowMist.
The attacker reportedly used fake tokens to bypass spend checks and exploited residual token approvals from 4 users.
Reported loss: Approximately $5,131, recorded by SlowMist.
Why does this matter?
A token approval allows a specified spender contract to move up to an approved amount of a particular token from your wallet.
That permission may remain active even after you stop using a protocol.
Protect Your Wallet:
Review your existing token approvals.
Revoke permissions you no longer need.
Verify contract addresses before interacting.
Do not approve or sign requests you do not understand.
Important: If you interacted with the Pennysia Settlement contract, review and revoke its approval promptly, following SlowMist's security alert.
Beginner Lesson:
Disconnecting your wallet from a website does not automatically revoke token approvals.
Your wallet security also depends on the permissions you have granted.
Question: When did you last review your token approvals?
Source: SlowMist Hacked Database; Pennysia Security Incident Alert.
#CryptoSecurity #WalletSafety #Ethereum #DeFi #CryptoEducation
On November 12, 2026, PennysiaSettlement on Ethereum was exploited through an arbitrary external-call vulnerability in its executeSwap function, according to SlowMist.
The attacker reportedly used fake tokens to bypass spend checks and exploited residual token approvals from 4 users.
Reported loss: Approximately $5,131, recorded by SlowMist.
Why does this matter?
A token approval allows a specified spender contract to move up to an approved amount of a particular token from your wallet.
That permission may remain active even after you stop using a protocol.
Protect Your Wallet:
Review your existing token approvals.
Revoke permissions you no longer need.
Verify contract addresses before interacting.
Do not approve or sign requests you do not understand.
Important: If you interacted with the Pennysia Settlement contract, review and revoke its approval promptly, following SlowMist's security alert.
Beginner Lesson:
Disconnecting your wallet from a website does not automatically revoke token approvals.
Your wallet security also depends on the permissions you have granted.
Question: When did you last review your token approvals?
Source: SlowMist Hacked Database; Pennysia Security Incident Alert.
#CryptoSecurity #WalletSafety #Ethereum #DeFi #CryptoEducation