Damn, hackers stole 900 video clips of people’s faces and scammed them out of over $400 million in 18 months!
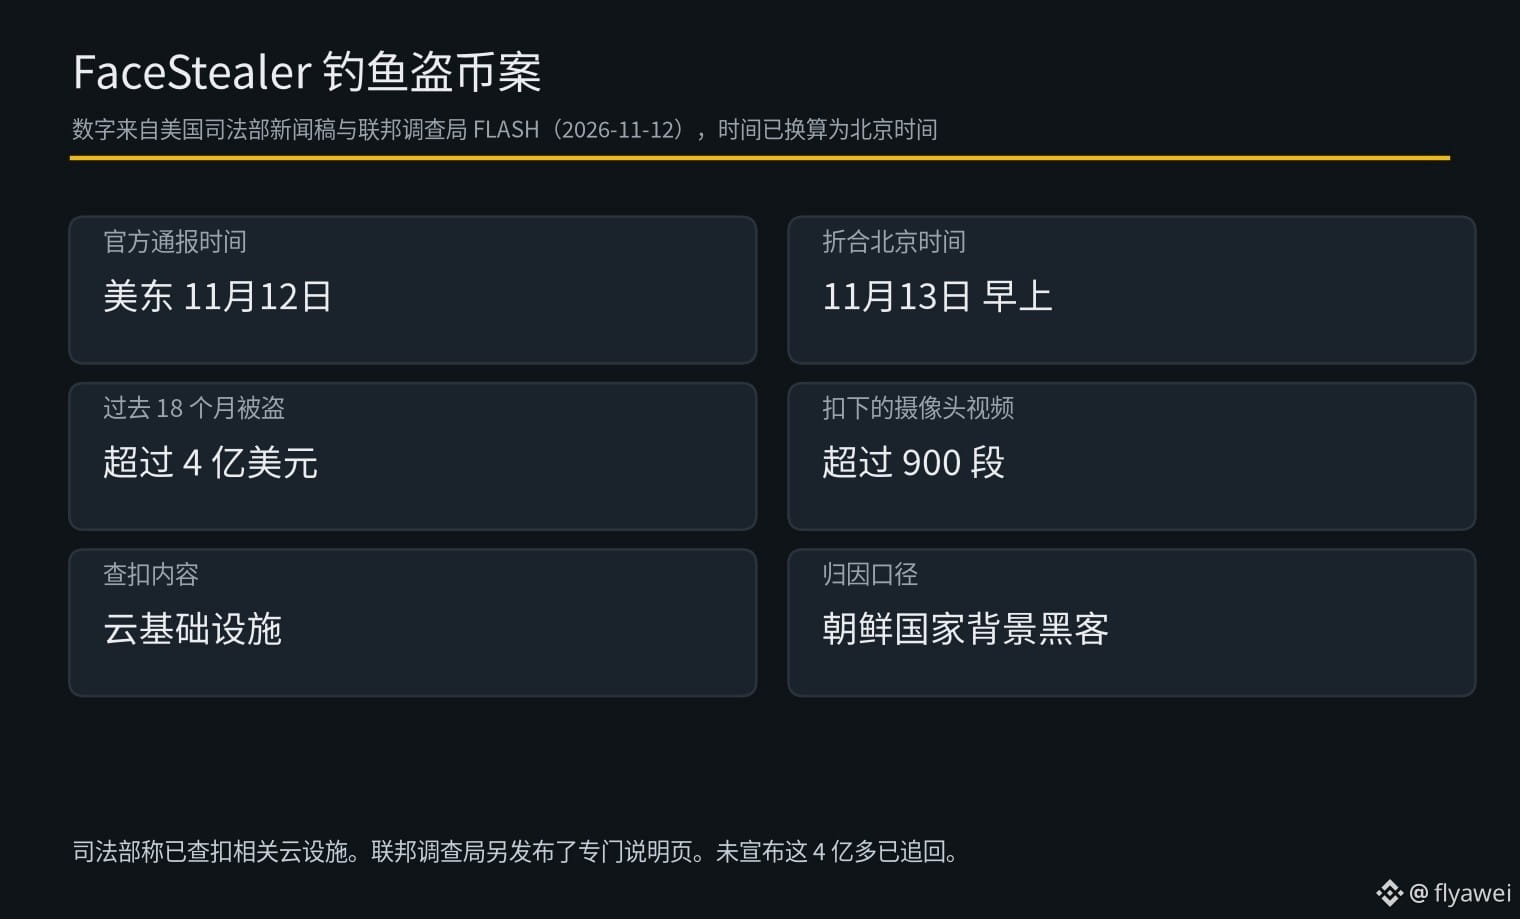
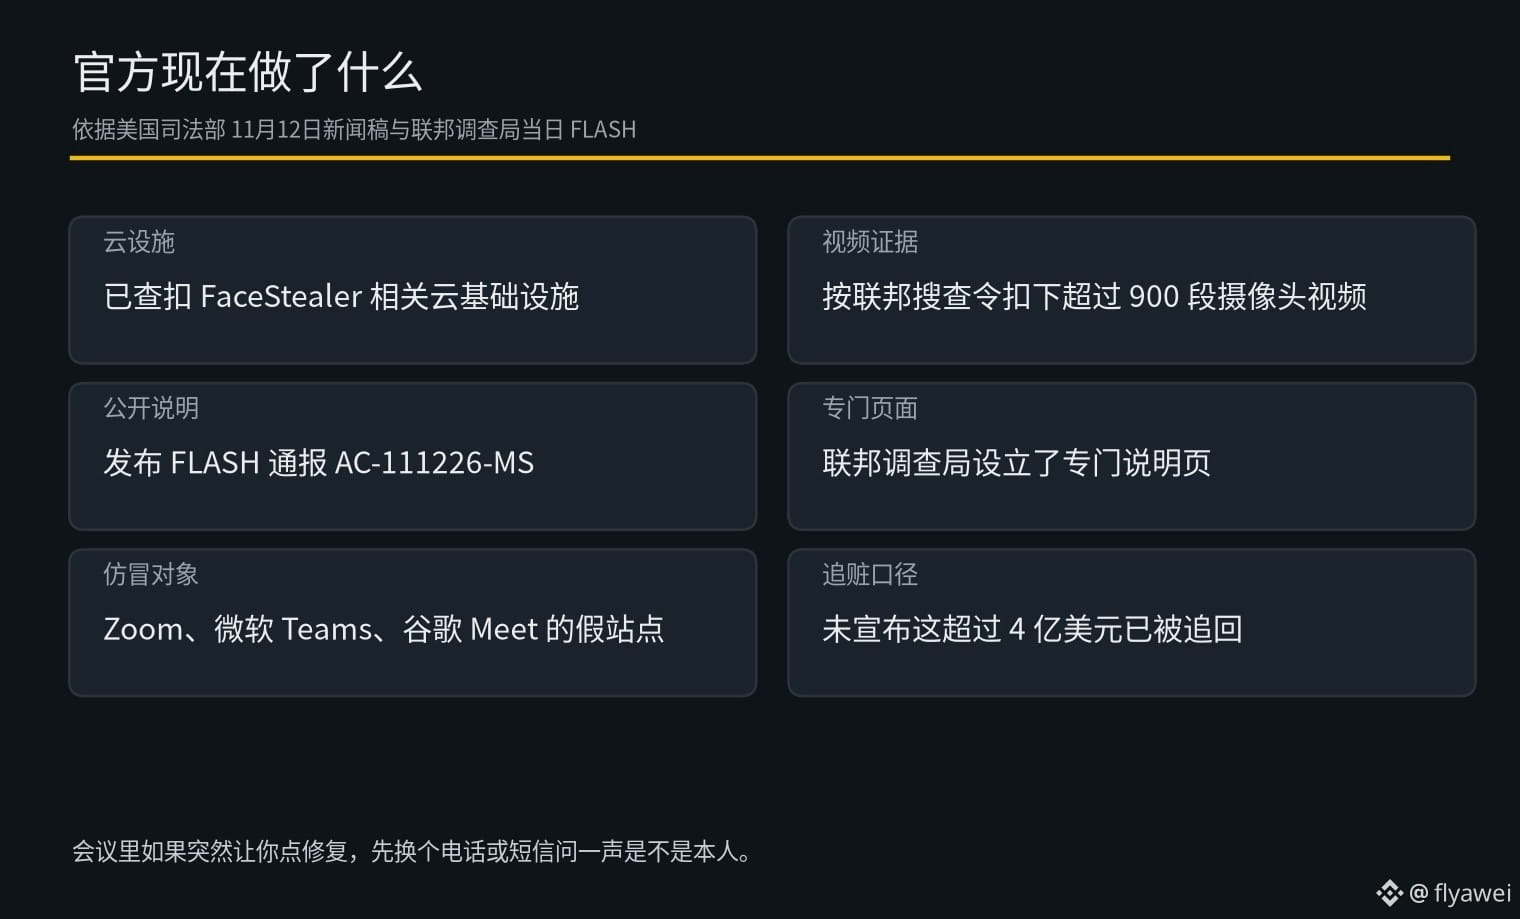
On November 12, U.S. Eastern Time, the U.S. Department of Justice announced that it had seized a cloud infrastructure operation the FBI calls FaceStealer. The FBI says that over the past 18 months, this operation stole more than $400 million in crypto assets from people involved in crypto and Web3, and that it had seized over 900 video clips of victims from their cameras under federal search warrants.
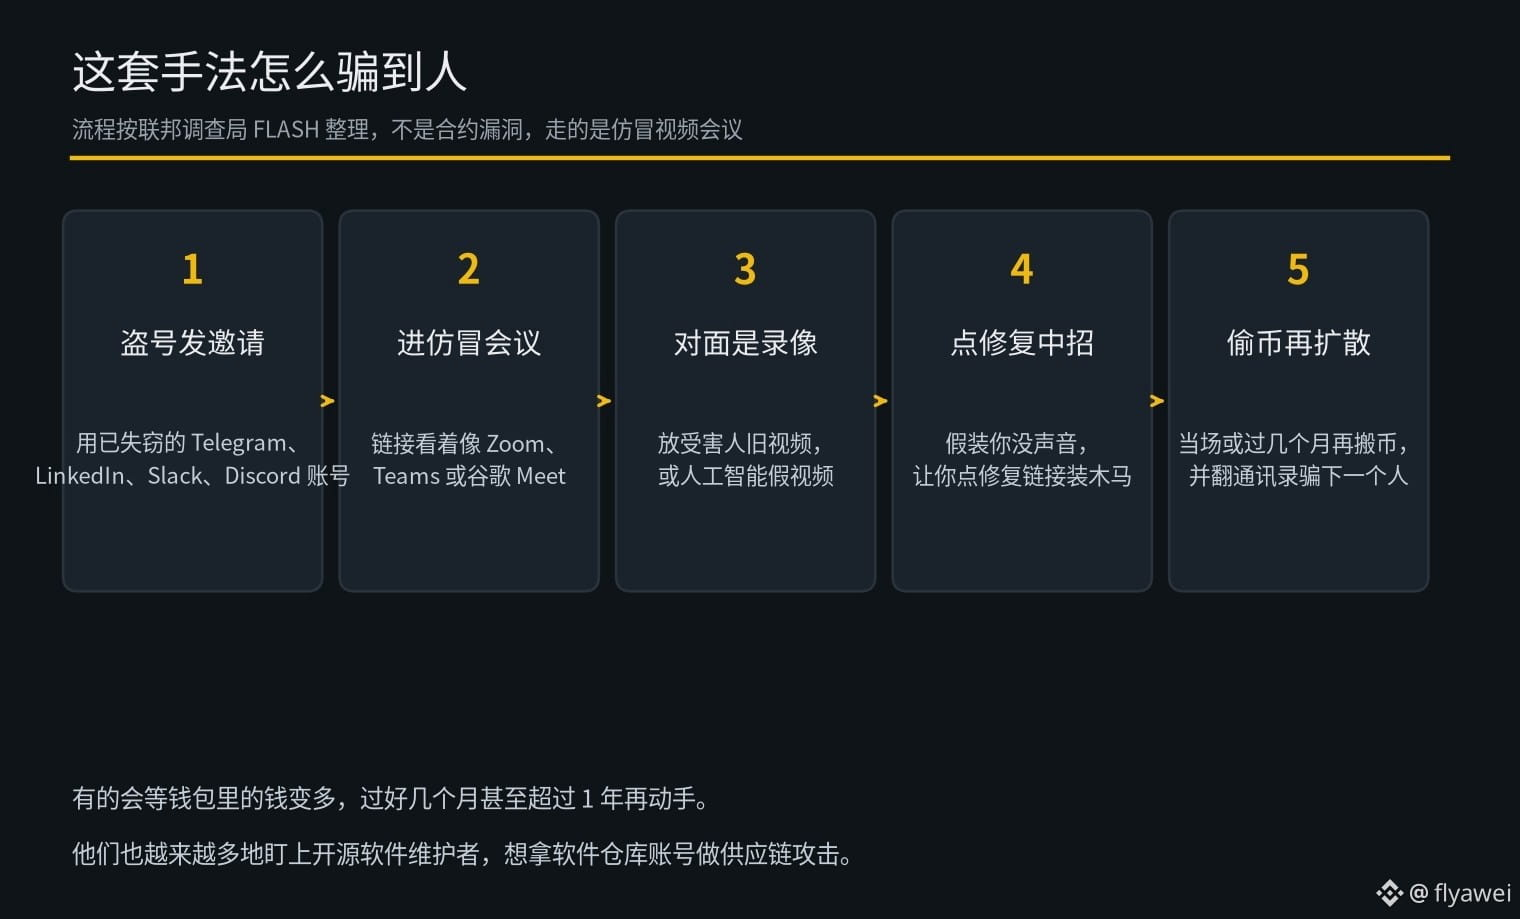
Here’s how it worked. First, they used already-stolen social media or work accounts to send video meeting invites, commonly through Telegram, LinkedIn, Slack, or Discord. The links looked like Zoom, Microsoft Teams, or Google Meet, but actually led to fake websites. Once someone joined, they’d see a recording of a previous victim on the other end. Some calls even featured fake videos of well-known industry figures created with AI. Halfway through the meeting, the scammers would pretend they couldn’t hear you and ask you to click a link to fix the problem—then the malware would get installed.
After taking over a computer, they’d sometimes move the crypto right away. Other times, they’d wait months or even more than a year, until the wallet held more money, before making their move. They’d also go through the victim’s contacts and then scam the next person. The FBI also noted that the group is increasingly targeting open-source software maintainers, hoping to use their software repository accounts for supply-chain attacks.
This scheme exploits trust between people. If someone in a video meeting suddenly asks you to click a link to fix something, it’s best to check with them by phone or text first to make sure it’s really them.
If you’re new to this, watch and learn before you act. If you buy crypto, buy only $BTC
On November 12, U.S. Eastern Time, the U.S. Department of Justice announced that it had seized a cloud infrastructure operation the FBI calls FaceStealer. The FBI says that over the past 18 months, this operation stole more than $400 million in crypto assets from people involved in crypto and Web3, and that it had seized over 900 video clips of victims from their cameras under federal search warrants.
Here’s how it worked. First, they used already-stolen social media or work accounts to send video meeting invites, commonly through Telegram, LinkedIn, Slack, or Discord. The links looked like Zoom, Microsoft Teams, or Google Meet, but actually led to fake websites. Once someone joined, they’d see a recording of a previous victim on the other end. Some calls even featured fake videos of well-known industry figures created with AI. Halfway through the meeting, the scammers would pretend they couldn’t hear you and ask you to click a link to fix the problem—then the malware would get installed.
After taking over a computer, they’d sometimes move the crypto right away. Other times, they’d wait months or even more than a year, until the wallet held more money, before making their move. They’d also go through the victim’s contacts and then scam the next person. The FBI also noted that the group is increasingly targeting open-source software maintainers, hoping to use their software repository accounts for supply-chain attacks.
This scheme exploits trust between people. If someone in a video meeting suddenly asks you to click a link to fix something, it’s best to check with them by phone or text first to make sure it’s really them.
If you’re new to this, watch and learn before you act. If you buy crypto, buy only $BTC