What exactly is a “Merkle tree,” often mentioned in exchange proof of reserves?
In a nutshell: A Merkle tree is a tree-like structure that hashes large amounts of data in pairs and combines them layer by layer. The hash at the very top is called the Merkle root.
Exchange proof of reserves also uses Merkle trees: the platform publishes the root hash, and each user can use their own Merkle path to verify whether their balance has been included.
Remember this instead of memorizing a pile of jargon. Understanding the principle can help you avoid pitfalls, but it can’t replace risk management.
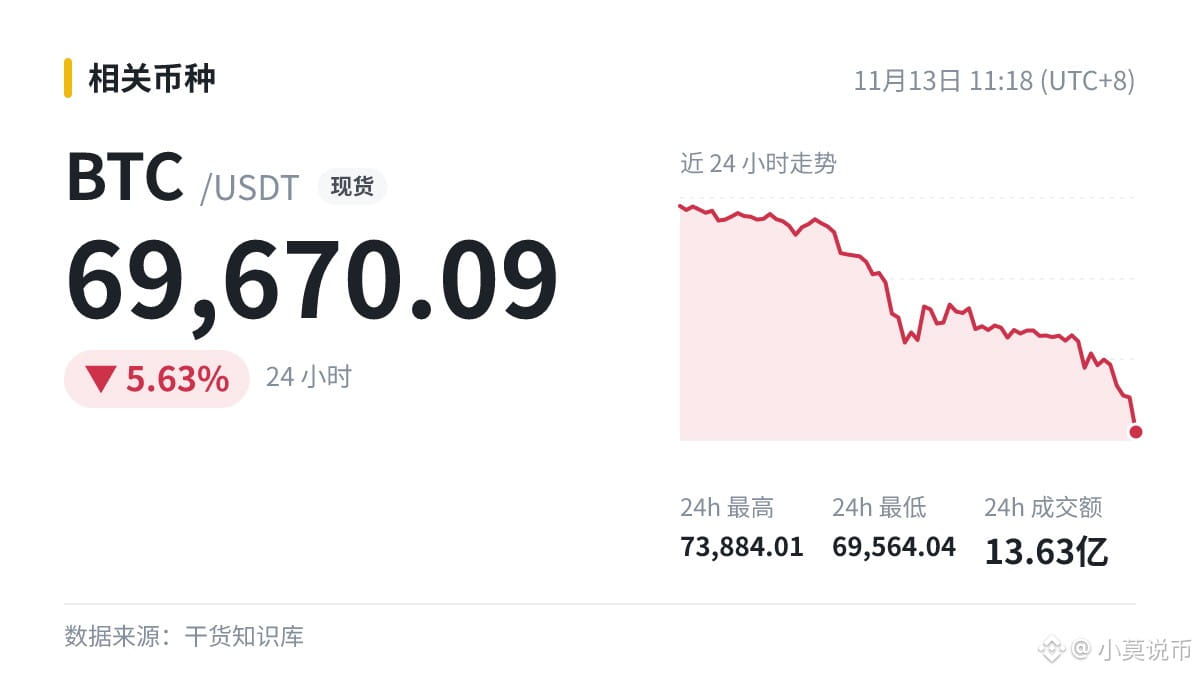
The header of every $BTC block contains a Merkle root that summarizes all the transactions in that block.
You bear the risk yourself; this is just a discussion.
In a nutshell: A Merkle tree is a tree-like structure that hashes large amounts of data in pairs and combines them layer by layer. The hash at the very top is called the Merkle root.
Exchange proof of reserves also uses Merkle trees: the platform publishes the root hash, and each user can use their own Merkle path to verify whether their balance has been included.
Remember this instead of memorizing a pile of jargon. Understanding the principle can help you avoid pitfalls, but it can’t replace risk management.
The header of every $BTC block contains a Merkle root that summarizes all the transactions in that block.
You bear the risk yourself; this is just a discussion.