The keys to 328 apps were exposed, but the assets are still safe
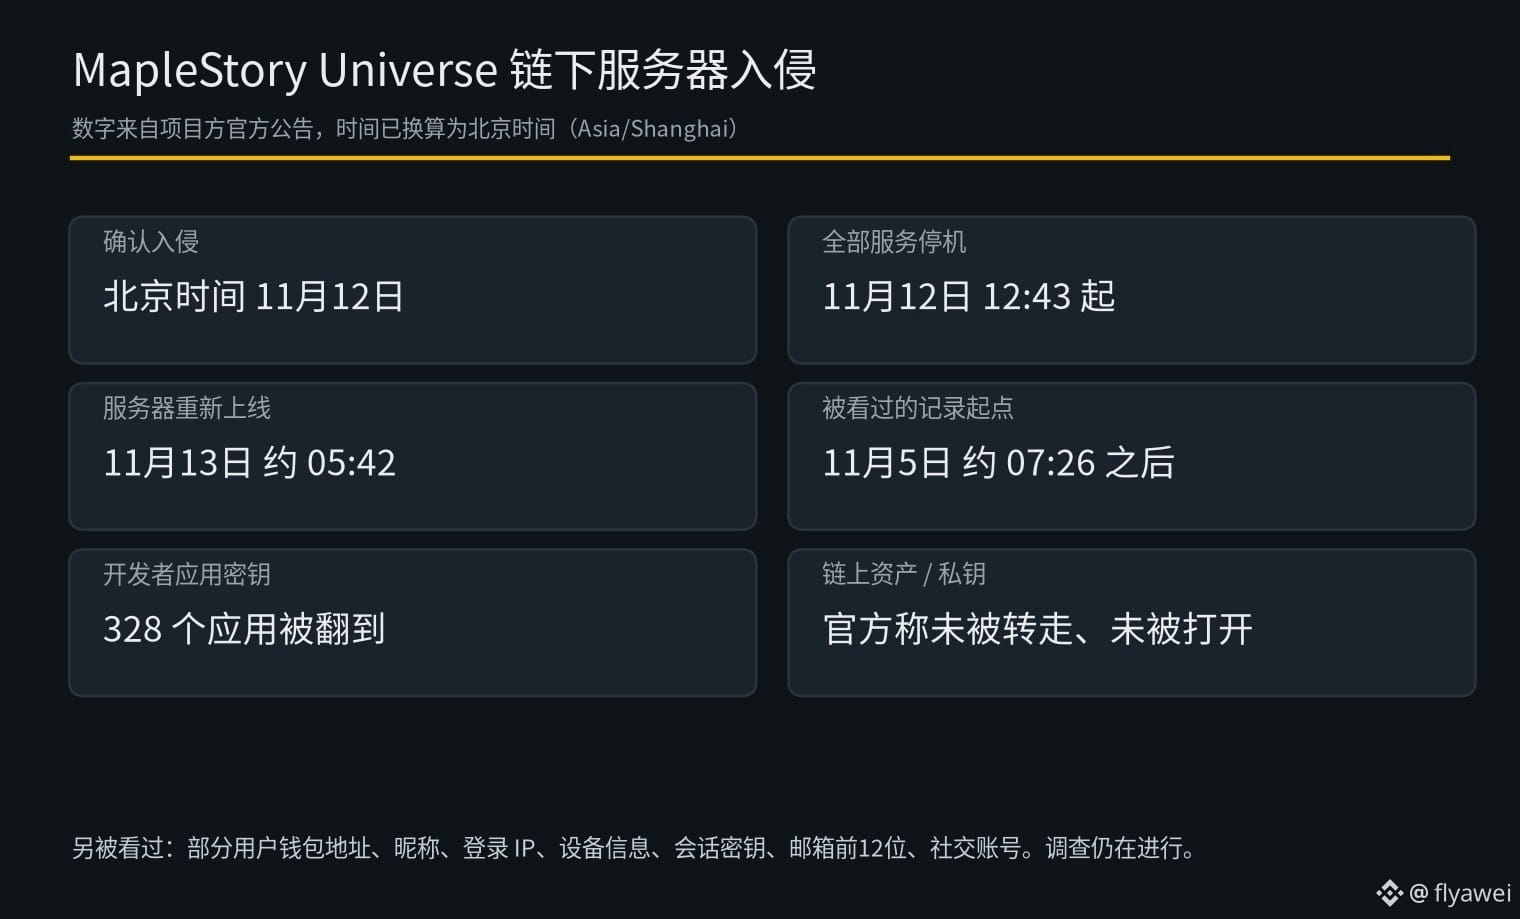
MapleStory Universe, a blockchain gaming project, confirmed on November 12, Beijing time, that some of its off-chain servers had been accessed by an outside party. It shut down all services for emergency maintenance starting at 12:43 that day.
An investigation found that the blockchain and smart contracts had not been altered, and no on-chain assets had been transferred. Users’ private keys were never stored on the project’s servers, and the operational keys capable of moving funds had not been accessed. However, someone viewed a batch of records dating from around 7:26 on November 5, Beijing time. These included some users’ wallet addresses, nicknames, login IP addresses, device information, session keys, the first 12 characters of their email addresses, and linked social media accounts. The wallet addresses, API keys, and login credentials of 328 apps registered in the developer center were also exposed. The team says these API keys cannot be used to access users’ assets. The investigation is ongoing.
They have closed the attack vector and replaced the affected servers. At around 5:42 on November 13, Beijing time, the project announced that its servers were back online. The team says users do not need to change wallets or move their coins for now, but should watch out for phishing attempts using leaked addresses, nicknames, or parts of email addresses.
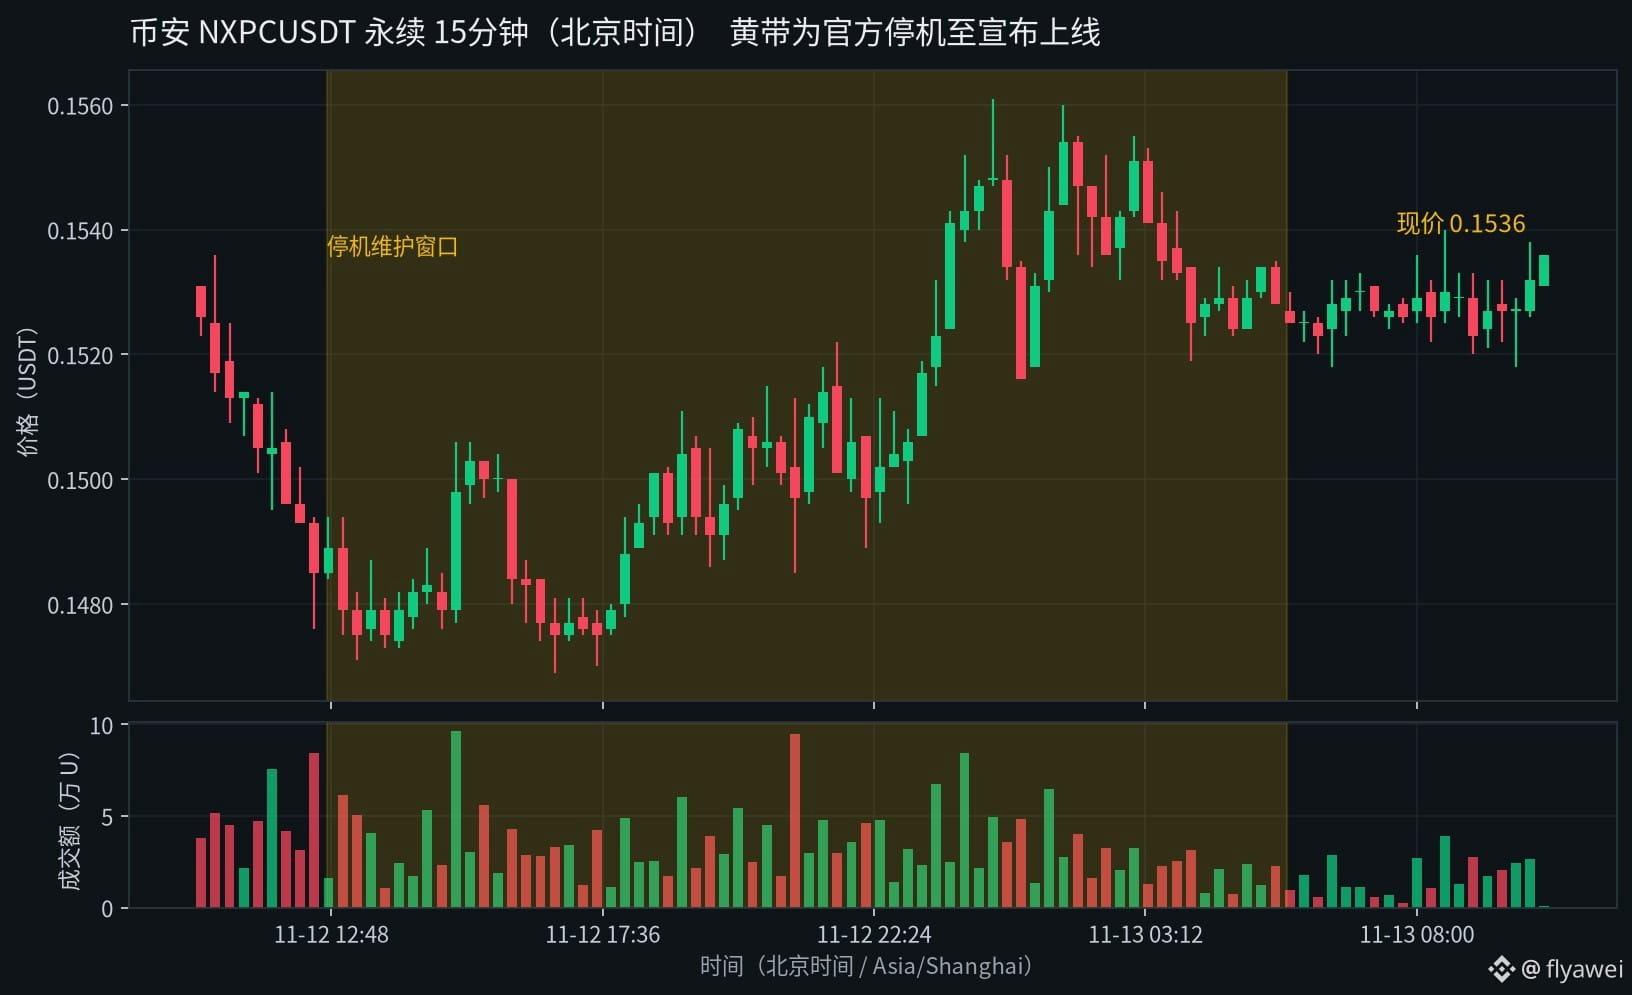
At the time of writing, Binance $NXPC perpetual was trading at around $0.1532, up about 0.20% over the past 24 hours, with roughly 3.08 million U in trading volume. My take is that the fact no coins were transferred doesn’t mean there won’t be trouble later. Once this kind of information gets out, fake customer support and bogus links are likely to follow.
My advice for beginners: watch and learn before taking action, and if you’re buying crypto, stick to $BTC
MapleStory Universe, a blockchain gaming project, confirmed on November 12, Beijing time, that some of its off-chain servers had been accessed by an outside party. It shut down all services for emergency maintenance starting at 12:43 that day.
An investigation found that the blockchain and smart contracts had not been altered, and no on-chain assets had been transferred. Users’ private keys were never stored on the project’s servers, and the operational keys capable of moving funds had not been accessed. However, someone viewed a batch of records dating from around 7:26 on November 5, Beijing time. These included some users’ wallet addresses, nicknames, login IP addresses, device information, session keys, the first 12 characters of their email addresses, and linked social media accounts. The wallet addresses, API keys, and login credentials of 328 apps registered in the developer center were also exposed. The team says these API keys cannot be used to access users’ assets. The investigation is ongoing.
They have closed the attack vector and replaced the affected servers. At around 5:42 on November 13, Beijing time, the project announced that its servers were back online. The team says users do not need to change wallets or move their coins for now, but should watch out for phishing attempts using leaked addresses, nicknames, or parts of email addresses.
At the time of writing, Binance $NXPC perpetual was trading at around $0.1532, up about 0.20% over the past 24 hours, with roughly 3.08 million U in trading volume. My take is that the fact no coins were transferred doesn’t mean there won’t be trouble later. Once this kind of information gets out, fake customer support and bogus links are likely to follow.
My advice for beginners: watch and learn before taking action, and if you’re buying crypto, stick to $BTC