Binance has blocked 57 suspected North Korea-linked cyber threats this year—about one every five days.
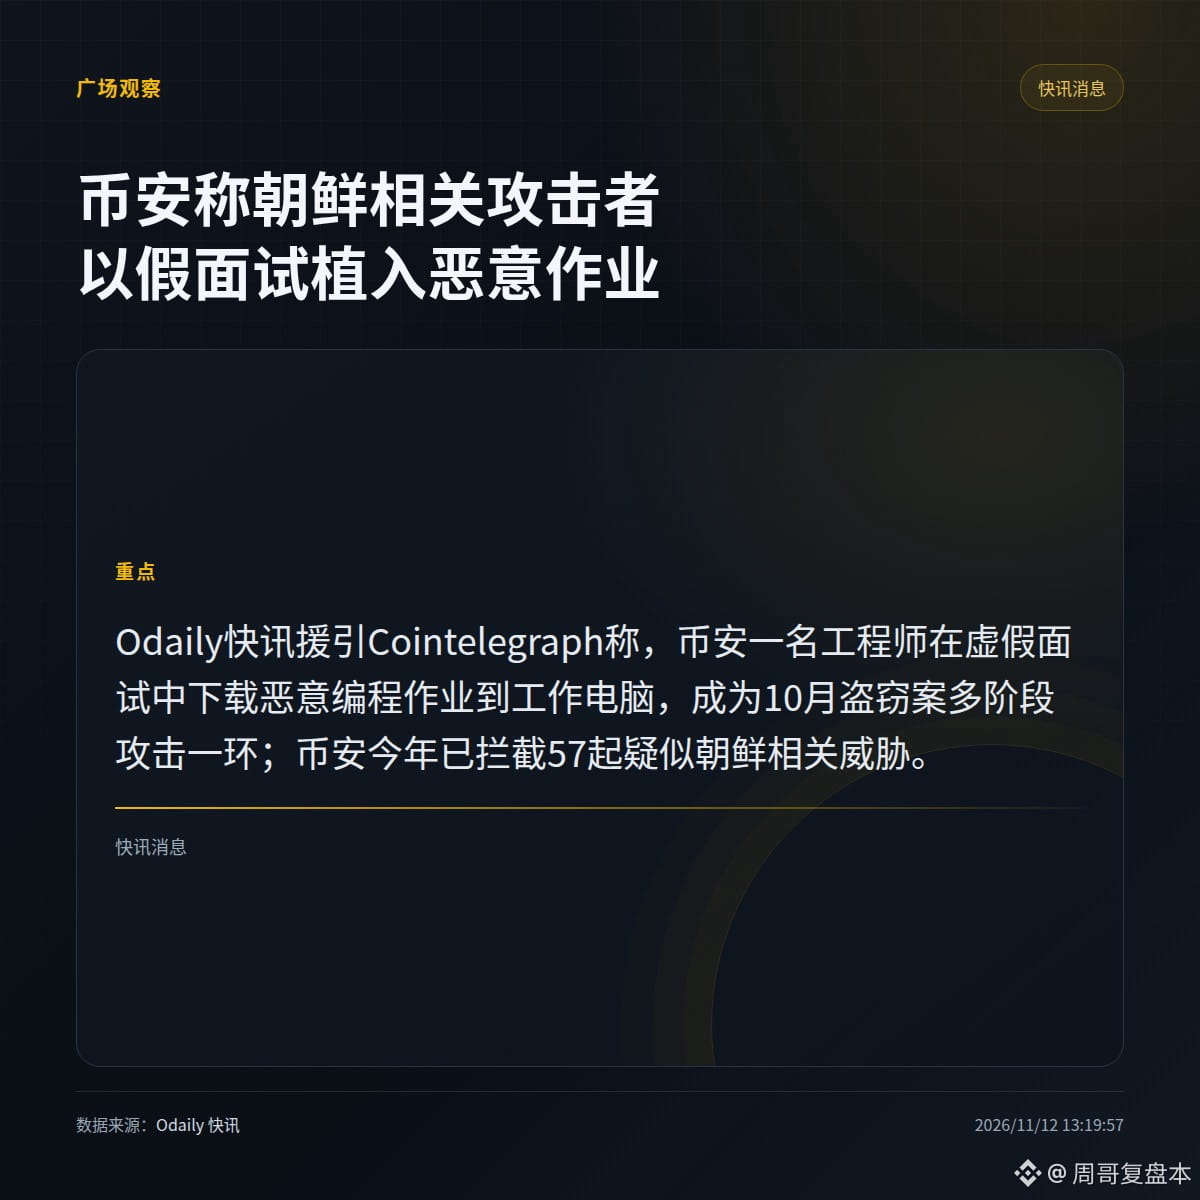
According to an Odaily News flash citing Cointelegraph, Binance Chief Security Officer Jimmy Su warned in a July interview that fake job interviews could trick employees into running malicious code on company devices, allowing attackers to take control of the devices, steal credentials, and infiltrate internal networks. In September, a Binance software engineer downloaded a malicious coding assignment to a work computer during a fake interview. Binance’s preliminary investigation said this was one stage of a multistep attack behind an October theft. The investigation also said the installer evaded endpoint security tools using techniques such as obfuscation. After the incident, Binance said it had strengthened device and access controls, rebuilt the affected wallet systems and internal AI tools, and increased investment in endpoint protection and development environment security.
· The warning came in July, the incident occurred in September, and the theft happened in October; the chronology itself can be verified.
· The claim that the attack bypassed endpoint tools comes from Binance’s subsequent investigation and is its own conclusion.
Does your team allow technical assessments to be run directly on office computers?
According to an Odaily News flash citing Cointelegraph, Binance Chief Security Officer Jimmy Su warned in a July interview that fake job interviews could trick employees into running malicious code on company devices, allowing attackers to take control of the devices, steal credentials, and infiltrate internal networks. In September, a Binance software engineer downloaded a malicious coding assignment to a work computer during a fake interview. Binance’s preliminary investigation said this was one stage of a multistep attack behind an October theft. The investigation also said the installer evaded endpoint security tools using techniques such as obfuscation. After the incident, Binance said it had strengthened device and access controls, rebuilt the affected wallet systems and internal AI tools, and increased investment in endpoint protection and development environment security.
· The warning came in July, the incident occurred in September, and the theft happened in October; the chronology itself can be verified.
· The claim that the attack bypassed endpoint tools comes from Binance’s subsequent investigation and is its own conclusion.
Does your team allow technical assessments to be run directly on office computers?