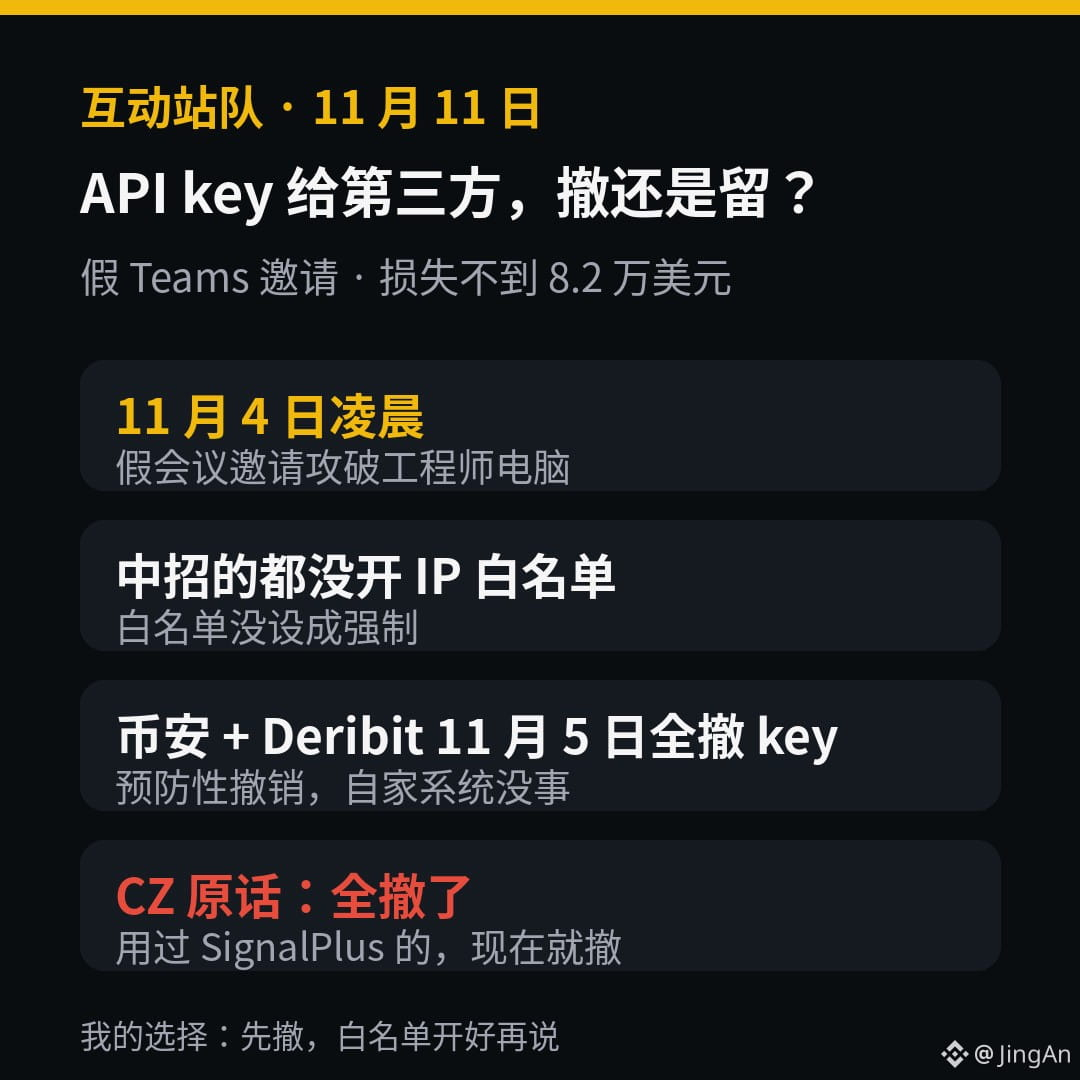
CZ’s exact words: If you’ve used SignalPlus, revoke all your API keys now.
In the early hours of November 4, attackers hijacked the Telegram account of one of SignalPlus’s vendors.
Posing as someone familiar, they sent an engineer a fake Teams meeting invitation.
Once the engineer’s computer was compromised, the attackers gained access to the internal network.
The losses were under $82,000, and SignalPlus said it would reimburse them in full.
On November 5, Binance ($BNB ) and Deribit revoked all SignalPlus keys as a precaution.
The key detail: Every compromised account lacked an IP whitelist.
SignalPlus admitted that whitelist enforcement wasn’t mandatory.
Revoke:
Once you revoke your key, your bots, copy trading, and market monitoring all stop.
Keep it:
Your tools keep running—but next time, your key could be among those stolen from the company you use.
Binance’s advice boils down to three points: Check your positions and open orders directly on the exchange; reconnect only after SignalPlus says the issue is resolved; and always enable an IP whitelist when setting up a key.
I’m choosing to revoke—first I’ll revoke my key, then enable the whitelist.
Which side are you on: revoke or keep?
#APISecurity
In the early hours of November 4, attackers hijacked the Telegram account of one of SignalPlus’s vendors.
Posing as someone familiar, they sent an engineer a fake Teams meeting invitation.
Once the engineer’s computer was compromised, the attackers gained access to the internal network.
The losses were under $82,000, and SignalPlus said it would reimburse them in full.
On November 5, Binance ($BNB ) and Deribit revoked all SignalPlus keys as a precaution.
The key detail: Every compromised account lacked an IP whitelist.
SignalPlus admitted that whitelist enforcement wasn’t mandatory.
Revoke:
Once you revoke your key, your bots, copy trading, and market monitoring all stop.
Keep it:
Your tools keep running—but next time, your key could be among those stolen from the company you use.
Binance’s advice boils down to three points: Check your positions and open orders directly on the exchange; reconnect only after SignalPlus says the issue is resolved; and always enable an IP whitelist when setting up a key.
I’m choosing to revoke—first I’ll revoke my key, then enable the whitelist.
Which side are you on: revoke or keep?
#APISecurity