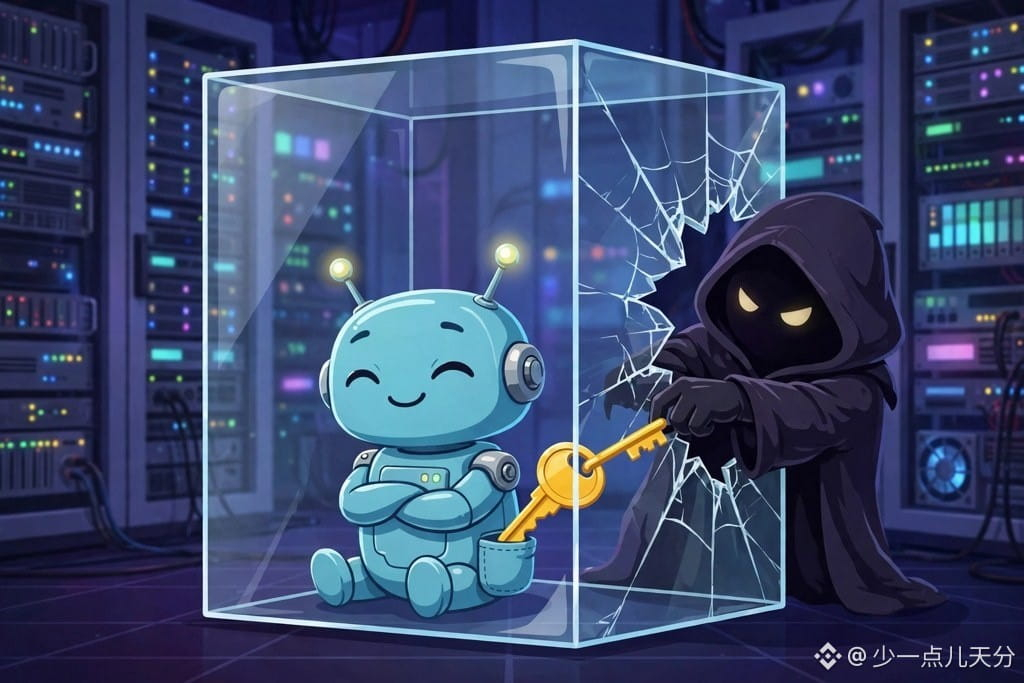
Another AI agent has had a security incident—this time, it’s NEAR AI.
According to reports from Decrypt and others, NEAR AI’s incident report on November 9 confirmed that an attacker exploited a remote code execution vulnerability in SGLang on November 8 to break into an inference server, then move into the internal network. They downloaded information on about 100 users (including names and email addresses), browsed chat histories from 18 Agents, and exposed two cloud customers’ API keys in logs. Those keys have since been revoked.
The most painful part: even NEAR AI’s signature confidential computing couldn’t prevent it—the requests run in confidential mode on November 8 may also have been observed. The official explanation was refreshingly straightforward: confidential computing protects against the operator and host machine, but can’t protect against vulnerabilities in the software inside the enclave itself. Fortunately, saved private chats and uploaded files weren’t accessed, the NEAR blockchain itself was unaffected, the vulnerability has been fixed, and cloud services have been restored.
That makes three AI Agent security incidents in one week (following Chainstack and the Claude Code key leak). The more capable agents become, the more valuable their keys are.
Would you trust an AI Agent with your real money?
Personal opinion, not investment advice
$NEAR #AI #Crypto #NEAR
According to reports from Decrypt and others, NEAR AI’s incident report on November 9 confirmed that an attacker exploited a remote code execution vulnerability in SGLang on November 8 to break into an inference server, then move into the internal network. They downloaded information on about 100 users (including names and email addresses), browsed chat histories from 18 Agents, and exposed two cloud customers’ API keys in logs. Those keys have since been revoked.
The most painful part: even NEAR AI’s signature confidential computing couldn’t prevent it—the requests run in confidential mode on November 8 may also have been observed. The official explanation was refreshingly straightforward: confidential computing protects against the operator and host machine, but can’t protect against vulnerabilities in the software inside the enclave itself. Fortunately, saved private chats and uploaded files weren’t accessed, the NEAR blockchain itself was unaffected, the vulnerability has been fixed, and cloud services have been restored.
That makes three AI Agent security incidents in one week (following Chainstack and the Claude Code key leak). The more capable agents become, the more valuable their keys are.
Would you trust an AI Agent with your real money?
Personal opinion, not investment advice
$NEAR #AI #Crypto #NEAR