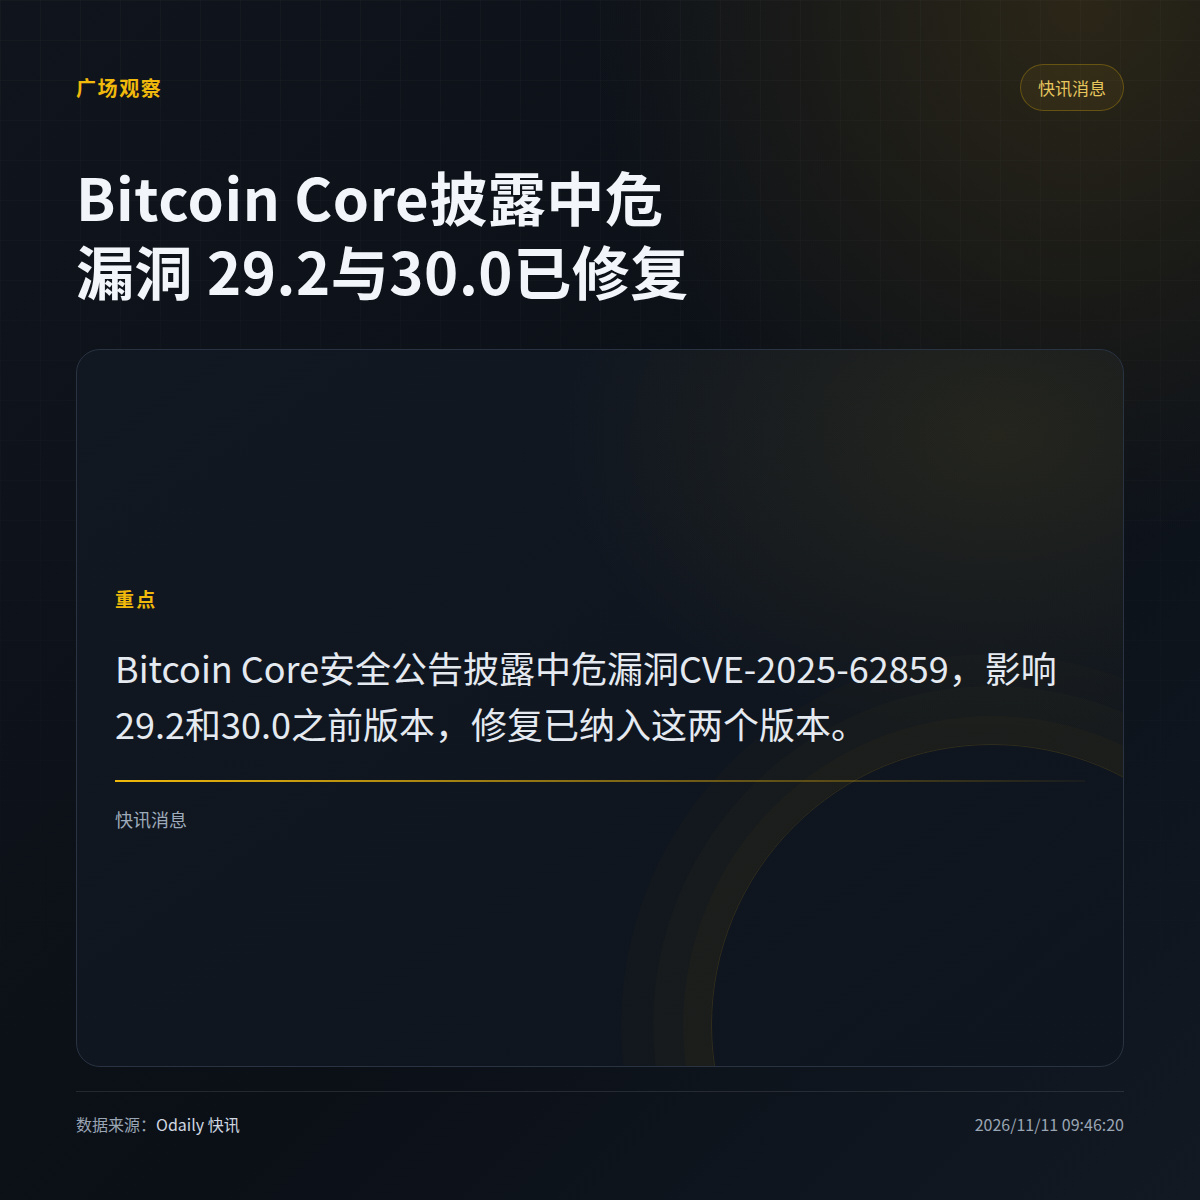
A medium-severity vulnerability, CVE-2025-62859, has been disclosed in Bitcoin Core versions prior to 29.2 and 30.0. It can cause block processing to stall.
According to the security advisory, malicious nodes can trigger the issue by tampering with witness data in compact blocks: after reconstructing a compact block, affected nodes clear the download state before checking the witness data. If the check fails, they request the full block from the same node and wait for a 10-minute timeout. The attack can be repeated indefinitely if an attacker controls three of the victim’s high-bandwidth peers, or if the victim is running in -blockonly mode.
The vulnerability was disclosed on November 10, 2026, and fixes are included in versions 29.2 and 30.0. The vulnerability only applies when the peer conditions described above are met or the node is running in a specific mode, so not all nodes are affected.
Is the version of your node 29.2 or 30.0 or later?
According to the security advisory, malicious nodes can trigger the issue by tampering with witness data in compact blocks: after reconstructing a compact block, affected nodes clear the download state before checking the witness data. If the check fails, they request the full block from the same node and wait for a 10-minute timeout. The attack can be repeated indefinitely if an attacker controls three of the victim’s high-bandwidth peers, or if the victim is running in -blockonly mode.
The vulnerability was disclosed on November 10, 2026, and fixes are included in versions 29.2 and 30.0. The vulnerability only applies when the peer conditions described above are met or the node is running in a specific mode, so not all nodes are affected.
Is the version of your node 29.2 or 30.0 or later?