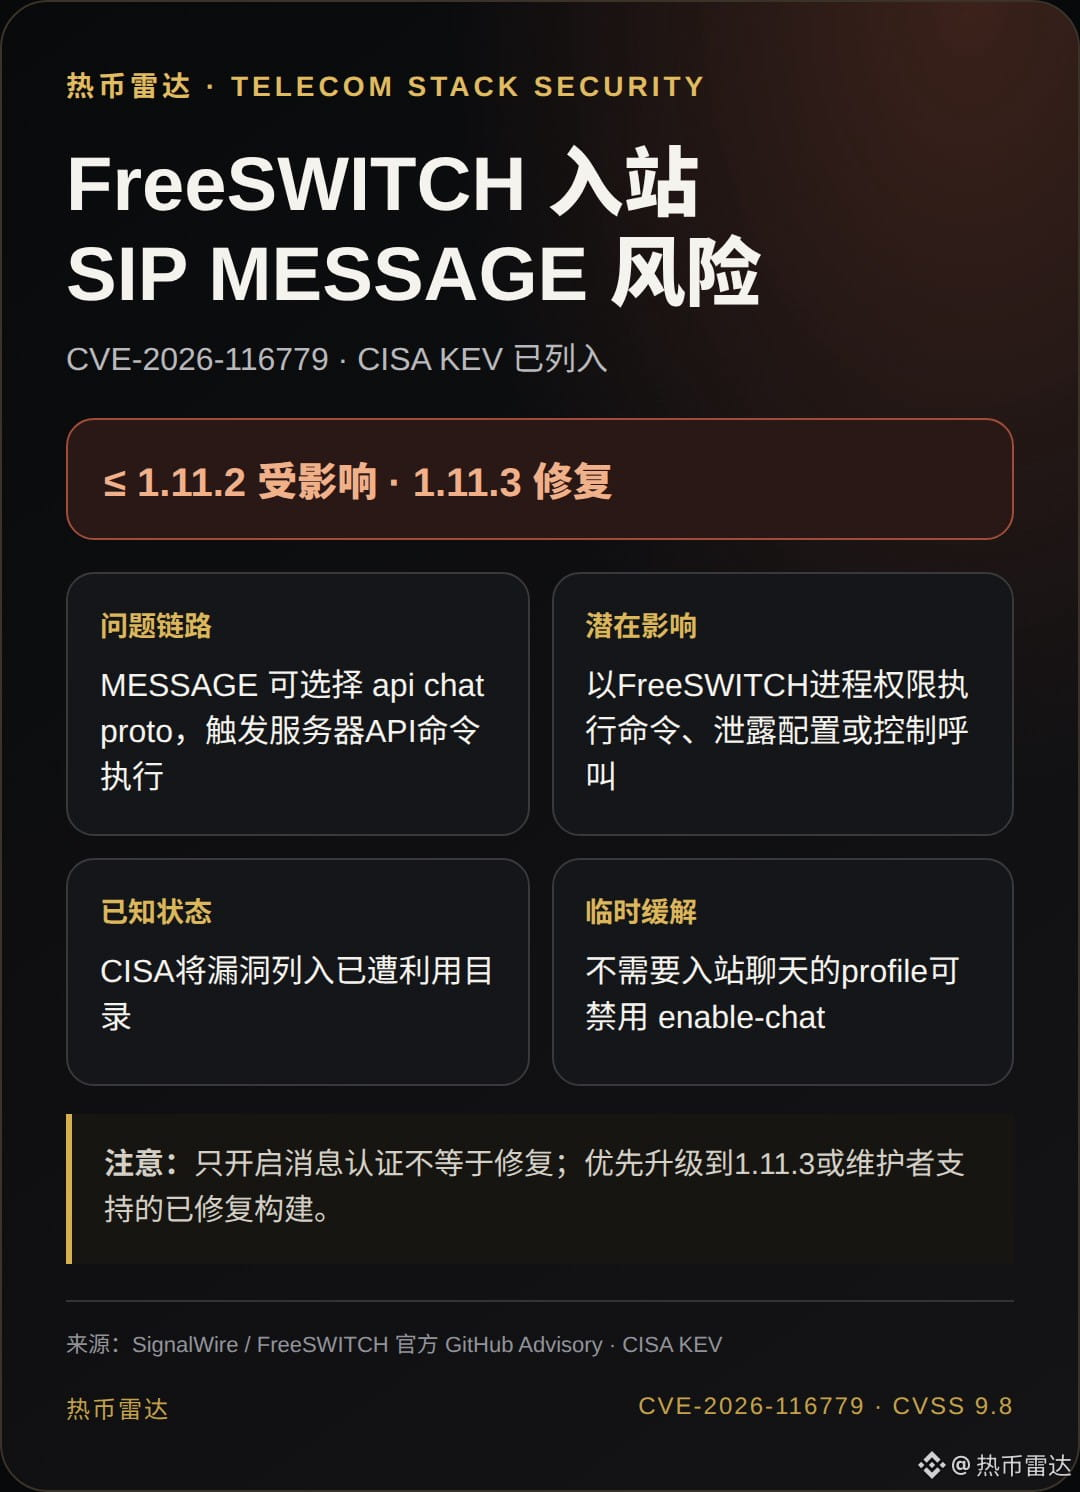
FreeSWITCH inbound SIP MESSAGE is more than a chat risk: a maintainer advisory notes that version 1.11.2 and earlier allow messages to select the `api` chat proto, triggering the server to execute API/OS commands with the privileges of the FreeSWITCH process; CISA has added CVE-2026-116779 to its Known Exploited Vulnerabilities Catalog. The official fix is version 1.11.3; for profiles that cannot upgrade yet and do not need inbound chat, the maintainers recommend disabling `enable-chat`. Enabling message authentication alone does not fully block this attack path. Sources: https://github.com/signalwire/freeswitch/security/advisories/GHSA-mg63-h38w-8p9p; https://www.cisa.gov/known-exploited-vulnerabilities-catalog
This article may be eligible for Binance Square Write to Earn content rewards, subject to the platform’s eligibility requirements and rules; it does not constitute trading advice.
This article may be eligible for Binance Square Write to Earn content rewards, subject to the platform’s eligibility requirements and rules; it does not constitute trading advice.