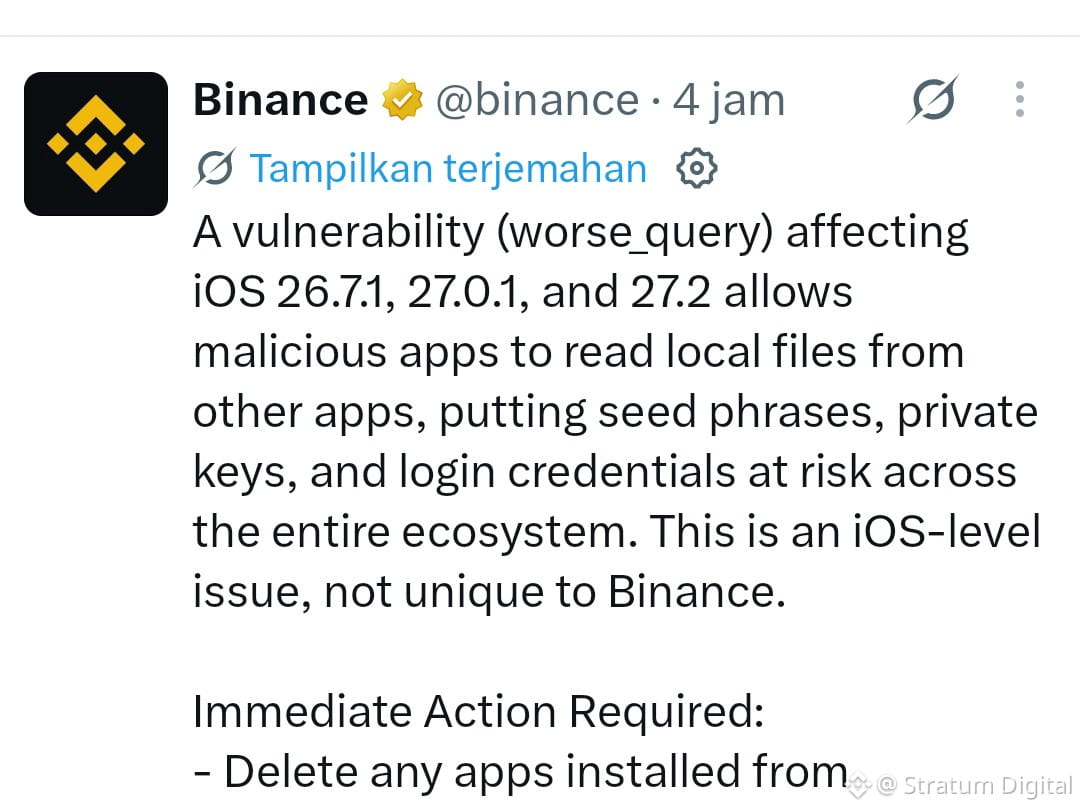
A vulnerability (worse_query) affecting iOS 26.7.1, 27.0.1, and 27.2 allows malicious apps to read local files from other apps, putting seed phrases, private keys, and login credentials across the ecosystem at risk. This is an iOS-level issue, not specific to Binance.
Immediate action required:
- Remove any apps installed from untrusted sources (such as sideloaded apps or manually signed IPAs).
- Update iOS and all apps to the latest official versions.
- If you suspect a breach, transfer funds to a new wallet created on a clean device and reset all active login sessions.
Never install unauthorized packages, and keep your software up to date.
$BTC $INIT
Immediate action required:
- Remove any apps installed from untrusted sources (such as sideloaded apps or manually signed IPAs).
- Update iOS and all apps to the latest official versions.
- If you suspect a breach, transfer funds to a new wallet created on a clean device and reset all active login sessions.
Never install unauthorized packages, and keep your software up to date.
$BTC $INIT