IOS 27.2 has a “sandbox escape” vulnerability
⚠️ Upgrade to IOS 27.2.1 as soon as possible
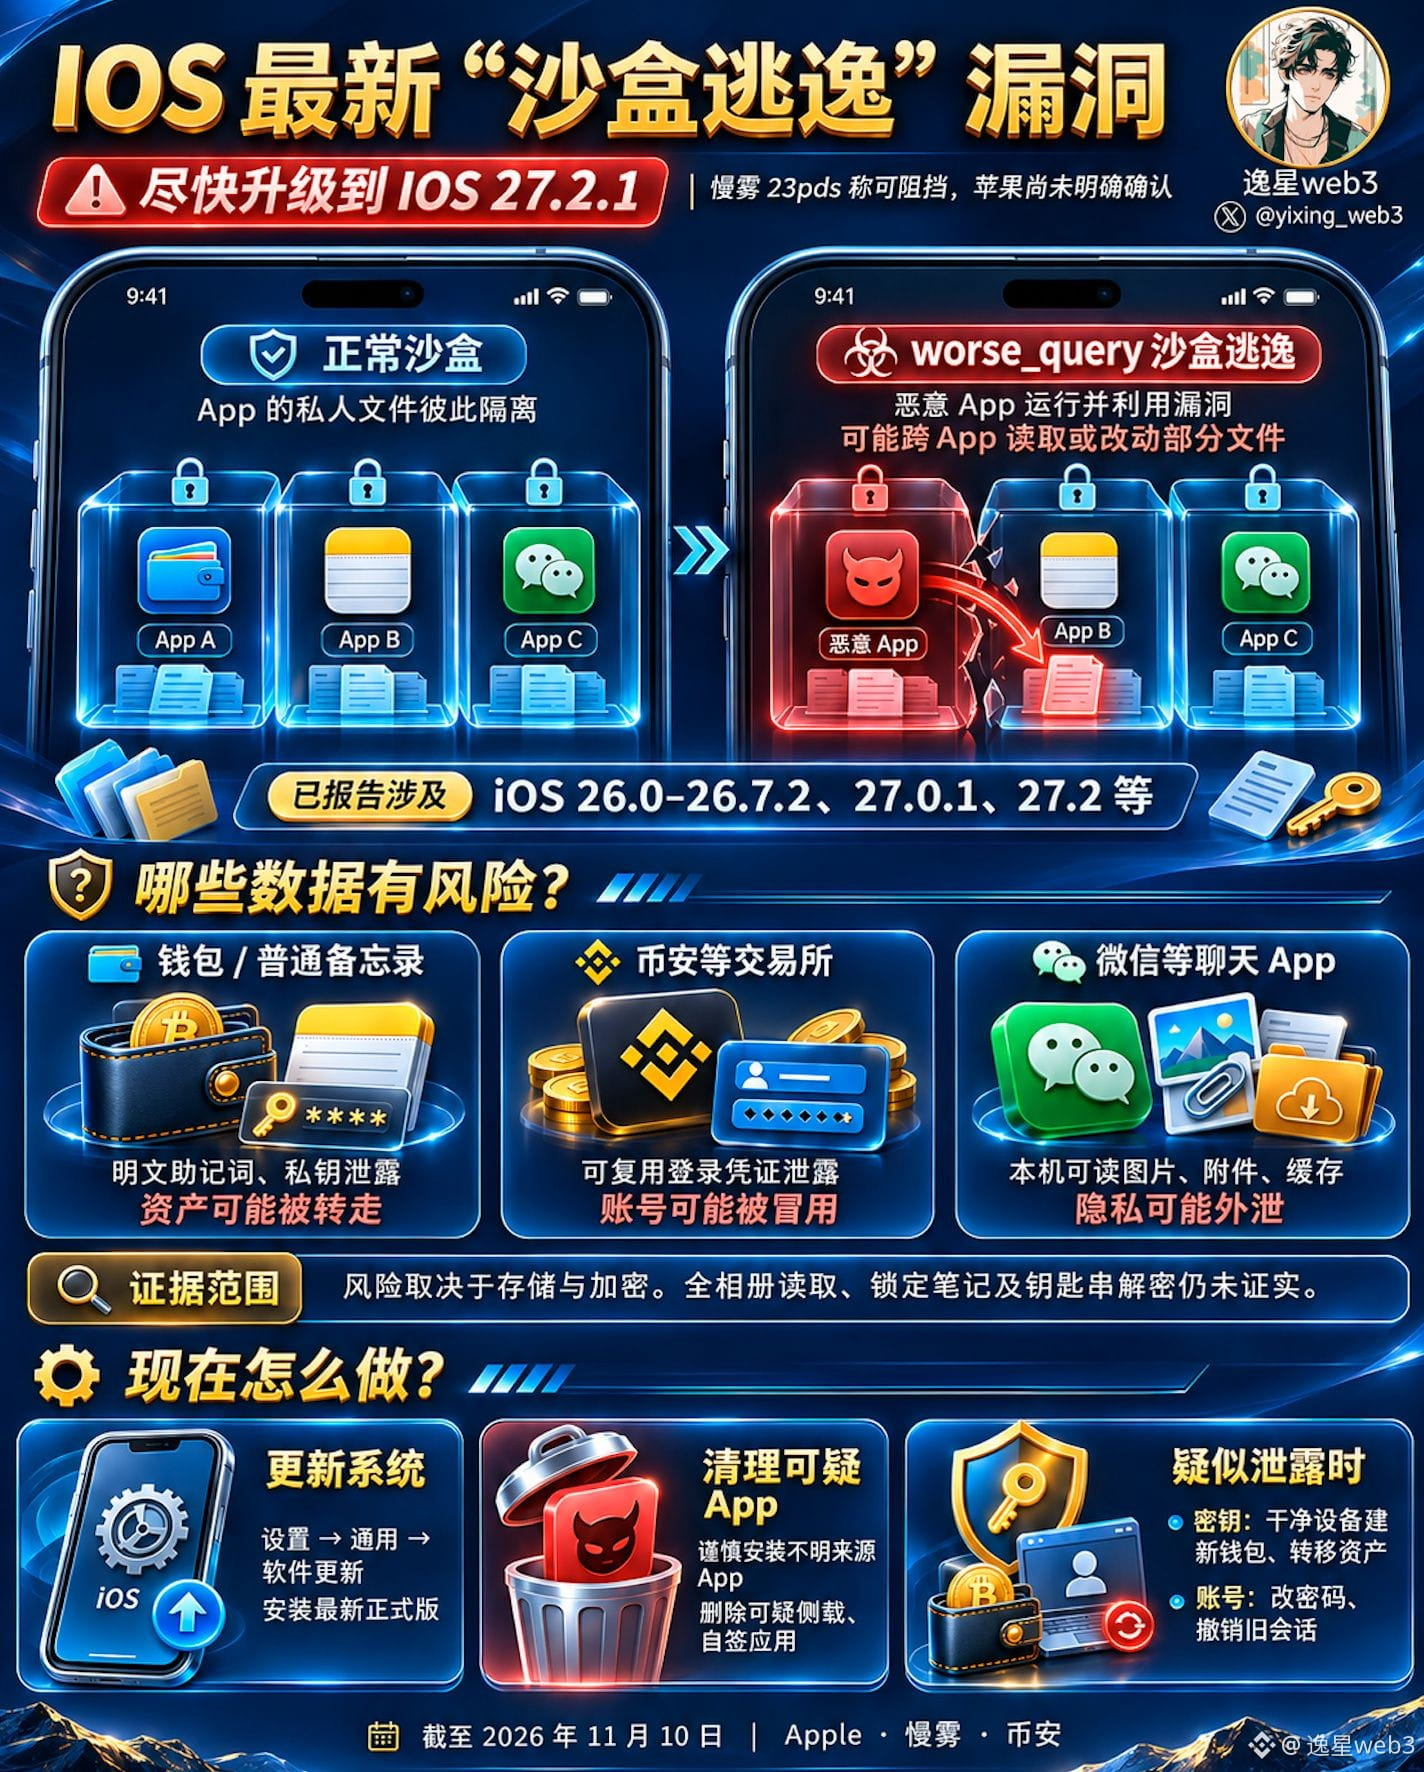
Normally, data is isolated between iOS apps.
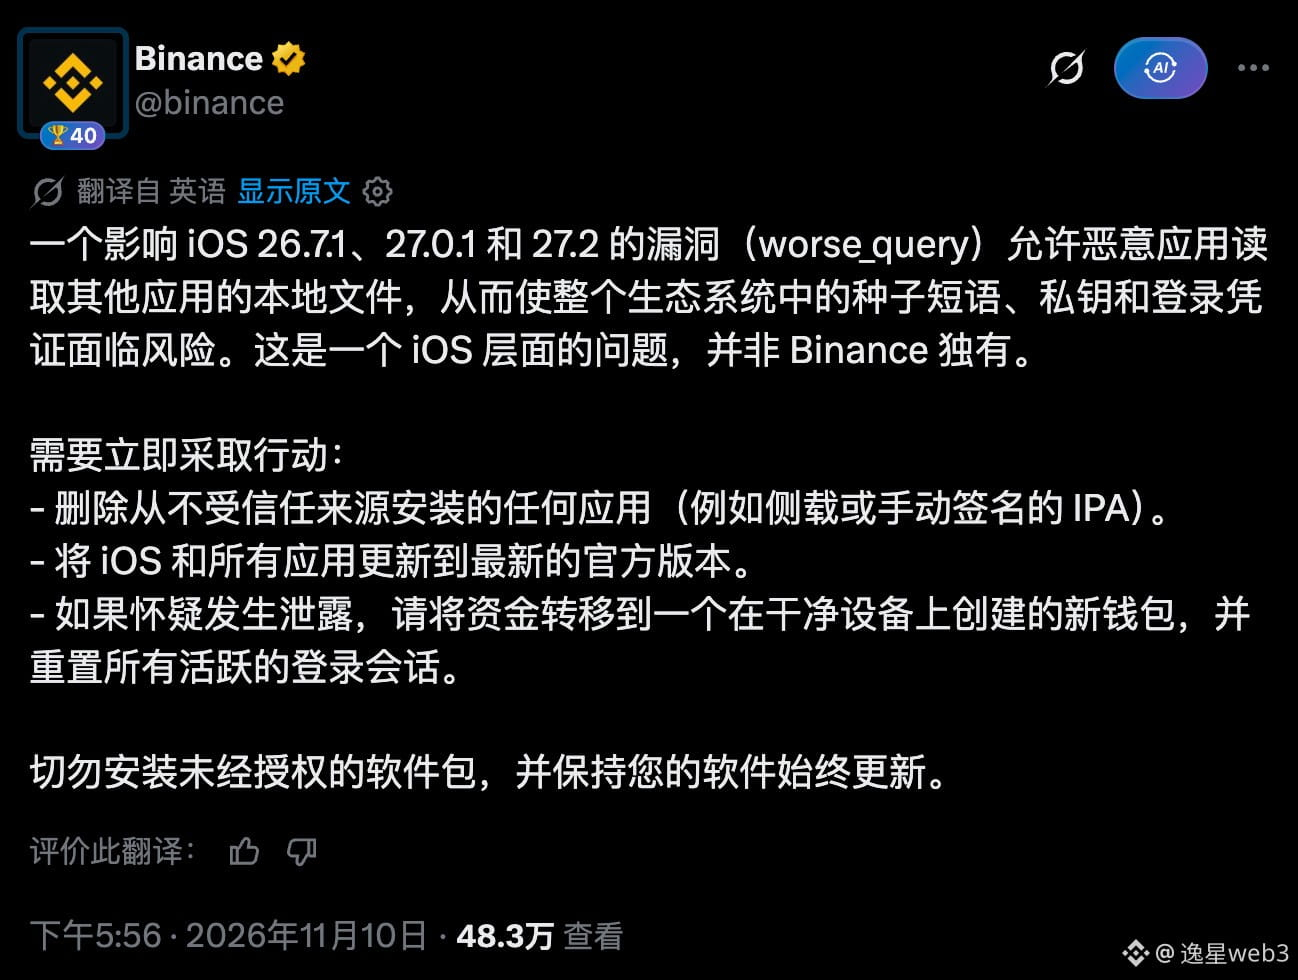
This worse_query vulnerability could allow malicious apps to read data from other apps, putting wallet private keys and login credentials at risk.
This vulnerability is medium-to-high severity (slightly less severe than the FomoPeek incident in September).
There is a risk only if you have downloaded apps from unknown sources (such as sideloaded apps or manually signed IPA files).
As of November 10, Apple has not issued any official statement about worse_query.
SlowMist says the security update in iOS 27.2.1 has fixed the vulnerability.
🟢 Recommendations:
1️⃣ Upgrade to IOS 27.2.1 as soon as possible
2️⃣ Do not download apps from unknown sources
3️⃣ Delete suspicious apps and move funds from wallets that may have been exposed
#安全漏洞
⚠️ Upgrade to IOS 27.2.1 as soon as possible
Normally, data is isolated between iOS apps.
This worse_query vulnerability could allow malicious apps to read data from other apps, putting wallet private keys and login credentials at risk.
This vulnerability is medium-to-high severity (slightly less severe than the FomoPeek incident in September).
There is a risk only if you have downloaded apps from unknown sources (such as sideloaded apps or manually signed IPA files).
As of November 10, Apple has not issued any official statement about worse_query.
SlowMist says the security update in iOS 27.2.1 has fixed the vulnerability.
🟢 Recommendations:
1️⃣ Upgrade to IOS 27.2.1 as soon as possible
2️⃣ Do not download apps from unknown sources
3️⃣ Delete suspicious apps and move funds from wallets that may have been exposed
#安全漏洞