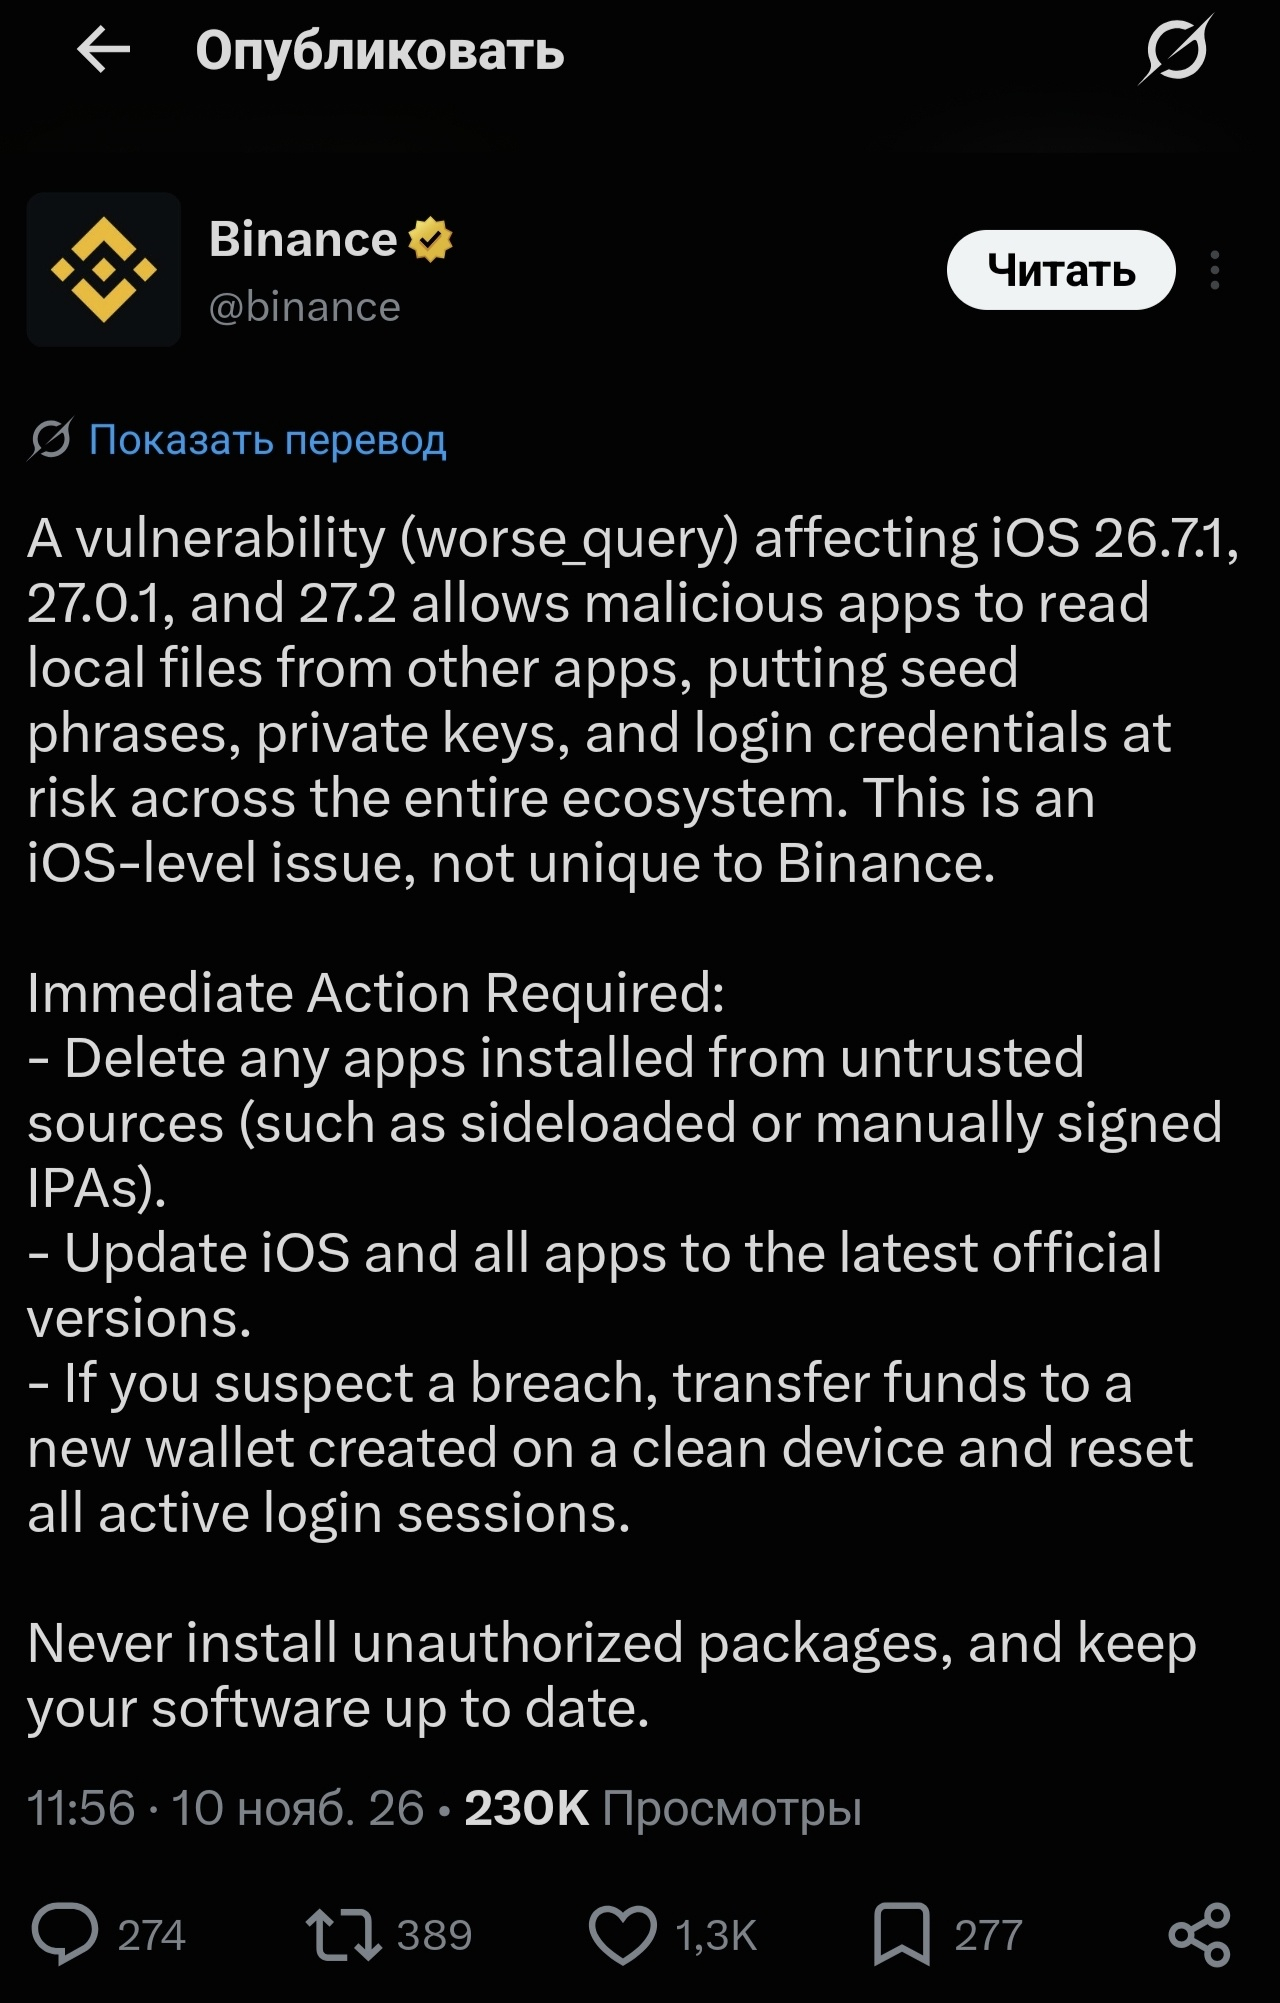
Cybersecurity specialists at SlowMist (in particular, security director 23pds) confirmed the technical details of this vulnerability:
What’s the issue?
This is a sandbox escape: In iOS, apps are isolated from each other and cannot access one another’s folders. The vulnerability, codenamed worse_query, breaks this isolation.
How the attack works: If malware gets onto a device, it can bypass the OS’s protections and directly read other apps’ local files (containers).
What’s at risk: If wallets or crypto apps store your seed phrases, private keys, logins, or WebView cache locally on the device in plain (unencrypted) text, a malicious app can copy them.
The key point: there is no automatic hack
The vulnerability itself does not steal money. For the trigger to be activated, the user must install a malicious app themselves. This most often happens through unofficial games, cracked software, or by installing third-party IPA files outside the App Store (sideloading).