Binance’s chief security officer confirms it: the withdrawal switch was effectively useless in this theft of $6.3 billion!
Last night, Binance co-CEO, He Yi, and Chief Security Officer Jimmy Su went live for a fireside chat and laid bare the blind spots in this attack.
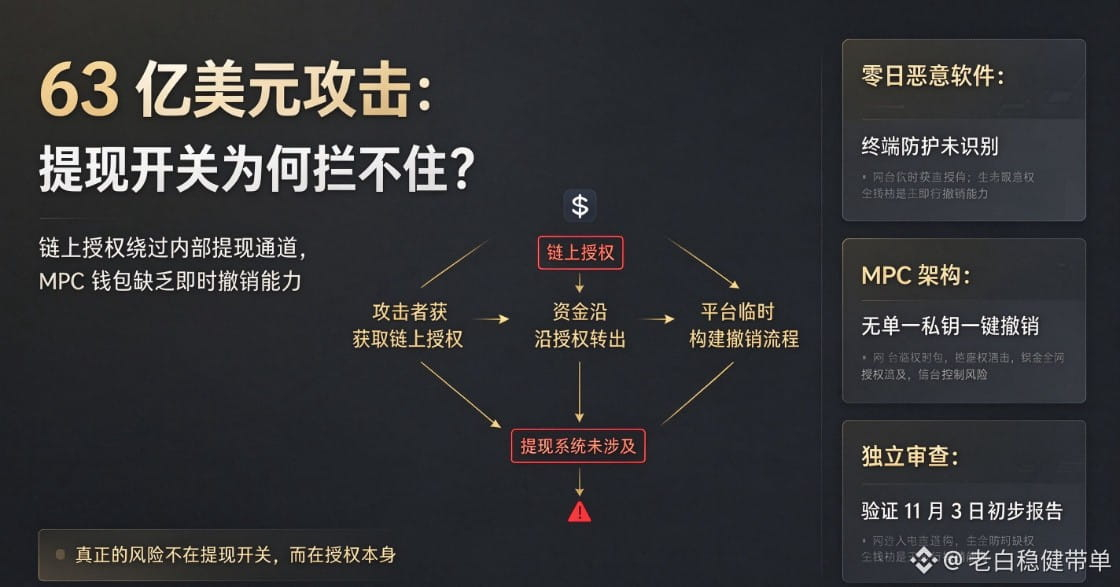
According to Jimmy Su, the on-chain transaction authorization obtained by the attacker did not use the withdrawal channel at all. Even if withdrawals had been disabled with a single click, the funds could still have been transferred out using the on-chain authorization.
This hot wallet uses an MPC (multi-party computation) architecture, so there is no single private key that can revoke authorization with one click. Moreover, this attack used zero-day malware, which conventional endpoint protection on the market was completely unable to detect at the time.
Going forward, Binance will invite external experts to conduct a comprehensive, independent review, and will also work with leading AI and security organizations to establish a dedicated security research fund focused on addressing emerging threats at the intersection of blockchain and AI. The key question now is whether the independent review will align with the preliminary report released on November 3.
#黄仁勋因婚外情致歉,英伟达启动独立调查 #币安神算子
Last night, Binance co-CEO, He Yi, and Chief Security Officer Jimmy Su went live for a fireside chat and laid bare the blind spots in this attack.
According to Jimmy Su, the on-chain transaction authorization obtained by the attacker did not use the withdrawal channel at all. Even if withdrawals had been disabled with a single click, the funds could still have been transferred out using the on-chain authorization.
This hot wallet uses an MPC (multi-party computation) architecture, so there is no single private key that can revoke authorization with one click. Moreover, this attack used zero-day malware, which conventional endpoint protection on the market was completely unable to detect at the time.
Going forward, Binance will invite external experts to conduct a comprehensive, independent review, and will also work with leading AI and security organizations to establish a dedicated security research fund focused on addressing emerging threats at the intersection of blockchain and AI. The key question now is whether the independent review will align with the preliminary report released on November 3.
#黄仁勋因婚外情致歉,英伟达启动独立调查 #币安神算子