
The Sequel to Binance’s $6.3 Billion Theft: When Hackers Turn “Interviews” into Weapons
This shocking $6.3 billion theft is exposing one of the most absurd episodes in Web3 security: the hackers didn’t crack private keys by force. Instead, they turned to “workplace infiltration.”
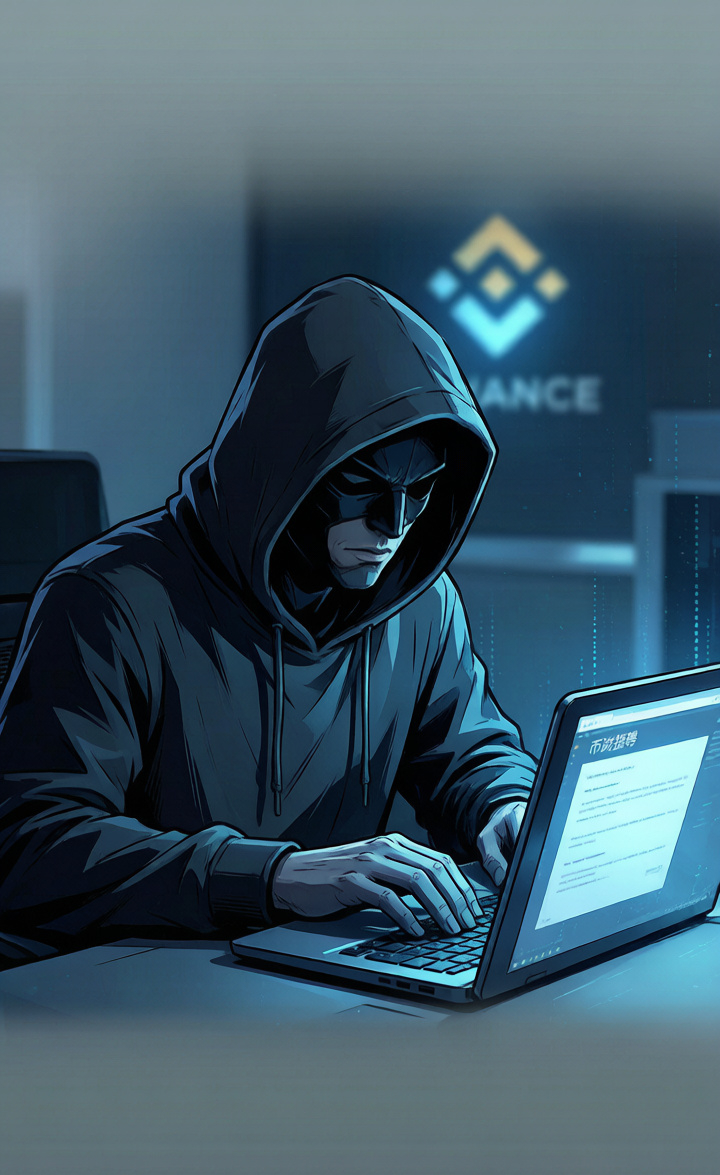
According to preliminary investigations, the attackers posed as recruiters conducting job interviews and sent malware-infected files to Binance operations staff. They successfully breached internal systems, hijacked an AI tool used for auxiliary signing, and ultimately gained control of assets across multiple chains.
Even more chilling are the on-chain traces: the stolen funds were “legitimately” authorized for transfer using the EIP-7702 standard. This means the hackers didn’t need to break in by force—they only had to obtain the “key” through social engineering to make smart contracts “willingly” open the door. This is not just a failure of technology, but a collapse of human judgment.
Yet crises are often catalysts for progress. Changpeng Zhao swiftly activated the SAFU fund to cover the losses in full, once again demonstrating the baseline responsibility of a mature platform. And rather than seeing Elon Musk’s knowing “frowning” expression on X as an omen of doom, we might view it as a sign of hope that the industry will undergo a painful but necessary purge.
Every security shock pushes the industry toward more robust AI defense systems and the adoption of zero-trust architectures. When hackers turn interviews into weapons, the crypto world will ultimately forge a smarter shield. Darkness may arrive, but the light of blockchain’s self-cleansing is never absent. #币安黑客攻击
This shocking $6.3 billion theft is exposing one of the most absurd episodes in Web3 security: the hackers didn’t crack private keys by force. Instead, they turned to “workplace infiltration.”
According to preliminary investigations, the attackers posed as recruiters conducting job interviews and sent malware-infected files to Binance operations staff. They successfully breached internal systems, hijacked an AI tool used for auxiliary signing, and ultimately gained control of assets across multiple chains.
Even more chilling are the on-chain traces: the stolen funds were “legitimately” authorized for transfer using the EIP-7702 standard. This means the hackers didn’t need to break in by force—they only had to obtain the “key” through social engineering to make smart contracts “willingly” open the door. This is not just a failure of technology, but a collapse of human judgment.
Yet crises are often catalysts for progress. Changpeng Zhao swiftly activated the SAFU fund to cover the losses in full, once again demonstrating the baseline responsibility of a mature platform. And rather than seeing Elon Musk’s knowing “frowning” expression on X as an omen of doom, we might view it as a sign of hope that the industry will undergo a painful but necessary purge.
Every security shock pushes the industry toward more robust AI defense systems and the adoption of zero-trust architectures. When hackers turn interviews into weapons, the crypto world will ultimately forge a smarter shield. Darkness may arrive, but the light of blockchain’s self-cleansing is never absent. #币安黑客攻击