After $660,000 was stolen, this 2020-era protocol broke up with its users!
Let me cut to the chase: I’ve read dozens of post-hack announcements—some shift the blame, some make empty promises, and some pretend nothing happened. ACryptoS is the first I’ve seen come clean like this.
This morning, veteran DeFi yield aggregator ACryptoS disclosed that its vaults had been attacked: across 5 chains and 77 vaults, roughly $665,000 was lost (SlowMist’s exact figure is $665,429).
The vulnerability itself was absurdly simple: the contract’s depositMulti function failed to validate inputs. An attacker only had to deposit a tiny amount of tokens to mint most of the shares in a vault, then withdraw other people’s money. The protocol launched in 2020, and its documentation still says, “No code vulnerability has ever been exploited since launch”—six years without a blemish, brought down by a validation check that was never finished.
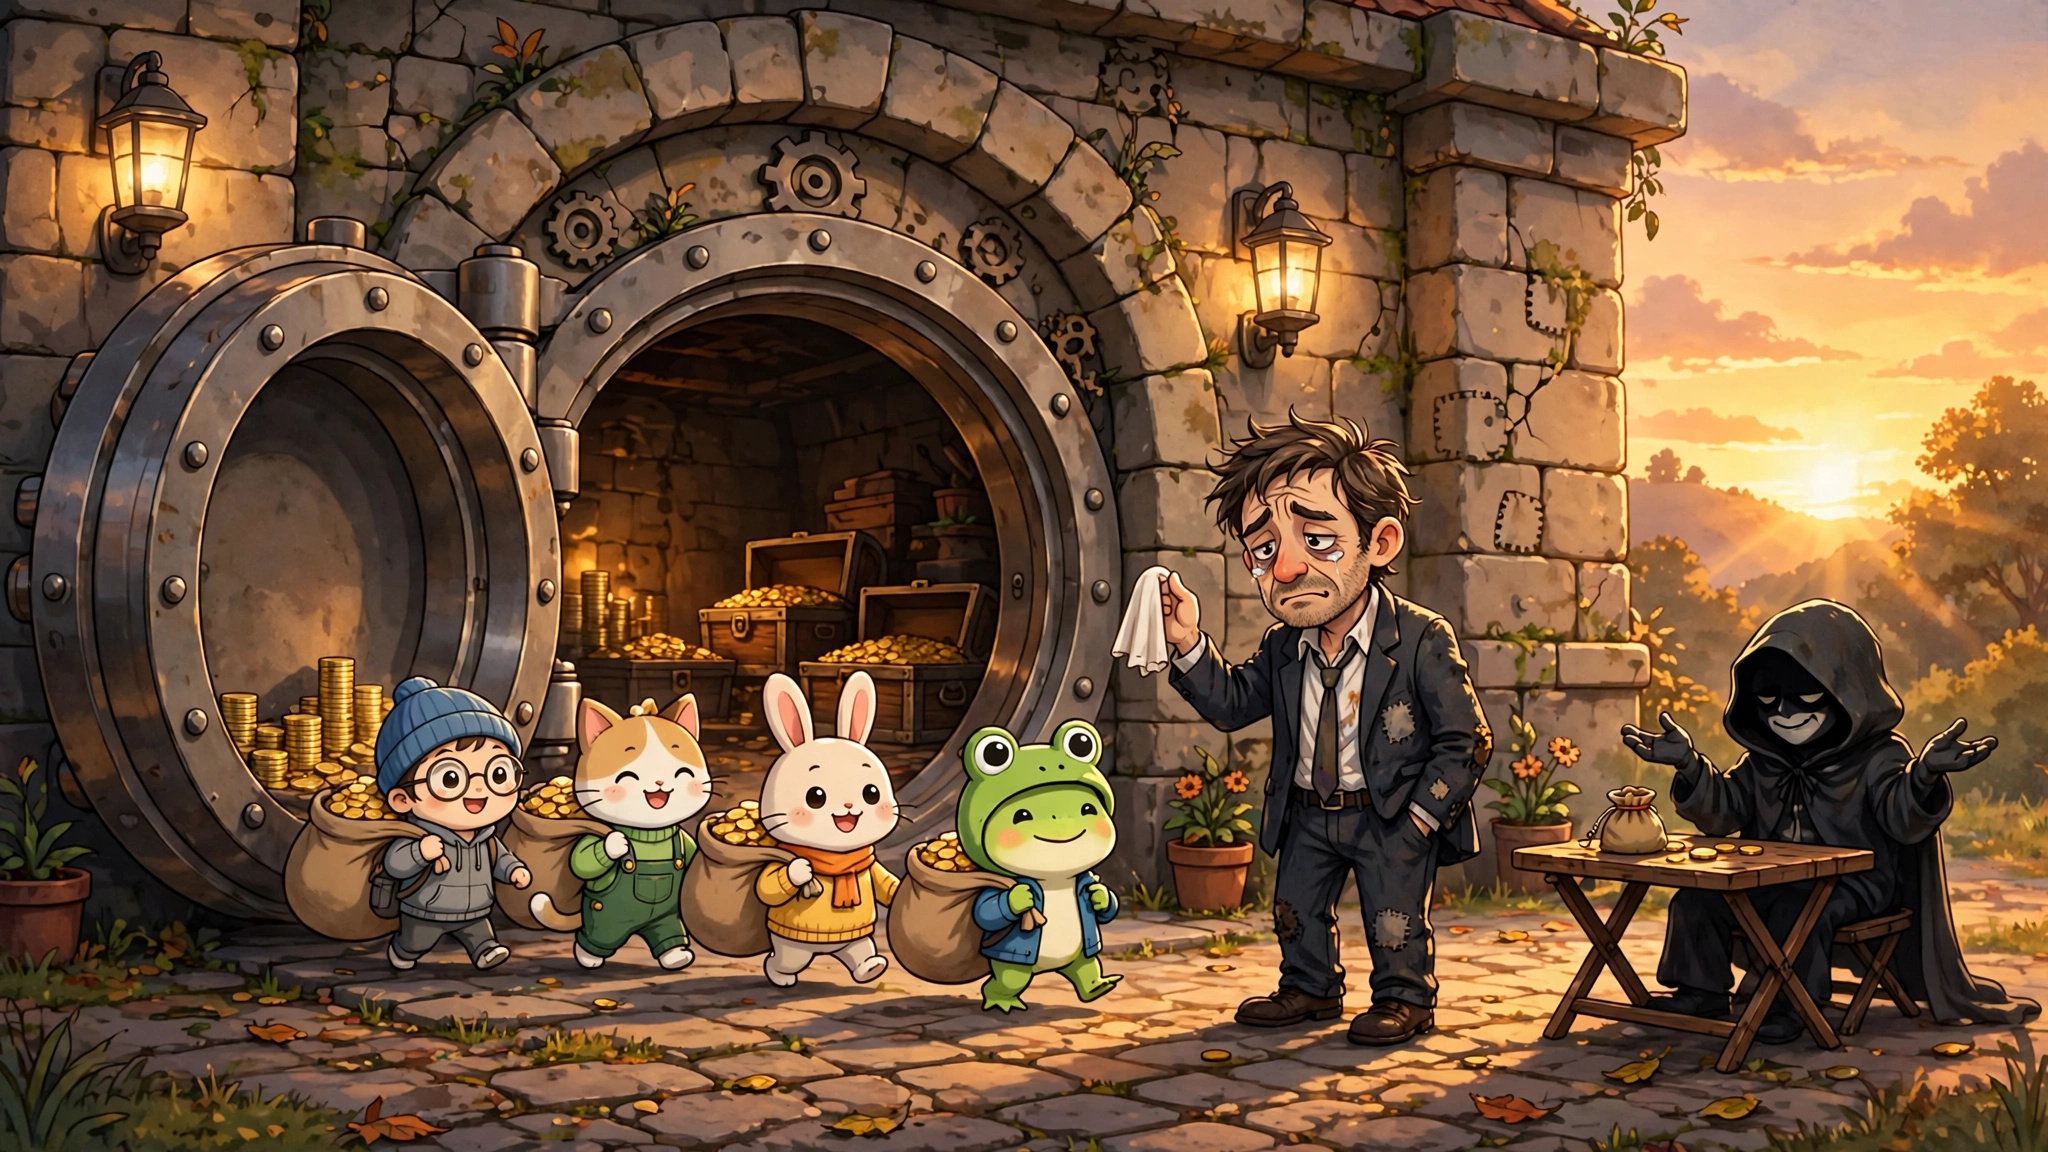
But what really made this story blow up was what the team did next: deposits were disabled, while withdrawals remained open; the stolen funds had already been moved, and the team sent the attacker a message—return the money and you can keep 10% as a bounty, about $66,500. Then the announcement stated outright: the team no longer had the resources to keep maintaining the project, operations were ceasing, and users should withdraw their assets as soon as possible.
This announcement was more honest than my breakup texts: “I can’t do this anymore. You should go. Take your stuff and don’t look back.” No “we’re doing everything we can to recover the funds,” no “please give us a little more time”—they couldn’t even be bothered to make promises.
Even more surreal is that 10%: in many hacks, projects drag their feet on enabling withdrawals and use new users’ money to plug old holes; here, the order was reversed—first open the gates so users can withdraw, then sit across the negotiating table from the hacker to discuss their “commission.” That’s how surreal the world of DeFi can be. Sometimes hackers have a stronger sense of honor than the projects.
$665,000 isn’t a huge sum, but what died was a six-year-old protocol. What sealed its fate wasn’t the hacker, but its own words: “We’re out of resources.” If you’ve got money sleeping in various yield vaults, check your positions tonight—some doors can close without warning.
$ETH $BNB
Let me cut to the chase: I’ve read dozens of post-hack announcements—some shift the blame, some make empty promises, and some pretend nothing happened. ACryptoS is the first I’ve seen come clean like this.
This morning, veteran DeFi yield aggregator ACryptoS disclosed that its vaults had been attacked: across 5 chains and 77 vaults, roughly $665,000 was lost (SlowMist’s exact figure is $665,429).
The vulnerability itself was absurdly simple: the contract’s depositMulti function failed to validate inputs. An attacker only had to deposit a tiny amount of tokens to mint most of the shares in a vault, then withdraw other people’s money. The protocol launched in 2020, and its documentation still says, “No code vulnerability has ever been exploited since launch”—six years without a blemish, brought down by a validation check that was never finished.
But what really made this story blow up was what the team did next: deposits were disabled, while withdrawals remained open; the stolen funds had already been moved, and the team sent the attacker a message—return the money and you can keep 10% as a bounty, about $66,500. Then the announcement stated outright: the team no longer had the resources to keep maintaining the project, operations were ceasing, and users should withdraw their assets as soon as possible.
This announcement was more honest than my breakup texts: “I can’t do this anymore. You should go. Take your stuff and don’t look back.” No “we’re doing everything we can to recover the funds,” no “please give us a little more time”—they couldn’t even be bothered to make promises.
Even more surreal is that 10%: in many hacks, projects drag their feet on enabling withdrawals and use new users’ money to plug old holes; here, the order was reversed—first open the gates so users can withdraw, then sit across the negotiating table from the hacker to discuss their “commission.” That’s how surreal the world of DeFi can be. Sometimes hackers have a stronger sense of honor than the projects.
$665,000 isn’t a huge sum, but what died was a six-year-old protocol. What sealed its fate wasn’t the hacker, but its own words: “We’re out of resources.” If you’ve got money sleeping in various yield vaults, check your positions tonight—some doors can close without warning.
$ETH $BNB