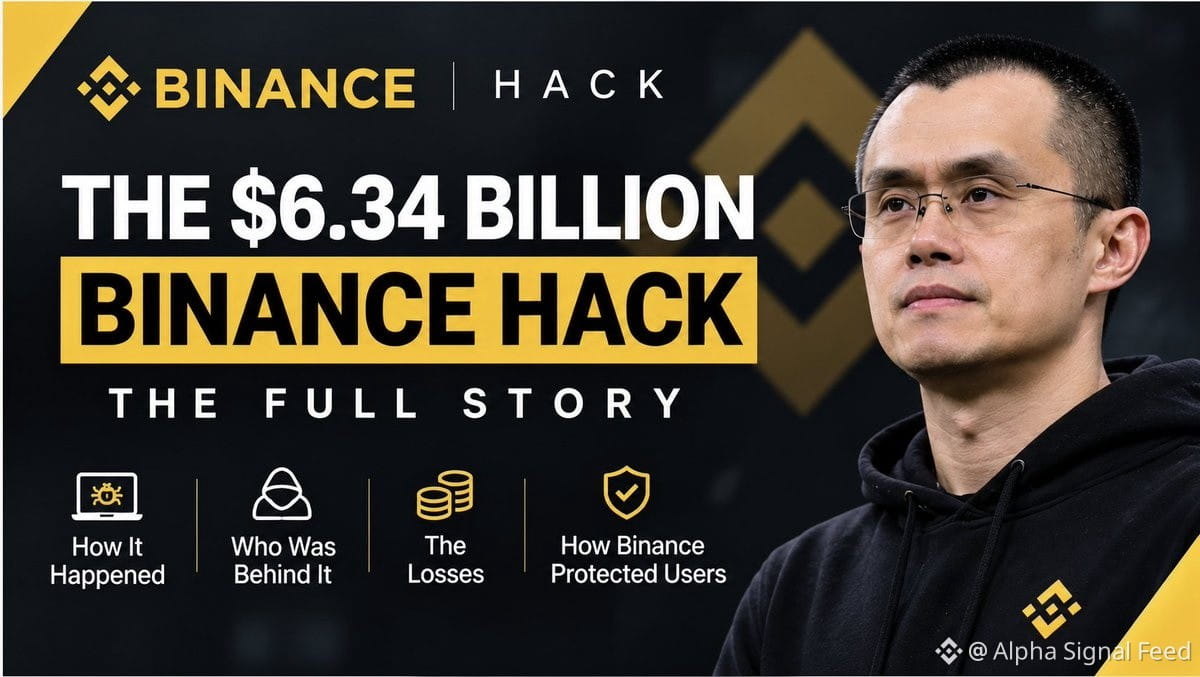
THE $6.34B BINANCE HACK: WHAT ACTUALLY WENT DOWN
One of the biggest security breaches in crypto history just unfolded. Fake job interviews, compromised employee devices, stolen credentials, and a multi-month infiltration by North Korea's TraderTraitor operation.
Here's the full breakdown:
THE ATTACK TIMELINE
October 29: Binance detected unauthorized transfers from hot wallets. $6.34B in digital assets moved across multiple chains.
But the attack started way earlier:
• June: Attackers compromised an employee's device via malicious dev software
• September: Second engineer targeted through fake job interview with malicious code
• October 20: Full access to employee systems, credentials, and wallet infrastructure
• October 29: Billions drained
WHAT GOT STOLEN
233.46M $XRP
970,500 $SOL
44.2M $OP
18,270 $BTC
Plus $ETH and other assets
Attackers immediately started converting everything into $ETH to complicate recovery.
THE FIGHTBACK
FBI officially blamed North Korea on October 31.
Industry response:
• Tether froze ~$1.57B $USDT
• Circle froze $800M+ $USDC
• Binance worked with blockchain investigators and law enforcement to trace funds
BINANCE'S RESPONSE
Say what you want about the security failure, but the response was solid:
• Covered all affected customer assets via SAFU + corporate treasury
• Replenished 98% of impacted tokens by October 31
• Customers bore ZERO losses
• Restored withdrawals gradually
• Expanded Proof of Reserves to 44 tokens
• Replaced compromised devices
• Launched independent cybersecurity review
THE REAL TAKEAWAY
The breach was serious. The internal failures need to be investigated hard.
But Binance took full financial responsibility and worked with the industry to recover funds. That matters.
An exchange isn't just about security when things are good. It's about how they respond when things go sideways.
Lesson for the industry: Protecting users must always come first. Every platform needs to learn from this.
One of the biggest security breaches in crypto history just unfolded. Fake job interviews, compromised employee devices, stolen credentials, and a multi-month infiltration by North Korea's TraderTraitor operation.
Here's the full breakdown:
THE ATTACK TIMELINE
October 29: Binance detected unauthorized transfers from hot wallets. $6.34B in digital assets moved across multiple chains.
But the attack started way earlier:
• June: Attackers compromised an employee's device via malicious dev software
• September: Second engineer targeted through fake job interview with malicious code
• October 20: Full access to employee systems, credentials, and wallet infrastructure
• October 29: Billions drained
WHAT GOT STOLEN
233.46M $XRP
970,500 $SOL
44.2M $OP
18,270 $BTC
Plus $ETH and other assets
Attackers immediately started converting everything into $ETH to complicate recovery.
THE FIGHTBACK
FBI officially blamed North Korea on October 31.
Industry response:
• Tether froze ~$1.57B $USDT
• Circle froze $800M+ $USDC
• Binance worked with blockchain investigators and law enforcement to trace funds
BINANCE'S RESPONSE
Say what you want about the security failure, but the response was solid:
• Covered all affected customer assets via SAFU + corporate treasury
• Replenished 98% of impacted tokens by October 31
• Customers bore ZERO losses
• Restored withdrawals gradually
• Expanded Proof of Reserves to 44 tokens
• Replaced compromised devices
• Launched independent cybersecurity review
THE REAL TAKEAWAY
The breach was serious. The internal failures need to be investigated hard.
But Binance took full financial responsibility and worked with the industry to recover funds. That matters.
An exchange isn't just about security when things are good. It's about how they respond when things go sideways.
Lesson for the industry: Protecting users must always come first. Every platform needs to learn from this.