#keplr建议社交登录用户转移资产 🚨 Keplr Wallet Exposes Private Key Leak Risk! Users Who Sign In With Google or Apple Should Be on Alert!
Another crypto wallet security incident has drawn market attention!
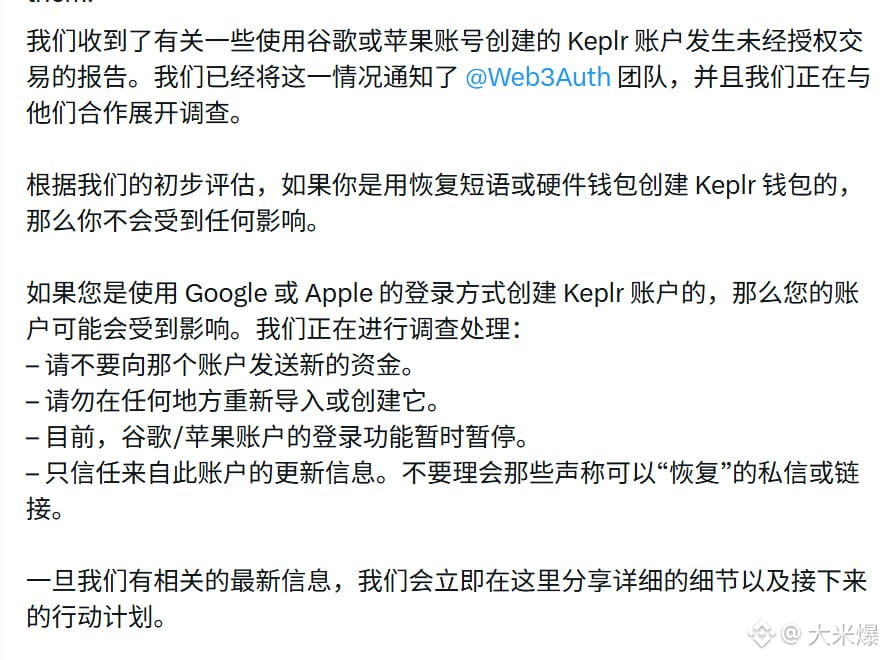
On November 8, Keplr urged users who created wallets using their Google or Apple accounts to immediately stop depositing new funds into the affected accounts and transfer any remaining movable assets to new accounts protected by a recovery phrase or hardware wallet.
The issue stems from a vulnerability in the infrastructure of third-party service Web3Auth, and some users' private keys may already have been exposed.
The real danger this time isn't a coin's price plunging—it's that a login method users thought was safe could become a way for their assets to be stolen.
First, convenient login doesn't mean your assets are safe.
Creating a wallet with one-click Google or Apple sign-in does lower the barrier to using Web3, but if the underlying private key management service has a vulnerability, users' assets are still at risk.
Second, wallet assets may already have been affected.
Web3Auth is currently conducting a white-hat asset recovery effort. Some users may find their balances reduced or even wiped out, but this doesn't necessarily mean all the losses were due to hacking. Official verification is still pending.
Third, the real risk may not be over yet.
For accounts whose private keys have already been exposed, signing in again won't eliminate the risk at its source.
My view is clear: Web3 can strive to be convenient, but never at the expense of private key security.
This incident is another reminder that decentralized wallets aren't completely free of third-party risks.
For affected users, the priority now isn't speculating about coin prices, but safeguarding their assets.
Don't click “asset recovery” links sent by strangers, and never disclose your recovery phrase or private key to anyone.
Related tokens: ATOM, INJ, OSMO
👇 Click the link below to go directly there!
Another crypto wallet security incident has drawn market attention!
On November 8, Keplr urged users who created wallets using their Google or Apple accounts to immediately stop depositing new funds into the affected accounts and transfer any remaining movable assets to new accounts protected by a recovery phrase or hardware wallet.
The issue stems from a vulnerability in the infrastructure of third-party service Web3Auth, and some users' private keys may already have been exposed.
The real danger this time isn't a coin's price plunging—it's that a login method users thought was safe could become a way for their assets to be stolen.
First, convenient login doesn't mean your assets are safe.
Creating a wallet with one-click Google or Apple sign-in does lower the barrier to using Web3, but if the underlying private key management service has a vulnerability, users' assets are still at risk.
Second, wallet assets may already have been affected.
Web3Auth is currently conducting a white-hat asset recovery effort. Some users may find their balances reduced or even wiped out, but this doesn't necessarily mean all the losses were due to hacking. Official verification is still pending.
Third, the real risk may not be over yet.
For accounts whose private keys have already been exposed, signing in again won't eliminate the risk at its source.
My view is clear: Web3 can strive to be convenient, but never at the expense of private key security.
This incident is another reminder that decentralized wallets aren't completely free of third-party risks.
For affected users, the priority now isn't speculating about coin prices, but safeguarding their assets.
Don't click “asset recovery” links sent by strangers, and never disclose your recovery phrase or private key to anyone.
Related tokens: ATOM, INJ, OSMO
👇 Click the link below to go directly there!