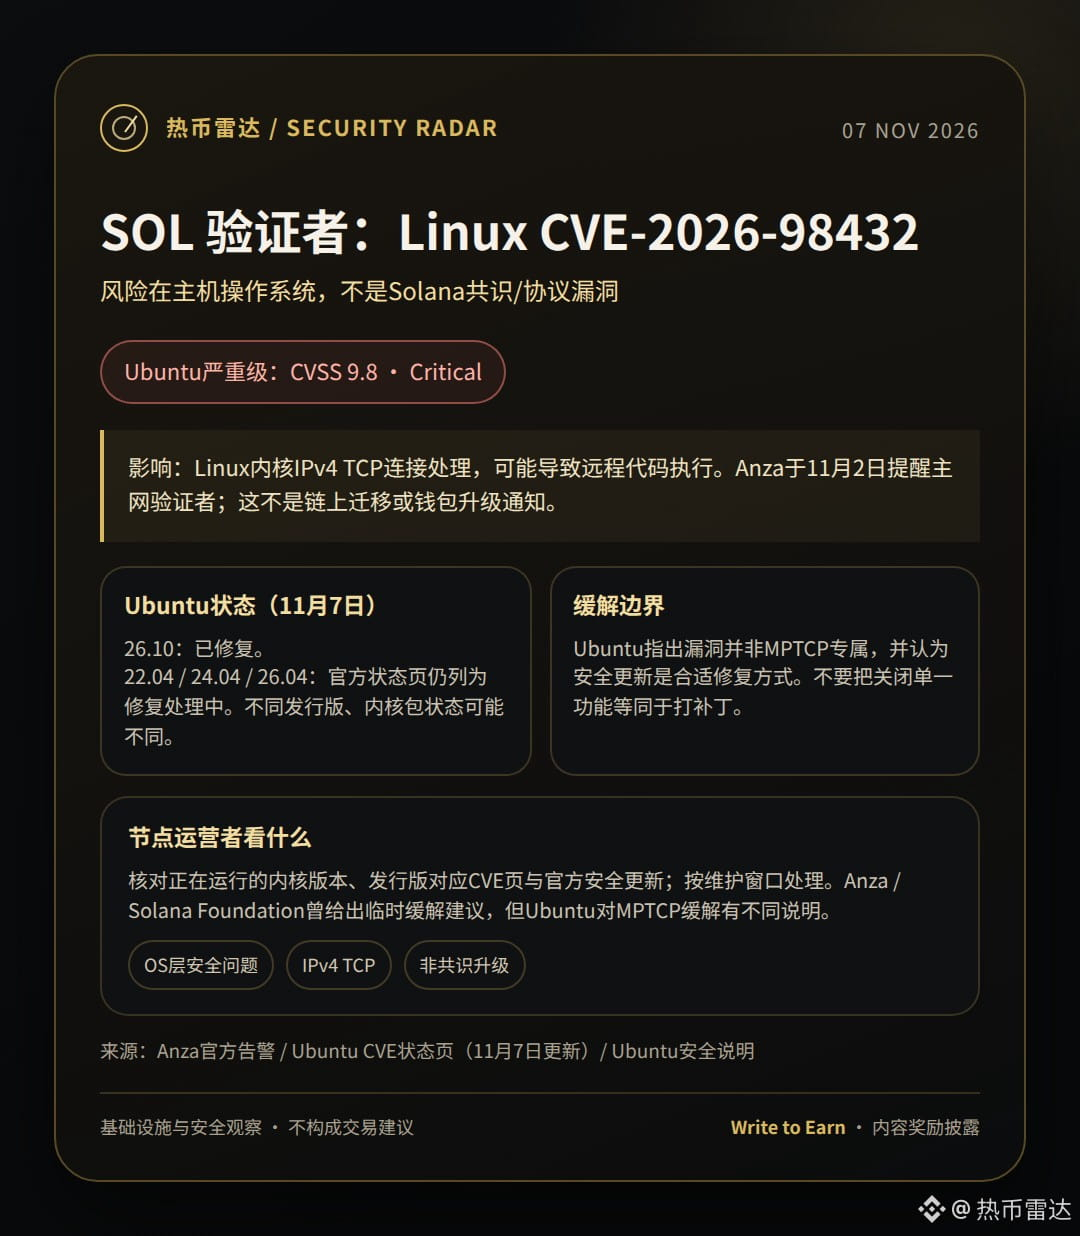
SOL validators, take note: the risk lies in the Linux host kernel, not a Solana consensus failure. Ubuntu rated CVE-2026-98432 9.8/10 in severity. It affects IPv4 TCP and could allow remote code execution.
Anza alerted mainnet validators on November 2; Ubuntu’s status page showed on November 7 that the issue was fixed in 26.10, while 22.04, 24.04, and 26.04 were still being addressed. Ubuntu emphasized that the vulnerability is not specific to MPTCP, and disabling MPTCP is not a substitute for a patch. Node operators should check their kernels and distribution advisories. Would you track distribution patches first, or validator mitigations?
Sources: Anza alert https://x.com/anza_xyz/status/2117045789730201889 |Ubuntu CVE status https://ubuntu.com/security/CVE-2026-98432 |Ubuntu explanation https://ubuntu.com/blog/fixes-available-in-proposed-pocket-for-cve-2026-98432
Disclosure: Participating in Binance Square Write to Earn; content rewards may be received. Eligibility and amounts are subject to platform rules and are not guaranteed. Not investment advice.
$SOL #Solana
Anza alerted mainnet validators on November 2; Ubuntu’s status page showed on November 7 that the issue was fixed in 26.10, while 22.04, 24.04, and 26.04 were still being addressed. Ubuntu emphasized that the vulnerability is not specific to MPTCP, and disabling MPTCP is not a substitute for a patch. Node operators should check their kernels and distribution advisories. Would you track distribution patches first, or validator mitigations?
Sources: Anza alert https://x.com/anza_xyz/status/2117045789730201889 |Ubuntu CVE status https://ubuntu.com/security/CVE-2026-98432 |Ubuntu explanation https://ubuntu.com/blog/fixes-available-in-proposed-pocket-for-cve-2026-98432
Disclosure: Participating in Binance Square Write to Earn; content rewards may be received. Eligibility and amounts are subject to platform rules and are not guaranteed. Not investment advice.
$SOL #Solana