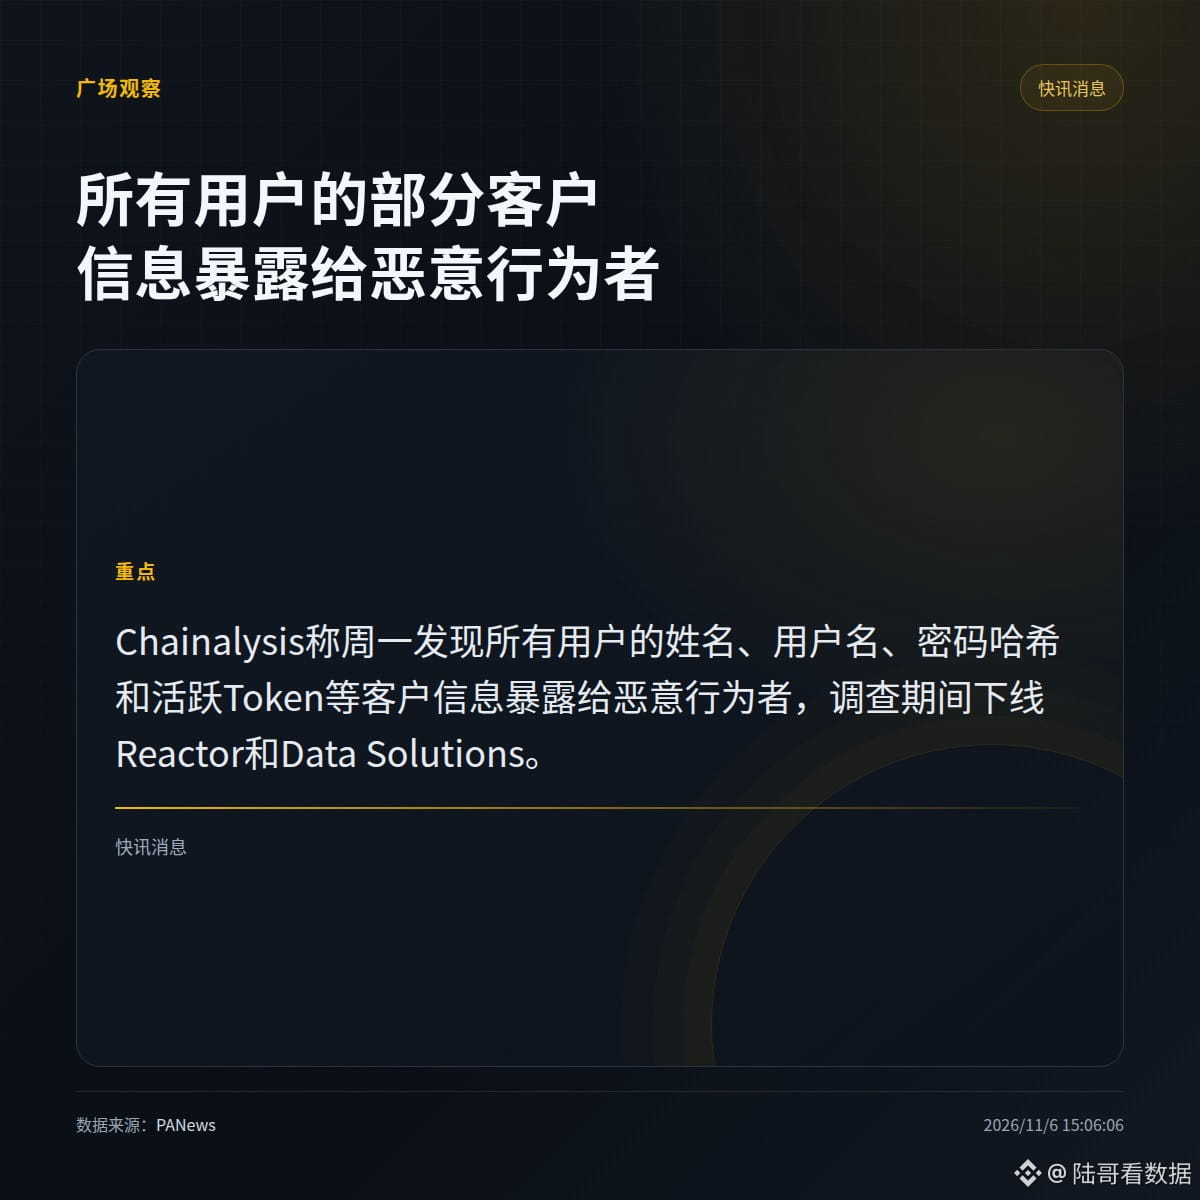
Chainalysis said it discovered on Monday that some customer information for all users had been exposed to malicious actors, including names, usernames, password hashes, and active Tokens.
During the investigation, Chainalysis removed access to Reactor and Data Solutions. The company said there is currently no evidence that investigation data was accessed or attribution data was manipulated. After detecting unusual activity today, KYT (user interface and API), other address-screening products, and the login page were taken offline. Customers whose KYT accounts may have been accessed without authorization were notified directly.
· The affected scope is “all users,” and the exposed fields include password hashes and active Tokens.
· “Investigation data was not accessed” is the company’s current claim; it has not been verified by a third party.
If you can’t log in to your compliance tool, would you contact your account manager first or troubleshoot your local network first?
During the investigation, Chainalysis removed access to Reactor and Data Solutions. The company said there is currently no evidence that investigation data was accessed or attribution data was manipulated. After detecting unusual activity today, KYT (user interface and API), other address-screening products, and the login page were taken offline. Customers whose KYT accounts may have been accessed without authorization were notified directly.
· The affected scope is “all users,” and the exposed fields include password hashes and active Tokens.
· “Investigation data was not accessed” is the company’s current claim; it has not been verified by a third party.
If you can’t log in to your compliance tool, would you contact your account manager first or troubleshoot your local network first?