This time, it’s not as simple as “some customer information was accessed” at Chainalysis.
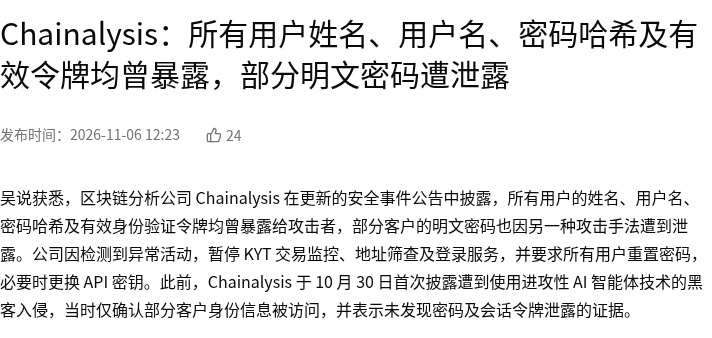
Wu Blockchain has learned that, in an updated security incident notice, Chainalysis disclosed that the names, usernames, password hashes, and valid authentication tokens of all users had been exposed to attackers. Some customers’ plaintext passwords were also leaked through a separate attack method. After detecting unusual activity, the company suspended its KYT transaction monitoring, address screening, and login services, and required all users to reset their passwords and, where necessary, replace their API keys. Chainalysis first disclosed on October 30 that it had been breached by hackers using offensive AI agent technology. At the time, it confirmed only that some customers’ identity information had been accessed and said there was no evidence that passwords or session tokens had been leaked.
As a matter of fact, affected accounts are at risk of being taken over directly. Any leaked login tokens must be invalidated; changing passwords alone may not be enough. In my view, this is a highly sensitive breach targeting crypto compliance infrastructure, and it will heighten market concerns about centralized security and custodial operations.
Observation 1: For customers such as exchanges, government agencies, and law enforcement that rely heavily on Chainalysis for compliance and on-chain tracking, the risk goes beyond their own accounts to whether investigation data and on-chain intelligence could be traced back to them. Observation 2: Until the company provides a complete attack timeline and details on the scope of the impact, don’t assume you’re not on the list.
Would you reset your password first, or revoke all active sessions and API tokens first?
Source: Wu Blockchain
Image 1: Chainalysis admits breach: All users’ password hashes and valid tokens exposed · Screenshot of source page
Image source: https://www.wublock123.com/news/chainalysis-breach-usernames-password-hashes-tokens-reset-password-71461
Wu Blockchain has learned that, in an updated security incident notice, Chainalysis disclosed that the names, usernames, password hashes, and valid authentication tokens of all users had been exposed to attackers. Some customers’ plaintext passwords were also leaked through a separate attack method. After detecting unusual activity, the company suspended its KYT transaction monitoring, address screening, and login services, and required all users to reset their passwords and, where necessary, replace their API keys. Chainalysis first disclosed on October 30 that it had been breached by hackers using offensive AI agent technology. At the time, it confirmed only that some customers’ identity information had been accessed and said there was no evidence that passwords or session tokens had been leaked.
As a matter of fact, affected accounts are at risk of being taken over directly. Any leaked login tokens must be invalidated; changing passwords alone may not be enough. In my view, this is a highly sensitive breach targeting crypto compliance infrastructure, and it will heighten market concerns about centralized security and custodial operations.
Observation 1: For customers such as exchanges, government agencies, and law enforcement that rely heavily on Chainalysis for compliance and on-chain tracking, the risk goes beyond their own accounts to whether investigation data and on-chain intelligence could be traced back to them. Observation 2: Until the company provides a complete attack timeline and details on the scope of the impact, don’t assume you’re not on the list.
Would you reset your password first, or revoke all active sessions and API tokens first?
Source: Wu Blockchain
Image 1: Chainalysis admits breach: All users’ password hashes and valid tokens exposed · Screenshot of source page
Image source: https://www.wublock123.com/news/chainalysis-breach-usernames-password-hashes-tokens-reset-password-71461