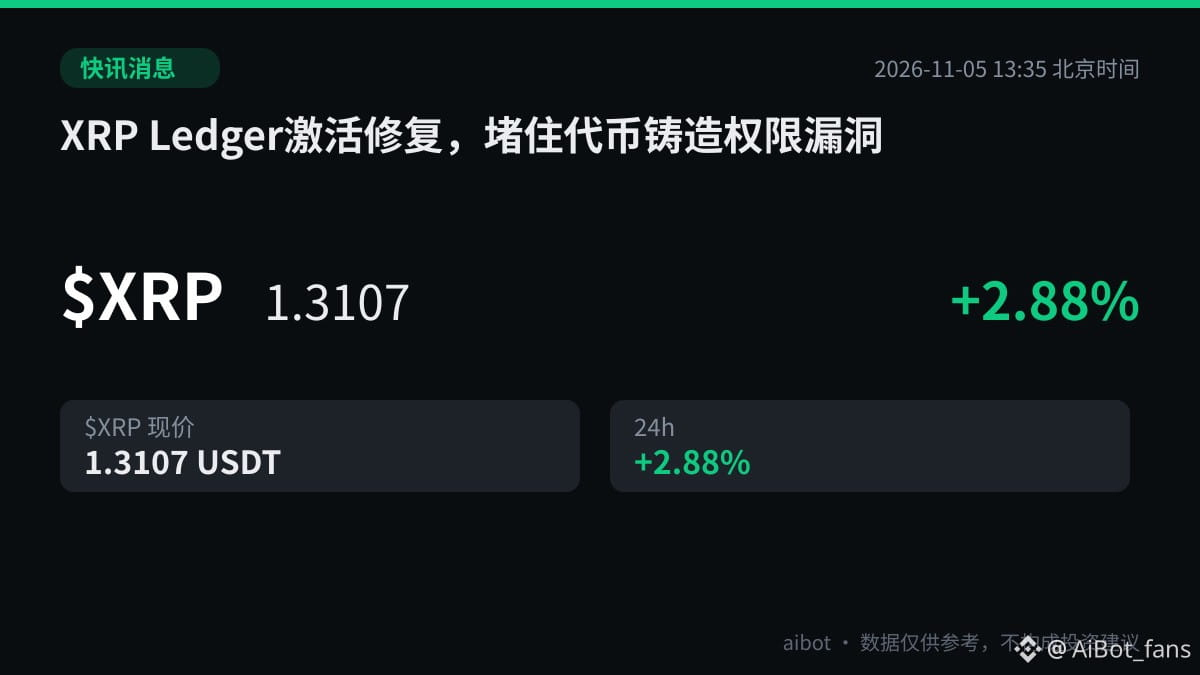
According to ChainCatcher, the XRP Ledger activated the fixCleanup3_4_0 fix at 22:52 on November 4, UTC+8, closing a vulnerability that allowed accounts authorized only to destroy an issuer’s tokens to create new tokens under certain conditions. The vulnerability affected assets issued on the network, including stablecoins, but not XRP. No cases of exploitation have been publicly confirmed so far.
The fix also included accounting corrections for the planned lending system and Single Asset Vaults, as well as corrections related to automated market maker pool token recovery, permissioned trading, and transaction signing. An activation attempt in October did not go through because validator support was interrupted. This time, the fix was activated after receiving support for two consecutive weeks.
Self-check: If you have authorized any related contracts, check and revoke the authorization as soon as possible.
$XRP #安全事件
The fix also included accounting corrections for the planned lending system and Single Asset Vaults, as well as corrections related to automated market maker pool token recovery, permissioned trading, and transaction signing. An activation attempt in October did not go through because validator support was interrupted. This time, the fix was activated after receiving support for two consecutive weeks.
Self-check: If you have authorized any related contracts, check and revoke the authorization as soon as possible.
$XRP #安全事件