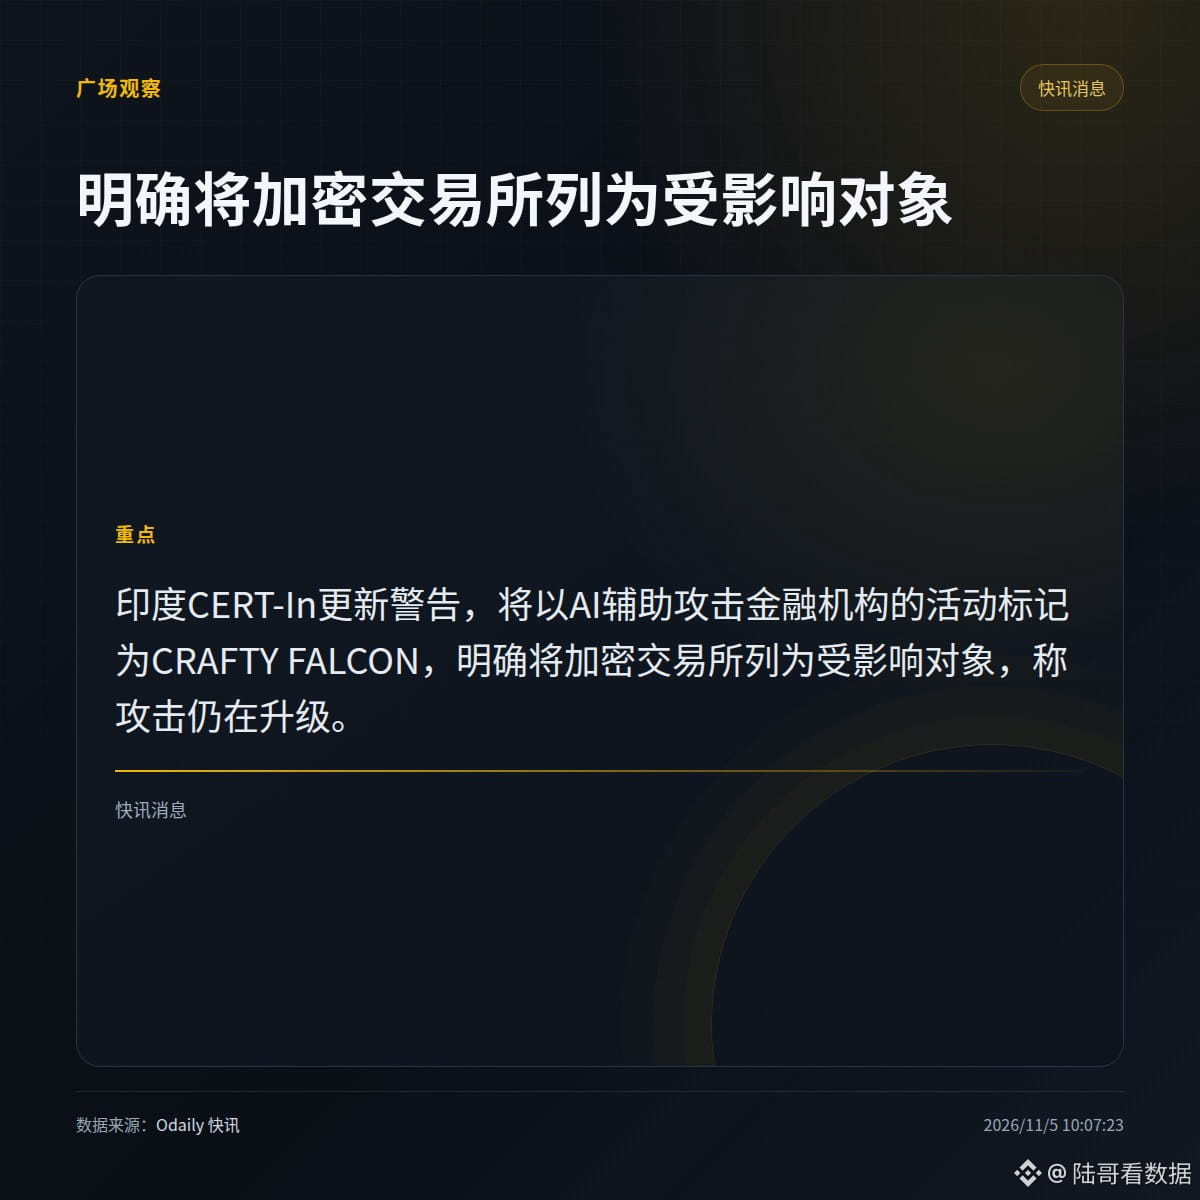
India’s Computer Emergency Response Team (CERT-In) on Wednesday dubbed AI-assisted attackers targeting financial institutions “CRAFTY FALCON” and explicitly listed cryptocurrency exchanges as affected entities in an updated advisory that was first issued last October.
The advisory said the attackers exploited vulnerable applications and exposed test environments, using shared credentials and access tokens to gain entry to production systems before deploying malicious files against cloud infrastructure. AI tools were used to quickly generate and refine attack scripts, and some attacks were scheduled for weekends and holidays to delay detection.
The agency also said the attackers had verified unauthorized transfers through small test transactions, stolen wallet keys, and moved funds out of wallets. CERT-In did not disclose the names of affected exchanges or the amount of losses.
· The recommended measures are clear: round-the-clock monitoring, increased staffing on weekends and holidays, and lower alert thresholds.
· The attack methods and impacts described above come from CERT-In’s advisory; no specific victims were named.
Does your team lower its alert thresholds on weekends?
The advisory said the attackers exploited vulnerable applications and exposed test environments, using shared credentials and access tokens to gain entry to production systems before deploying malicious files against cloud infrastructure. AI tools were used to quickly generate and refine attack scripts, and some attacks were scheduled for weekends and holidays to delay detection.
The agency also said the attackers had verified unauthorized transfers through small test transactions, stolen wallet keys, and moved funds out of wallets. CERT-In did not disclose the names of affected exchanges or the amount of losses.
· The recommended measures are clear: round-the-clock monitoring, increased staffing on weekends and holidays, and lower alert thresholds.
· The attack methods and impacts described above come from CERT-In’s advisory; no specific victims were named.
Does your team lower its alert thresholds on weekends?