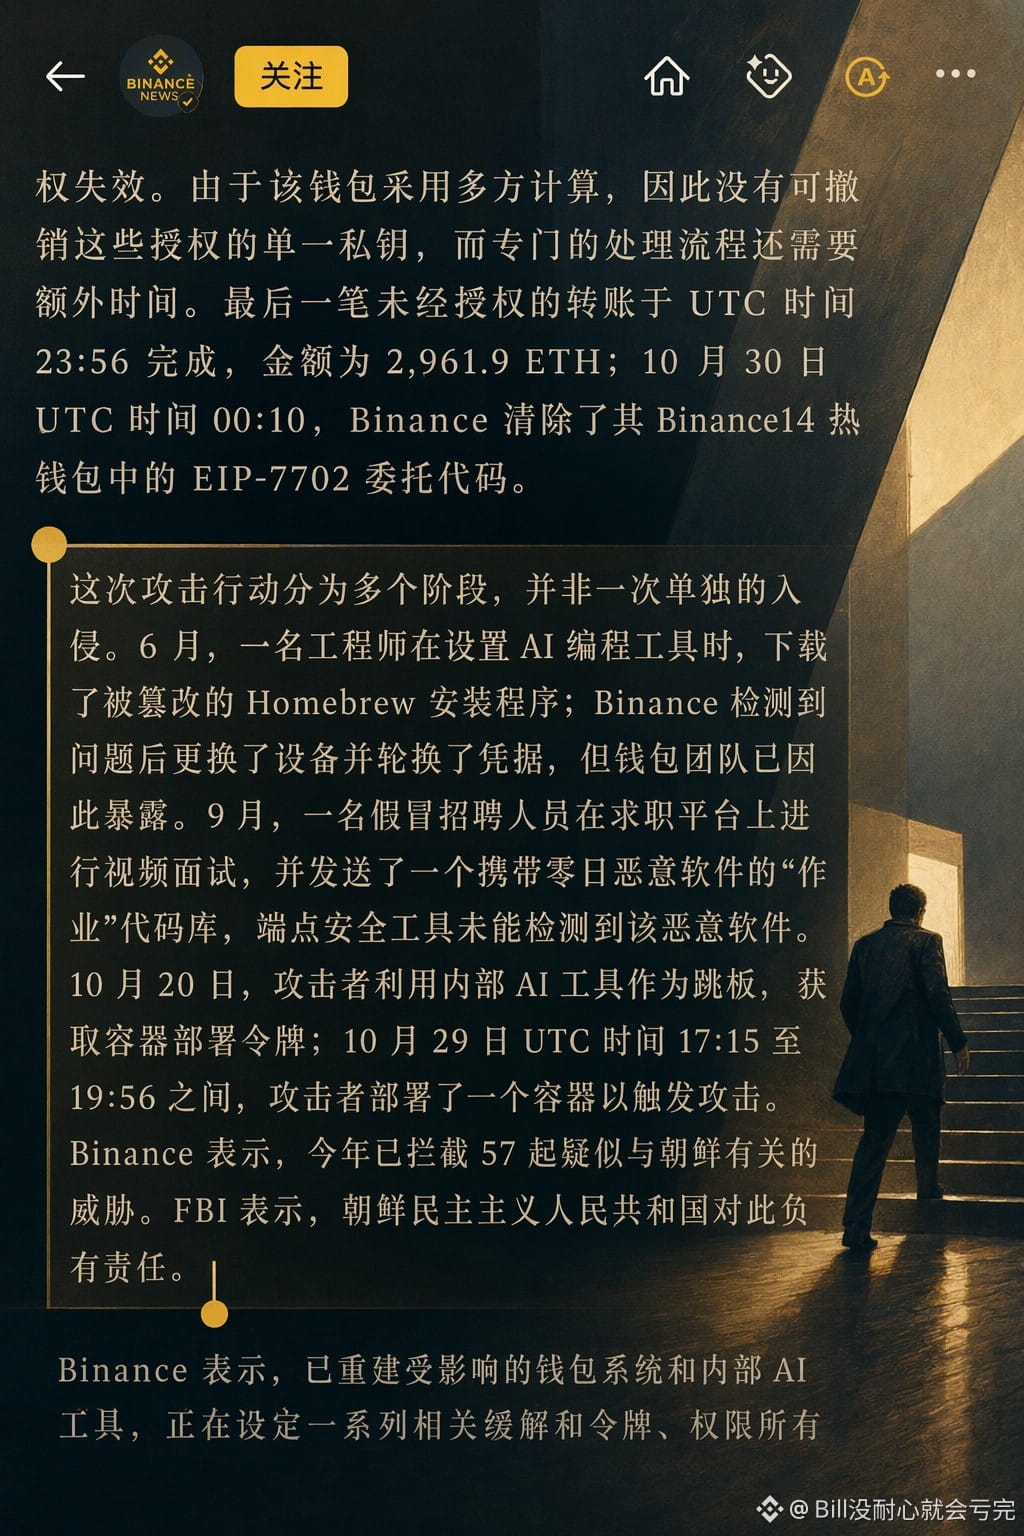
The trigger for this attack on Binance turned out to be an employee using a company computer to install a software package sent by a prospective employer during an interview for a new job. Whether the recruiter was legitimate or not, installing unfamiliar software on a company computer was dangerous enough.
The employee didn’t notice the Trojan after it was installed, and the hackers waited a month after gaining access before making their move. They really knew how to play the long game 😅
In the wake of this, access privileges for exchange employees and computer monitoring will likely be tightened. Computers will also need to identify, report, and block suspicious programs more quickly. The Binance Wallet team had expanded too quickly and too smoothly before this incident; perhaps now it’s time to slow down and review the relevant processes.
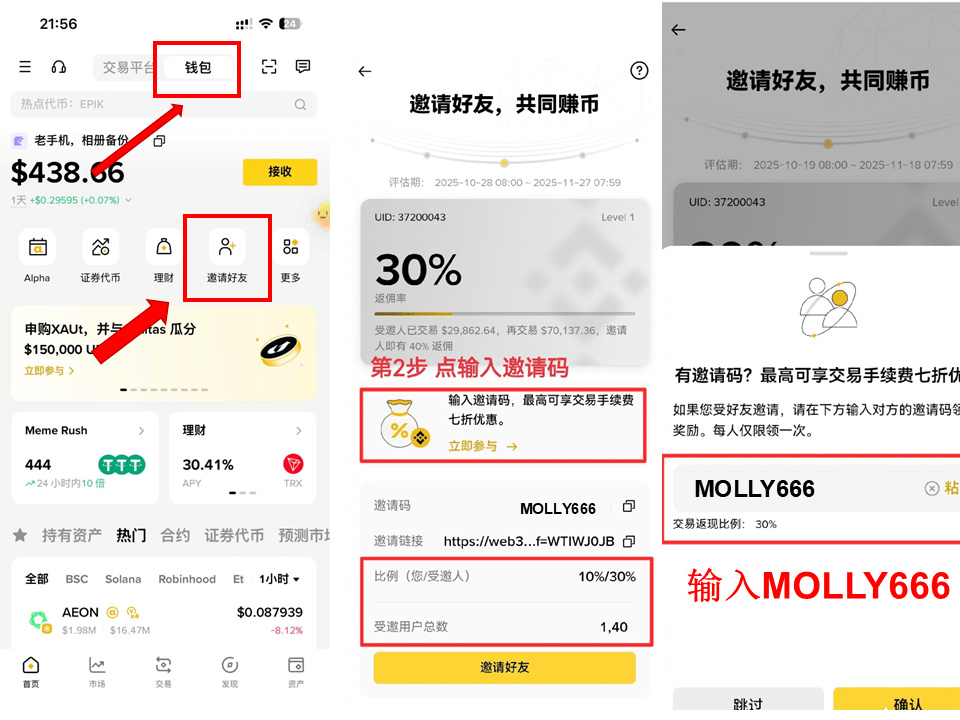
Binance Wallet invitation code: MOLLY666
The employee didn’t notice the Trojan after it was installed, and the hackers waited a month after gaining access before making their move. They really knew how to play the long game 😅
In the wake of this, access privileges for exchange employees and computer monitoring will likely be tightened. Computers will also need to identify, report, and block suspicious programs more quickly. The Binance Wallet team had expanded too quickly and too smoothly before this incident; perhaps now it’s time to slow down and review the relevant processes.
Binance Wallet invitation code: MOLLY666