
AZ__
8.4k Posts

AZ__
 Square Verified+
Report
Block User
Data Over Narratives | On-Chain Intelligence | Mechanism & Market Structure Research |
X: @AZ_Asif01
High-Frequency Trader
1.8 Years
315 Following
43.7K+ Followers
21.0K+ Liked
Posts
All
Quotes
Videos
Live
·
--
Bearish
Is Wall Street's fear finally fading, or is another volatility spike coming?
$ZEC
{future}(ZECUSDT)
$SUI
{future}(SUIUSDT)
$ONDO
{future}(ONDOUSDT)
Is Wall Street's fear finally fading, or is another volatility spike coming?
$ZEC
$SUI
$ONDO
$ZEC
$SUI
$ONDO
📈 Fear is fading fast
⚠️ Temporary relief only
🌪️ More volatility ahead
🚀 Confidence is returning
11 hr(s) left
4
2.4k
·
--
Bullish
Verified
Trump Accepts Midterm Results: What's Next for US Politics? 🇺🇸
Trump signals willingness to work with Democrats as election results point to a shift in congressional power.
How could this political shift impact the US markets?
$ARX
{future}(ARXUSDT)
$CAP
{future}(CAPUSDT)
$JCT
{future}(JCTUSDT)
Trump Accepts Midterm Results: What's Next for US Politics? 🇺🇸
Trump signals willingness to work with Democrats as election results point to a shift in congressional power.
How could this political shift impact the US markets?
$ARX
$CAP
$JCT
Trump signals willingness to work with Democrats as election results point to a shift in congressional power.
How could this political shift impact the US markets?
$ARX
$CAP
$JCT
📈 Market Recovery
72%
📉 More Market Volatility
8%
₿ Bullish for Crypto
12%
⚖️ Limited Market Impact
8%
25 votes • Voting closed
1
3
2.2k
·
--
Asian Markets Under Pressure! 📉
Tech stocks slide as US midterm uncertainty shakes investor confidence. Bitcoin also dips toward $76K.
What's the biggest risk for markets right now?
$LSK
{future}(LSKUSDT)
$EVAA
{future}(EVAAUSDT)
$BMT
{future}(BMTUSDT)
Asian Markets Under Pressure! 📉
Tech stocks slide as US midterm uncertainty shakes investor confidence. Bitcoin also dips toward $76K.
What's the biggest risk for markets right now?
$LSK
$EVAA
$BMT
Tech stocks slide as US midterm uncertainty shakes investor confidence. Bitcoin also dips toward $76K.
What's the biggest risk for markets right now?
$LSK
$EVAA
$BMT
📉 Tech Stock Sell-Off
50%
🇺🇸 US Political Uncertainty
25%
₿ Bitcoin's Weakness
6%
🌏 Global Market Volatility
19%
16 votes • Voting closed
3.8k
·
--
Article
The Binance Hack: Did One Rushed Click Leave a Trail to the Hacker?Introduction: A Massive Crypto Heist and an Unexpected Clue
On October 29, 2026, approximately $6.36 billion was stolen from Binance wallets across 10 blockchains, with most of the funds transferred in around 20 minutes. TRM Labs reported these figures through its blockchain investigation.
However, another detail attracted attention: a possible MetaMask transaction mistake that could have left an investigative trail. Viral discussions suggested that one checkbox exposed the hacker, but this theory remains unconfirmed.
Sources: TRM Labs; Reuters; independent developer analysis.
1. The Viral Claim: Was the Hacker Exposed by One Checkbox?
The claim suggests that the attacker made a simple mistake while processing a transaction through MetaMask. However, no individual has been identified through this alleged mistake.
The checkbox theory originated from an independent developer's analysis, not an official investigation announcement. An independent forensic review by GCSA also cautioned that the theory remains speculative.
Sources: Independent developer analysis; GCSA forensic investigation.
2. The Unusual Transaction: Paying Gas Fees in USDT Instead of ETH
An independent developer examining the attacker's transactions noticed that the wallet used MetaMask's Gas Station to pay fees in USDT despite holding ETH.
This unusual transaction attracted attention because it involved MetaMask's infrastructure. However, having ETH available does not prove that selecting USDT was accidental.
Sources: Independent developer analysis; GCSA forensic investigation; MetaMask documentation.
3. MetaMask's Gas Station: How One Transaction Could Leave a Digital Trail
MetaMask's Gas Station processes transactions through its service infrastructure. This raised the possibility that server-side records could contain useful technical information, potentially including an IP address.
The developer reportedly asked MetaMask to preserve relevant logs. However, there is no confirmation that an IP address was obtained or that the service identified the attacker.
Sources: Independent developer analysis; GCSA forensic investigation.
4. The Scale of the Incident: Understanding the Numbers
According to the initial reports and subsequent updates:
$6.36 billion: Estimated stolen amount, according to TRM Labs.20 minutes: Approximate time for most of the transfers.10 blockchains: Networks affected, according to TRM Labs.Approximately $2.7–$2.85 billion: Funds frozen or seized, according to TRM Labs and Elliptic.Bitcoin price decline: Approximately 5%, as reported in the original source material.$6 billion: Binance's reported financial reserve to cover losses.
The freezing of stolen stablecoins by Tether and Circle demonstrated how centralized issuers can intervene during major security incidents.
Sources: TRM Labs; Elliptic; Binance statements; Al Jazeera (as listed in the original PDF).
5. Who Is Behind the Attack?
TRM Labs and Chainalysis initially linked the attack to TraderTraitor, associated with North Korea's Lazarus Group.
On November 1, 2026, the FBI officially attributed the theft to North Korea's TraderTraitor group, strengthening the attribution beyond the earlier blockchain analytics assessments.
However, identifying a responsible hacking group does not necessarily reveal the individual operators behind the attack.
Sources: TRM Labs; Chainalysis; FBI public attribution, reported by BleepingComputer.
6. The Bigger Security Lesson: Speed Can Create Vulnerabilities
The attack reportedly involved days of preparation but only around 20 minutes for most of the fund transfers.
The unusual MetaMask transaction may offer an investigative lead, although the alleged human error has not been established.
The incident highlights why cryptocurrency security must extend beyond blockchain transactions to internal systems, wallet infrastructure, transaction services and operational security.
Sources: TRM Labs; independent developer analysis; GCSA forensic investigation.
7. What Happens Next?
Investigators still need to establish whether MetaMask's relevant server logs contain useful evidence, whether any technical identifiers were recorded and whether those records can be connected to the people responsible.
Further cooperation between exchanges, blockchain analytics firms, infrastructure providers and law enforcement may help uncover additional evidence.
Sources: GCSA forensic investigation; TRM Labs.
Conclusion: A Potential Clue Is Not a Confirmed Identification
The Binance hack demonstrates how sophisticated cyberattacks can leave unexpected digital traces. The unusual USDT gas-fee transaction and potential MetaMask server logs could provide useful investigative leads, but the checkbox theory has not been confirmed.
The FBI has attributed the attack to North Korea's TraderTraitor group, but identifying the individual operators is a separate challenge.
The biggest question remains: Could one unusual transaction eventually help investigators uncover the people behind the largest crypto heist in history?
$ESPORTS
{future}(ESPORTSUSDT)
$LYN
{future}(LYNUSDT)
$ONDO
{future}(ONDOUSDT)
#BinanceProcesses$4.65BWithdrawals #WithdrawalsBack: 15 networks live #BinanceUpdatesProofofReservesAddresses
The Binance Hack: Did One Rushed Click Leave a Trail to the Hacker?
Introduction: A Massive Crypto Heist and an Unexpected Clue
On October 29, 2026, approximately $6.36 billion was stolen from Binance wallets across 10 blockchains, with most of the funds transferred in around 20 minutes. TRM Labs reported these figures through its blockchain investigation.
However, another detail attracted attention: a possible MetaMask transaction mistake that could have left an investigative trail. Viral discussions suggested that one checkbox exposed the hacker, but this theory remains unconfirmed.
Sources: TRM Labs; Reuters; independent developer analysis.
1. The Viral Claim: Was the Hacker Exposed by One Checkbox?
The claim suggests that the attacker made a simple mistake while processing a transaction through MetaMask. However, no individual has been identified through this alleged mistake.
The checkbox theory originated from an independent developer's analysis, not an official investigation announcement. An independent forensic review by GCSA also cautioned that the theory remains speculative.
Sources: Independent developer analysis; GCSA forensic investigation.
2. The Unusual Transaction: Paying Gas Fees in USDT Instead of ETH
An independent developer examining the attacker's transactions noticed that the wallet used MetaMask's Gas Station to pay fees in USDT despite holding ETH.
This unusual transaction attracted attention because it involved MetaMask's infrastructure. However, having ETH available does not prove that selecting USDT was accidental.
Sources: Independent developer analysis; GCSA forensic investigation; MetaMask documentation.
3. MetaMask's Gas Station: How One Transaction Could Leave a Digital Trail
MetaMask's Gas Station processes transactions through its service infrastructure. This raised the possibility that server-side records could contain useful technical information, potentially including an IP address.
The developer reportedly asked MetaMask to preserve relevant logs. However, there is no confirmation that an IP address was obtained or that the service identified the attacker.
Sources: Independent developer analysis; GCSA forensic investigation.
4. The Scale of the Incident: Understanding the Numbers
According to the initial reports and subsequent updates:
$6.36 billion: Estimated stolen amount, according to TRM Labs.20 minutes: Approximate time for most of the transfers.10 blockchains: Networks affected, according to TRM Labs.Approximately $2.7–$2.85 billion: Funds frozen or seized, according to TRM Labs and Elliptic.Bitcoin price decline: Approximately 5%, as reported in the original source material.$6 billion: Binance's reported financial reserve to cover losses.
The freezing of stolen stablecoins by Tether and Circle demonstrated how centralized issuers can intervene during major security incidents.
Sources: TRM Labs; Elliptic; Binance statements; Al Jazeera (as listed in the original PDF).
5. Who Is Behind the Attack?
TRM Labs and Chainalysis initially linked the attack to TraderTraitor, associated with North Korea's Lazarus Group.
On November 1, 2026, the FBI officially attributed the theft to North Korea's TraderTraitor group, strengthening the attribution beyond the earlier blockchain analytics assessments.
However, identifying a responsible hacking group does not necessarily reveal the individual operators behind the attack.
Sources: TRM Labs; Chainalysis; FBI public attribution, reported by BleepingComputer.
6. The Bigger Security Lesson: Speed Can Create Vulnerabilities
The attack reportedly involved days of preparation but only around 20 minutes for most of the fund transfers.
The unusual MetaMask transaction may offer an investigative lead, although the alleged human error has not been established.
The incident highlights why cryptocurrency security must extend beyond blockchain transactions to internal systems, wallet infrastructure, transaction services and operational security.
Sources: TRM Labs; independent developer analysis; GCSA forensic investigation.
7. What Happens Next?
Investigators still need to establish whether MetaMask's relevant server logs contain useful evidence, whether any technical identifiers were recorded and whether those records can be connected to the people responsible.
Further cooperation between exchanges, blockchain analytics firms, infrastructure providers and law enforcement may help uncover additional evidence.
Sources: GCSA forensic investigation; TRM Labs.
Conclusion: A Potential Clue Is Not a Confirmed Identification
The Binance hack demonstrates how sophisticated cyberattacks can leave unexpected digital traces. The unusual USDT gas-fee transaction and potential MetaMask server logs could provide useful investigative leads, but the checkbox theory has not been confirmed.
The FBI has attributed the attack to North Korea's TraderTraitor group, but identifying the individual operators is a separate challenge.
The biggest question remains: Could one unusual transaction eventually help investigators uncover the people behind the largest crypto heist in history?
$ESPORTS
$LYN
$ONDO
#BinanceProcesses$4.65BWithdrawals #WithdrawalsBack: 15 networks live #BinanceUpdatesProofofReservesAddresses
On October 29, 2026, approximately $6.36 billion was stolen from Binance wallets across 10 blockchains, with most of the funds transferred in around 20 minutes. TRM Labs reported these figures through its blockchain investigation.
However, another detail attracted attention: a possible MetaMask transaction mistake that could have left an investigative trail. Viral discussions suggested that one checkbox exposed the hacker, but this theory remains unconfirmed.
Sources: TRM Labs; Reuters; independent developer analysis.
1. The Viral Claim: Was the Hacker Exposed by One Checkbox?
The claim suggests that the attacker made a simple mistake while processing a transaction through MetaMask. However, no individual has been identified through this alleged mistake.
The checkbox theory originated from an independent developer's analysis, not an official investigation announcement. An independent forensic review by GCSA also cautioned that the theory remains speculative.
Sources: Independent developer analysis; GCSA forensic investigation.
2. The Unusual Transaction: Paying Gas Fees in USDT Instead of ETH
An independent developer examining the attacker's transactions noticed that the wallet used MetaMask's Gas Station to pay fees in USDT despite holding ETH.
This unusual transaction attracted attention because it involved MetaMask's infrastructure. However, having ETH available does not prove that selecting USDT was accidental.
Sources: Independent developer analysis; GCSA forensic investigation; MetaMask documentation.
3. MetaMask's Gas Station: How One Transaction Could Leave a Digital Trail
MetaMask's Gas Station processes transactions through its service infrastructure. This raised the possibility that server-side records could contain useful technical information, potentially including an IP address.
The developer reportedly asked MetaMask to preserve relevant logs. However, there is no confirmation that an IP address was obtained or that the service identified the attacker.
Sources: Independent developer analysis; GCSA forensic investigation.
4. The Scale of the Incident: Understanding the Numbers
According to the initial reports and subsequent updates:
$6.36 billion: Estimated stolen amount, according to TRM Labs.20 minutes: Approximate time for most of the transfers.10 blockchains: Networks affected, according to TRM Labs.Approximately $2.7–$2.85 billion: Funds frozen or seized, according to TRM Labs and Elliptic.Bitcoin price decline: Approximately 5%, as reported in the original source material.$6 billion: Binance's reported financial reserve to cover losses.
The freezing of stolen stablecoins by Tether and Circle demonstrated how centralized issuers can intervene during major security incidents.
Sources: TRM Labs; Elliptic; Binance statements; Al Jazeera (as listed in the original PDF).
5. Who Is Behind the Attack?
TRM Labs and Chainalysis initially linked the attack to TraderTraitor, associated with North Korea's Lazarus Group.
On November 1, 2026, the FBI officially attributed the theft to North Korea's TraderTraitor group, strengthening the attribution beyond the earlier blockchain analytics assessments.
However, identifying a responsible hacking group does not necessarily reveal the individual operators behind the attack.
Sources: TRM Labs; Chainalysis; FBI public attribution, reported by BleepingComputer.
6. The Bigger Security Lesson: Speed Can Create Vulnerabilities
The attack reportedly involved days of preparation but only around 20 minutes for most of the fund transfers.
The unusual MetaMask transaction may offer an investigative lead, although the alleged human error has not been established.
The incident highlights why cryptocurrency security must extend beyond blockchain transactions to internal systems, wallet infrastructure, transaction services and operational security.
Sources: TRM Labs; independent developer analysis; GCSA forensic investigation.
7. What Happens Next?
Investigators still need to establish whether MetaMask's relevant server logs contain useful evidence, whether any technical identifiers were recorded and whether those records can be connected to the people responsible.
Further cooperation between exchanges, blockchain analytics firms, infrastructure providers and law enforcement may help uncover additional evidence.
Sources: GCSA forensic investigation; TRM Labs.
Conclusion: A Potential Clue Is Not a Confirmed Identification
The Binance hack demonstrates how sophisticated cyberattacks can leave unexpected digital traces. The unusual USDT gas-fee transaction and potential MetaMask server logs could provide useful investigative leads, but the checkbox theory has not been confirmed.
The FBI has attributed the attack to North Korea's TraderTraitor group, but identifying the individual operators is a separate challenge.
The biggest question remains: Could one unusual transaction eventually help investigators uncover the people behind the largest crypto heist in history?
$ESPORTS
$LYN
$ONDO
#BinanceProcesses$4.65BWithdrawals #WithdrawalsBack: 15 networks live #BinanceUpdatesProofofReservesAddresses
1
3
1.7k
·
--
Bullish
Is Alphabet’s plunge the start of a bigger AI stock correction?
$Q
{future}(QUSDT)
$MAGMA
{future}(MAGMAUSDT)
$AIN
{future}(AINUSDT)
Is Alphabet’s plunge the start of a bigger AI stock correction?
$Q
$MAGMA
$AIN
$Q
$MAGMA
$AIN
📉 Tech sell-off deepens
21%
🚀 Buy the dip
61%
⚖️ Earnings will decide
7%
🤖 AI valuations face reality
11%
28 votes • Voting closed
5
3.5k
·
--
Verified
The S&P 500 is becoming a market of winners and losers, and investors may need to rethink their strategy.
Societe Generale data shows around 40% of possible S&P 500 stock pairs are negatively correlated, with overall correlations below historical norms.
That could create more opportunities for stock pickers and diversification, but index gains may hide growing gaps between individual companies.
Is this a golden opportunity for selective investors, or a warning that market uncertainty is rising?
#SP500 #Stocks #Investing
$MAGMA
{future}(MAGMAUSDT)
$HYPE
{future}(HYPEUSDT)
$LSK
{future}(LSKUSDT)
The S&P 500 is becoming a market of winners and losers, and investors may need to rethink their strategy.
Societe Generale data shows around 40% of possible S&P 500 stock pairs are negatively correlated, with overall correlations below historical norms.
That could create more opportunities for stock pickers and diversification, but index gains may hide growing gaps between individual companies.
Is this a golden opportunity for selective investors, or a warning that market uncertainty is rising?
#SP500 #Stocks #Investing
$MAGMA
$HYPE
$LSK
Societe Generale data shows around 40% of possible S&P 500 stock pairs are negatively correlated, with overall correlations below historical norms.
That could create more opportunities for stock pickers and diversification, but index gains may hide growing gaps between individual companies.
Is this a golden opportunity for selective investors, or a warning that market uncertainty is rising?
#SP500 #Stocks #Investing
$MAGMA
$HYPE
$LSK
1
628
·
--
Bullish
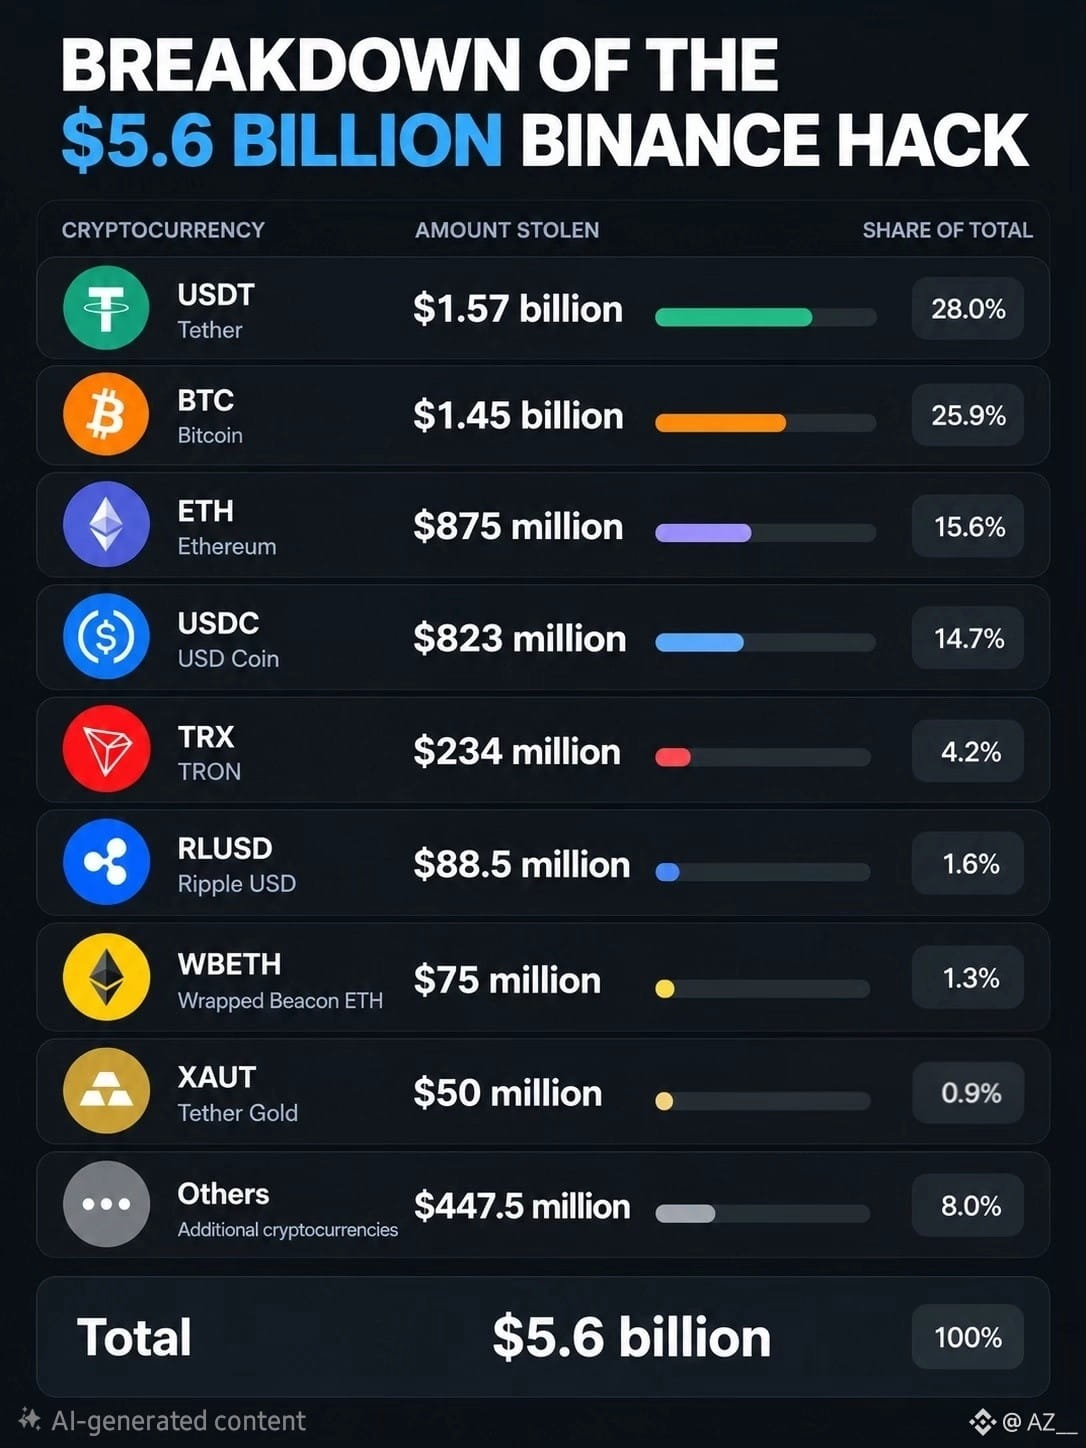
Binance Got Hacked
This is potentialy the Biggest Crypto Hack in History, with $5.6 Billion Reportedly Stolen.
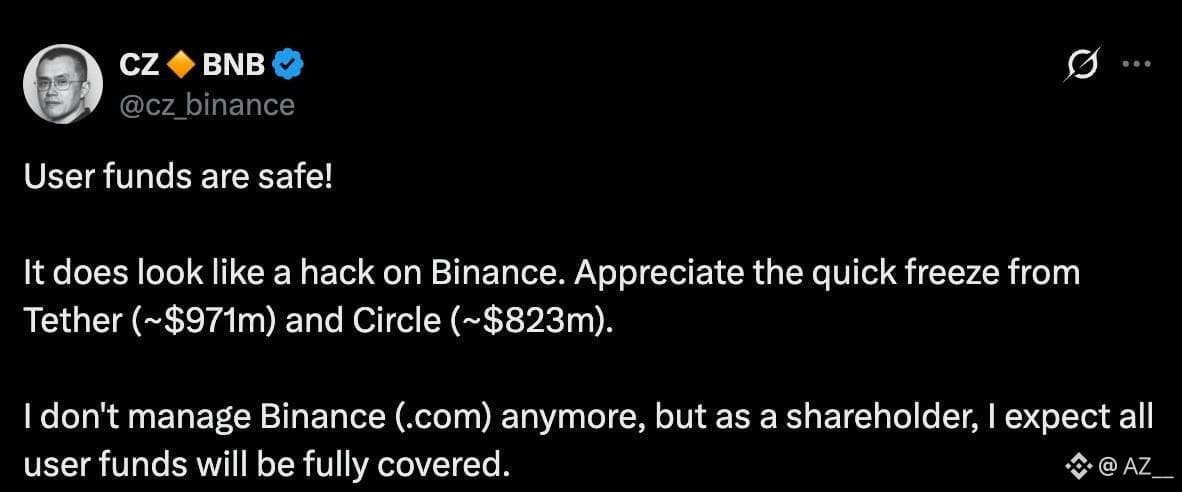
Luckly, Tether managed to Frezze over $1.567 Billion, While Circlee Froze another $823 Million.
Binance Founder @CZ assures users their funds are safe and expacts all user funds to be fully recovered.
$PREDICT
{future}(PREDICTUSDT)
$SUI
{future}(SUIUSDT)
$SIREN
{future}(SIRENUSDT)
Binance Got Hacked
This is potentialy the Biggest Crypto Hack in History, with $5.6 Billion Reportedly Stolen.
Luckly, Tether managed to Frezze over $1.567 Billion, While Circlee Froze another $823 Million.
Binance Founder @CZ assures users their funds are safe and expacts all user funds to be fully recovered.
$PREDICT
$SUI
$SIREN
This is potentialy the Biggest Crypto Hack in History, with $5.6 Billion Reportedly Stolen.
Luckly, Tether managed to Frezze over $1.567 Billion, While Circlee Froze another $823 Million.
Binance Founder @CZ assures users their funds are safe and expacts all user funds to be fully recovered.
$PREDICT
$SUI
$SIREN
1
1k
·
--
Bullish
Is the S&P 500 becoming a stock picker's market?
$LSK
{future}(LSKUSDT)
$ZEC
{future}(ZECUSDT)
$ONDO
{future}(ONDOUSDT)
Is the S&P 500 becoming a stock picker's market?
$LSK
$ZEC
$ONDO
$LSK
$ZEC
$ONDO
📊 Yes, stock selection matter
63%
🚀 Broad rally is coming
14%
🛡️ Diversification matters
14%
⚠️ Market signals are unclear
9%
22 votes • Voting closed
1
5.2k
·
--
Bearish
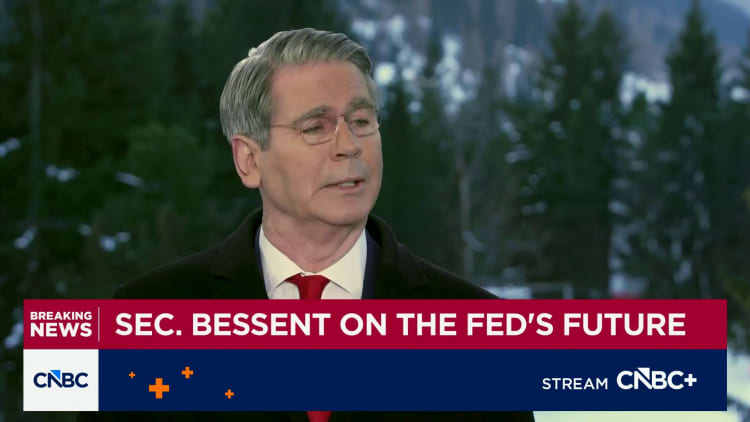
The next Fed surprise could be another rate hike and markets may not be ready for it.
Treasury Secretary Scott Bessent says future rate increases wouldn't necessarily be a policy mistake, pointing to signs of strong U.S. economic growth.
But persistent energy inflation complicates the outlook, potentially pressuring bonds, raising borrowing costs, and weighing on risk assets.
If growth stays strong while inflation remains stubborn, are investors too confident that rate cuts are coming?
#FederalReserve #interestrates #markets
$ZEC
{future}(ZECUSDT)
$ONDO
{future}(ONDOUSDT)
$SUI
{future}(SUIUSDT)
The next Fed surprise could be another rate hike and markets may not be ready for it.
Treasury Secretary Scott Bessent says future rate increases wouldn't necessarily be a policy mistake, pointing to signs of strong U.S. economic growth.
But persistent energy inflation complicates the outlook, potentially pressuring bonds, raising borrowing costs, and weighing on risk assets.
If growth stays strong while inflation remains stubborn, are investors too confident that rate cuts are coming?
#FederalReserve #interestrates #markets
$ZEC
$ONDO
$SUI
Treasury Secretary Scott Bessent says future rate increases wouldn't necessarily be a policy mistake, pointing to signs of strong U.S. economic growth.
But persistent energy inflation complicates the outlook, potentially pressuring bonds, raising borrowing costs, and weighing on risk assets.
If growth stays strong while inflation remains stubborn, are investors too confident that rate cuts are coming?
#FederalReserve #interestrates #markets
$ZEC
$ONDO
$SUI
782
·
--
What matters most to investors right now?
$BMT
{future}(BMTUSDT)
$BIRB
{future}(BIRBUSDT)
$LA
{future}(LAUSDT)
What matters most to investors right now?
$BMT
$BIRB
$LA
$BMT
$BIRB
$LA
📉 Economic uncertainty
64%
⚖️ Government corruption
22%
🗳️ Midterm election results
14%
14 votes • Voting closed
1.4k
·
--
Bullish
Is Western Digital’s sell-off a buying opportunity or a warning sign?
$IRYS
{future}(IRYSUSDT)
$BIRB
{future}(BIRBUSDT)
$ERA
{future}(ERAUSDT)
Is Western Digital’s sell-off a buying opportunity or a warning sign?
$IRYS
$BIRB
$ERA
$IRYS
$BIRB
$ERA
🚀 Buy the dip
66%
📉 More downside ahead
26%
💰 Capex concerns overblown
4%
⏳ Wait for more clarity
4%
27 votes • Voting closed
3.8k
·
--
Bullish
PREMARKET MOVERS: What would you watch first?
$SKYAI
{future}(SKYAIUSDT)
$PEPE
{spot}(PEPEUSDT)
$IRYS
{future}(IRYSUSDT)
PREMARKET MOVERS: What would you watch first?
$SKYAI
$PEPE
$IRYS
$SKYAI
$PEPE
$IRYS
🚀 Momentum breakout
53%
🔍 Wait for confirmation
12%
📉 Fade the gap up
35%
17 votes • Voting closed
1.4k
·
--
Bullish
✅ Already voted!
84%
🔥 Bro, you already know! 😎
16%
80 votes • Voting closed
1.7k
5
97
2.4k
·
--
Bullish
What will quantum computing change first?
$KERNEL
{future}(KERNELUSDT)
$ENSO
{future}(ENSOUSDT)
$JCT
{future}(JCTUSDT)
🚨 NVIDIA just pushed quantum computing another step forward.
On Europe’s largest supercomputer, Jupiter, researchers simulated a 104-qubit fault-tolerant system using 90% fewer physical qubits than previous attempts, according to NVIDIA.
Why it matters: quantum computing could eventually transform drug discovery, financial modeling, and materials science.
But the real breakthrough may be the combination of GPUs and quantum processors, not either technology alone.
Is this a glimpse of the next computing revolution, or are practical quantum applications still years away?
#NVIDIA #QuantumComputing #AI
What will quantum computing change first?
$KERNEL
$ENSO
$JCT
🚨 NVIDIA just pushed quantum computing another step forward.
On Europe’s largest supercomputer, Jupiter, researchers simulated a 104-qubit fault-tolerant system using 90% fewer physical qubits than previous attempts, according to NVIDIA.
Why it matters: quantum computing could eventually transform drug discovery, financial modeling, and materials science.
But the real breakthrough may be the combination of GPUs and quantum processors, not either technology alone.
Is this a glimpse of the next computing revolution, or are practical quantum applications still years away?
#NVIDIA #QuantumComputing #AI
$KERNEL
$ENSO
$JCT
🚨 NVIDIA just pushed quantum computing another step forward.
On Europe’s largest supercomputer, Jupiter, researchers simulated a 104-qubit fault-tolerant system using 90% fewer physical qubits than previous attempts, according to NVIDIA.
Why it matters: quantum computing could eventually transform drug discovery, financial modeling, and materials science.
But the real breakthrough may be the combination of GPUs and quantum processors, not either technology alone.
Is this a glimpse of the next computing revolution, or are practical quantum applications still years away?
#NVIDIA #QuantumComputing #AI
💊 Drug discovery
0%
📈 Finance & trading
75%
🧪 Materials science
25%
4 votes • Voting closed
1
2
2.7k
·
--
Bullish
AI’s biggest threat might NOT be a bubble. It might be running out of power.
BlackRock CEO Larry Fink sees shortages, not speculation, as the bigger risk to the AI boom.
Think about it, no matter how powerful AI becomes, it still needs chips, memory, electricity, and skilled workers to scale.
The next big AI bottleneck may not be intelligence. It may be infrastructure.
What will limit AI growth the most?
#AI #BlackRock #TechStocks .
$PHA
{future}(PHAUSDT)
$BR
{future}(BRUSDT)
$BMT
{future}(BMTUSDT)
AI’s biggest threat might NOT be a bubble. It might be running out of power.
BlackRock CEO Larry Fink sees shortages, not speculation, as the bigger risk to the AI boom.
Think about it, no matter how powerful AI becomes, it still needs chips, memory, electricity, and skilled workers to scale.
The next big AI bottleneck may not be intelligence. It may be infrastructure.
What will limit AI growth the most?
#AI #BlackRock #TechStocks .
$PHA
$BR
$BMT
BlackRock CEO Larry Fink sees shortages, not speculation, as the bigger risk to the AI boom.
Think about it, no matter how powerful AI becomes, it still needs chips, memory, electricity, and skilled workers to scale.
The next big AI bottleneck may not be intelligence. It may be infrastructure.
What will limit AI growth the most?
#AI #BlackRock #TechStocks .
$PHA
$BR
$BMT
⚡ Power & energy shortages
0%
🖥️ Chips & memory shortages
33%
👷 Skilled worker shortages
67%
3 votes • Voting closed
1
1k
·
--
Bearish
What should require human approval?
The biggest risk with an AI agent may not be what it thinks. It may be what it’s allowed to do.
A model can be impressive at planning, but once it can spend money, call paid APIs, or act across services, a bad decision stops being just a bad answer. It can become a real transaction.
What caught my attention in Kite’s design is the separation between the user, the agent, and the session. The user remains the root authority; the agent receives delegated permissions; and a session can be limited to a specific task or period. That creates a clearer boundary between asking an AI to help and giving it the power to act.
Kite’s approach also puts programmable constraints at the infrastructure level. Spending limits and permitted actions are meant to be enforced through cryptographic authorization and smart-contract logic, not merely written into a prompt and hoped for the best.
To me, that’s a more useful way to think about AI safety in financial workflows. We probably won’t eliminate every model error. But we can design systems where one error doesn’t automatically become unlimited authority.
The question I’m left with is this: if an agent has a clear identity, limited permissions, and an auditable trail, what should still require human approval? I’d draw the line differently for a small API payment than for moving funds between accounts.
That permission boundary may be just as important as the intelligence behind the agent.
#KiteBBW $KITE @GoKiteAI
{future}(KITEUSDT)
What should require human approval?
The biggest risk with an AI agent may not be what it thinks. It may be what it’s allowed to do.
A model can be impressive at planning, but once it can spend money, call paid APIs, or act across services, a bad decision stops being just a bad answer. It can become a real transaction.
What caught my attention in Kite’s design is the separation between the user, the agent, and the session. The user remains the root authority; the agent receives delegated permissions; and a session can be limited to a specific task or period. That creates a clearer boundary between asking an AI to help and giving it the power to act.
Kite’s approach also puts programmable constraints at the infrastructure level. Spending limits and permitted actions are meant to be enforced through cryptographic authorization and smart-contract logic, not merely written into a prompt and hoped for the best.
To me, that’s a more useful way to think about AI safety in financial workflows. We probably won’t eliminate every model error. But we can design systems where one error doesn’t automatically become unlimited authority.
The question I’m left with is this: if an agent has a clear identity, limited permissions, and an auditable trail, what should still require human approval? I’d draw the line differently for a small API payment than for moving funds between accounts.
That permission boundary may be just as important as the intelligence behind the agent.
#KiteBBW $KITE @KITE AI 中文
The biggest risk with an AI agent may not be what it thinks. It may be what it’s allowed to do.
A model can be impressive at planning, but once it can spend money, call paid APIs, or act across services, a bad decision stops being just a bad answer. It can become a real transaction.
What caught my attention in Kite’s design is the separation between the user, the agent, and the session. The user remains the root authority; the agent receives delegated permissions; and a session can be limited to a specific task or period. That creates a clearer boundary between asking an AI to help and giving it the power to act.
Kite’s approach also puts programmable constraints at the infrastructure level. Spending limits and permitted actions are meant to be enforced through cryptographic authorization and smart-contract logic, not merely written into a prompt and hoped for the best.
To me, that’s a more useful way to think about AI safety in financial workflows. We probably won’t eliminate every model error. But we can design systems where one error doesn’t automatically become unlimited authority.
The question I’m left with is this: if an agent has a clear identity, limited permissions, and an auditable trail, what should still require human approval? I’d draw the line differently for a small API payment than for moving funds between accounts.
That permission boundary may be just as important as the intelligence behind the agent.
#KiteBBW $KITE @KITE AI 中文
1. 💸 Large transfers
0%
2. 🔐 Actions beyond limits
0%
3. ⚖️ High-risk actions
100%
1 votes • Voting closed
1
3
276
·
--
Bullish
Big News, Binancian Family! 💛🏆
I'm excited to share that I've been selected as a Rising Star Nominee for The 2026 Blockchain 100 Awards! 🚀
This nomination means a lot to me, and now I need your support to take it to the next level.
🗳️ How to Vote for AZ__
01. Go to my profile: AZ__
02. Find the The 2026 Blockchain 100 Awards section.
03. Click the Vote button. That's it!
Every single vote counts, and your support can make a real difference. ❤️
If you've been following my journey, now is the perfect time to stand with me. Let's show the strength of our community and bring this Rising Star nomination home!
Go to AZ__'s profile and hit that Vote button! 🔥
Thank you for being part of this journey. Let's make it happen! 🫡🏆
#Blockchain100 #RisingStar #BinanceCommunity
$GTC
{future}(GTCUSDT)
$GRVT
{future}(GRVTUSDT)
$NIL
{future}(NILUSDT)
Big News, Binancian Family! 💛🏆
I'm excited to share that I've been selected as a Rising Star Nominee for The 2026 Blockchain 100 Awards! 🚀
This nomination means a lot to me, and now I need your support to take it to the next level.
🗳️ How to Vote for AZ__
01. Go to my profile: AZ__
02. Find the The 2026 Blockchain 100 Awards section.
03. Click the Vote button. That's it!
Every single vote counts, and your support can make a real difference. ❤️
If you've been following my journey, now is the perfect time to stand with me. Let's show the strength of our community and bring this Rising Star nomination home!
Go to AZ__'s profile and hit that Vote button! 🔥
Thank you for being part of this journey. Let's make it happen! 🫡🏆
#Blockchain100 #RisingStar #BinanceCommunity
$GTC
$GRVT
$NIL
I'm excited to share that I've been selected as a Rising Star Nominee for The 2026 Blockchain 100 Awards! 🚀
This nomination means a lot to me, and now I need your support to take it to the next level.
🗳️ How to Vote for AZ__
01. Go to my profile: AZ__
02. Find the The 2026 Blockchain 100 Awards section.
03. Click the Vote button. That's it!
Every single vote counts, and your support can make a real difference. ❤️
If you've been following my journey, now is the perfect time to stand with me. Let's show the strength of our community and bring this Rising Star nomination home!
Go to AZ__'s profile and hit that Vote button! 🔥
Thank you for being part of this journey. Let's make it happen! 🫡🏆
#Blockchain100 #RisingStar #BinanceCommunity
$GTC
$GRVT
$NIL
3
2
12
245
·
--
Verified
Building the Next Era of Privacy for Web3
The more I explore the future of blockchain, the more I believe that transparency alone isn't enough. We need systems that can protect sensitive information while still allowing applications to work intelligently.
That's why @nillionnetwork has caught my attention.
1. Covenants: Privacy With a Purpose
What excites me most about Covenants is the idea of encrypted instructions that remain sealed until predefined conditions are satisfied. Instead of exposing every instruction immediately, applications can control when those instructions become actionable.
This could open new possibilities for programmable privacy across Web3.
2. DUSK: The First Step on Ethereum
With Dusk as the first release in Nillion's Covenants roadmap on Ethereum mainnet, the vision moves toward practical applications. It creates an exciting foundation for exploring how encrypted instructions can work within Ethereum's existing ecosystem.
3. A New Possibility for Trading
As a crypto enthusiast, I find the concept of Encrypted Markets particularly interesting. Trading strategies, order conditions and other sensitive instructions can reveal valuable information when exposed too early.
Privacy preserving mechanisms could help developers explore new market designs where sensitive instructions stay protected until the appropriate conditions are met.
4. Privacy Meets Automation
Imagine conditional payments, sealed trading orders or auctions where instructions are not revealed before their intended execution conditions are satisfied.
These are potential applications worth exploring. Covenants could help make privacy a programmable feature rather than an afterthought.
#nil $NIL @nillionnetwork
Building the Next Era of Privacy for Web3
The more I explore the future of blockchain, the more I believe that transparency alone isn't enough. We need systems that can protect sensitive information while still allowing applications to work intelligently.
That's why @Nillion has caught my attention.
1. Covenants: Privacy With a Purpose
What excites me most about Covenants is the idea of encrypted instructions that remain sealed until predefined conditions are satisfied. Instead of exposing every instruction immediately, applications can control when those instructions become actionable.
This could open new possibilities for programmable privacy across Web3.
2. DUSK: The First Step on Ethereum
With Dusk as the first release in Nillion's Covenants roadmap on Ethereum mainnet, the vision moves toward practical applications. It creates an exciting foundation for exploring how encrypted instructions can work within Ethereum's existing ecosystem.
3. A New Possibility for Trading
As a crypto enthusiast, I find the concept of Encrypted Markets particularly interesting. Trading strategies, order conditions and other sensitive instructions can reveal valuable information when exposed too early.
Privacy preserving mechanisms could help developers explore new market designs where sensitive instructions stay protected until the appropriate conditions are met.
4. Privacy Meets Automation
Imagine conditional payments, sealed trading orders or auctions where instructions are not revealed before their intended execution conditions are satisfied.
These are potential applications worth exploring. Covenants could help make privacy a programmable feature rather than an afterthought.
#nil $NIL @Nillion
The more I explore the future of blockchain, the more I believe that transparency alone isn't enough. We need systems that can protect sensitive information while still allowing applications to work intelligently.
That's why @Nillion has caught my attention.
1. Covenants: Privacy With a Purpose
What excites me most about Covenants is the idea of encrypted instructions that remain sealed until predefined conditions are satisfied. Instead of exposing every instruction immediately, applications can control when those instructions become actionable.
This could open new possibilities for programmable privacy across Web3.
2. DUSK: The First Step on Ethereum
With Dusk as the first release in Nillion's Covenants roadmap on Ethereum mainnet, the vision moves toward practical applications. It creates an exciting foundation for exploring how encrypted instructions can work within Ethereum's existing ecosystem.
3. A New Possibility for Trading
As a crypto enthusiast, I find the concept of Encrypted Markets particularly interesting. Trading strategies, order conditions and other sensitive instructions can reveal valuable information when exposed too early.
Privacy preserving mechanisms could help developers explore new market designs where sensitive instructions stay protected until the appropriate conditions are met.
4. Privacy Meets Automation
Imagine conditional payments, sealed trading orders or auctions where instructions are not revealed before their intended execution conditions are satisfied.
These are potential applications worth exploring. Covenants could help make privacy a programmable feature rather than an afterthought.
#nil $NIL @Nillion
4
9
232
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
BinanceReopensWithdrawalsForMoreAssets
910,725 views
4,726 Discussing
Security Incident | Recovery Update #8: Withdrawals for More Assets to Reopen (2026-11-05)
Binance Announcement
·423 Likes
·1.9M views
Binance98PercentReplenished
222,462 views
1,945 Discussing
USStocksSlipandCryptoMarketUnderBroadPressure
25,383 views
284 Discussing