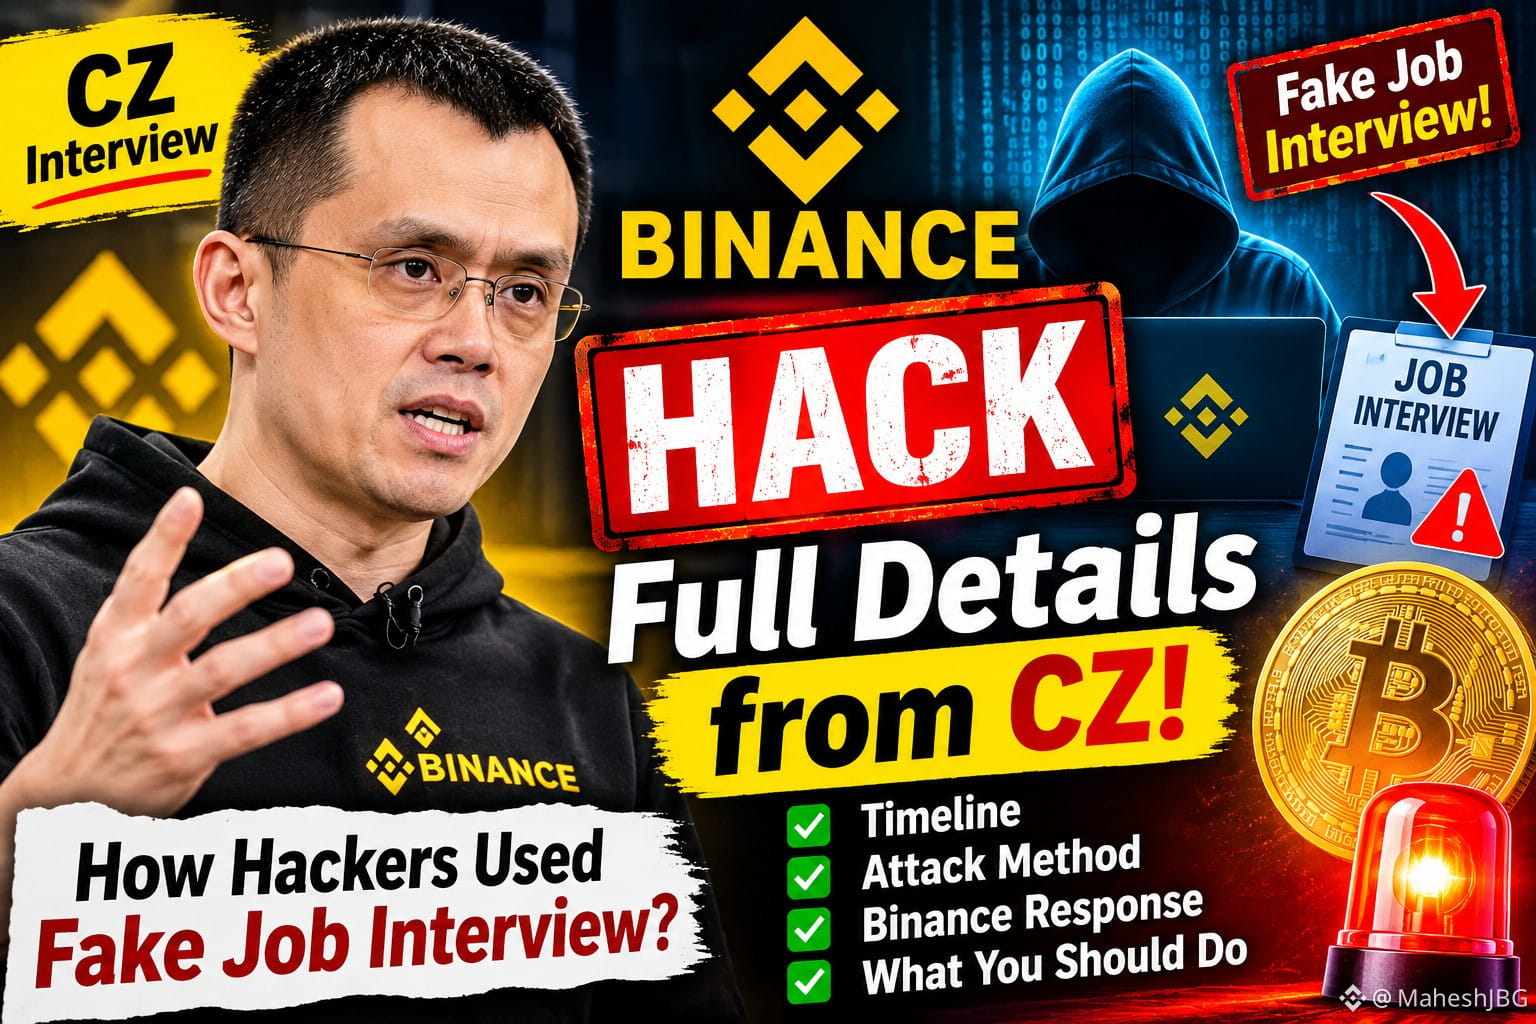
According to Binance's incident briefing and CZ's public comments, the attack was not a simple hack—it was a highly targeted, months-long social engineering operation.
Timeline of the attack
- June 2026: An engineer downloaded a malicious developer tool disguised as legitimate software. The malware gave attackers an initial foothold.
- September 2026: Another Binance engineer was contacted through a fake job interview. During the interview process, the engineer was asked to download and run a "technical assessment," which secretly installed malware.
- October 20: Attackers used the compromised devices and abused an internal AI tool to expand access inside Binance's systems.
- October 29: Using stolen credentials, the attackers executed malicious scripts and drained assets from internet-connected hot wallets within minutes. Binance froze roughly $2.8–3.0 billion, but about $6.3 billion in crypto was affected overall.
What CZ said
In his first interview after the incident, CZ emphasized:
- The crypto industry must cooperate more closely on security.
- AI is helping both attackers and defenders, so exchanges need stronger AI-powered detection.
- Exchanges should share threat intelligence and freeze stolen assets faster across the industry.
- Binance will compensate affected users and continue investing heavily in cybersecurity.
Lessons for crypto users
- Never install software sent by unknown recruiters or interviewers.
- Use a separate device for work and crypto whenever possible.
- Enable hardware-based 2FA instead of SMS.
- Verify recruiters and companies before downloading coding tests or assignments.
- Be cautious of unsolicited LinkedIn or Telegram job offers.
$BNB $ETH $XRP
Timeline of the attack
- June 2026: An engineer downloaded a malicious developer tool disguised as legitimate software. The malware gave attackers an initial foothold.
- September 2026: Another Binance engineer was contacted through a fake job interview. During the interview process, the engineer was asked to download and run a "technical assessment," which secretly installed malware.
- October 20: Attackers used the compromised devices and abused an internal AI tool to expand access inside Binance's systems.
- October 29: Using stolen credentials, the attackers executed malicious scripts and drained assets from internet-connected hot wallets within minutes. Binance froze roughly $2.8–3.0 billion, but about $6.3 billion in crypto was affected overall.
What CZ said
In his first interview after the incident, CZ emphasized:
- The crypto industry must cooperate more closely on security.
- AI is helping both attackers and defenders, so exchanges need stronger AI-powered detection.
- Exchanges should share threat intelligence and freeze stolen assets faster across the industry.
- Binance will compensate affected users and continue investing heavily in cybersecurity.
Lessons for crypto users
- Never install software sent by unknown recruiters or interviewers.
- Use a separate device for work and crypto whenever possible.
- Enable hardware-based 2FA instead of SMS.
- Verify recruiters and companies before downloading coding tests or assignments.
- Be cautious of unsolicited LinkedIn or Telegram job offers.
$BNB $ETH $XRP