
The internet is going wild! Binance has just released the full investigation report on the epic $6.3 billion theft!
Everyone used to think that breaching a top-tier exchange had to involve an insanely sophisticated code exploit, elite hackers brute-forcing their way in, or the system’s defenses collapsing.
But the truth is chilling—and completely upends everything we thought we knew!
The largest theft in crypto history (over $6.3 billion)
didn’t involve breaching a top-tier firewall or exploiting a vulnerability in the system’s code.
It stemmed from nothing more than a “fake job interview” that an ordinary person would never suspect was a setup.
The perpetrators: North Korea’s elite hacking group
A meticulously executed hunt from start to finish, exploiting human nature to perfection, with layers of planning and not a single detail missed!
After hearing the full story, crypto veterans, A8/A9 big holders, and longtime traders all fell silent:
It turns out the crypto industry’s biggest risk has never been a market crash or unfavorable policies, but human traps that are impossible to guard against!
The full story: a textbook case of high-level infiltration and fraud
The entire operation was a masterclass in cybercrime. The patience, attention to detail, and level of disguise were terrifying!
Step one: Precisely identify the target (zero in on an internal engineer)
A software engineer currently working at Binance updated their résumé and profile on a job site as usual.
It was just an ordinary workplace action—they were simply looking for new opportunities.
Who could have imagined?
North Korean hackers, who had long been lying in wait and monitoring the crypto industry, immediately singled them out!
The hackers posed as a “project director” at a legitimate company
and reached out directly: they had a well-paid, high-quality technical role and wanted to discuss it in depth.
Their communication was professional throughout, logically sound, and seemingly flawless.
Step two: An immersive disguise that completely lowered every defense
To earn absolute trust, the hackers’ setup was nothing short of flawless:
Round one: A real person appeared on camera for an HR video interview. The conversation was normal throughout, and the interviewer came across as highly professional.
To dispel any doubts, the HR representative proactively shared their real, full personal social media account.
The account had it all: real-life photos, everyday videos, and regular updates.
It looked exactly like the account of a completely genuine, ordinary person living a normal life.
Nothing unusual, no ads, no sign of marketing.
Faced with a real person on camera, genuine social media posts, and a formal interview process, anyone would let their guard down completely.
Step three: Escalating the contact—an in-depth conversation with a fake CEO
The second interview went straight to the next level!
They switched to a familiar messaging app and connected with the person supposedly serving as the company’s CEO.
The one-on-one technical discussion was in-depth throughout, and the person came across as professional and insightful.
The entire formal interview process was completed,
and no one could tell that from beginning to end, the company and every persona involved had been fabricated by hackers!
Step four: The final blow—a coding assignment that looked entirely routine
Near the end of the interview, the CEO made an entirely reasonable request:
“Complete a technical coding test to demonstrate your practical skills.”
With no suspicion, the engineer downloaded and ran the code file directly on their Binance work computer.
This seemingly routine workplace task
pierced every defense at the world’s largest exchange!
The malicious code was exceptionally stealthy:
It automatically replaced the computer’s legitimate development tools and planted a deep-rooted Trojan
It silently connected to the hackers’ remote server and automatically erased all traces of the intrusion
Most terrifying of all:
Binance’s top-tier antivirus software and endpoint protection systems raised no alerts and blocked nothing!
More than a month lying low, penetrating layer by layer, straight into the vault
After successfully planting the Trojan, the hackers stayed calm and avoided making any rash moves.
They lay low, observed, explored, infiltrated, and escalated their privileges.
Using this one compromised internal computer,
they moved laterally through Binance’s internal network, harvested credentials, mapped the underlying wallet architecture, and bypassed every risk control.
More than a full month of silent persistence!
Right under the nose of Binance’s top security team,
they quietly established a path to the core wallet privileges.
Finally, on October 30, they struck with precision!
In 20 minutes, across multiple blockchains, they transferred more than $6.3 billion in assets!
A top-tier exchange, top-tier risk controls, and billions invested in security
were defeated by a fake interview that an ordinary person could never have seen through!
The ultimate hidden risk that should terrify everyone (and that no one online is emphasizing)
According to the latest investigation:
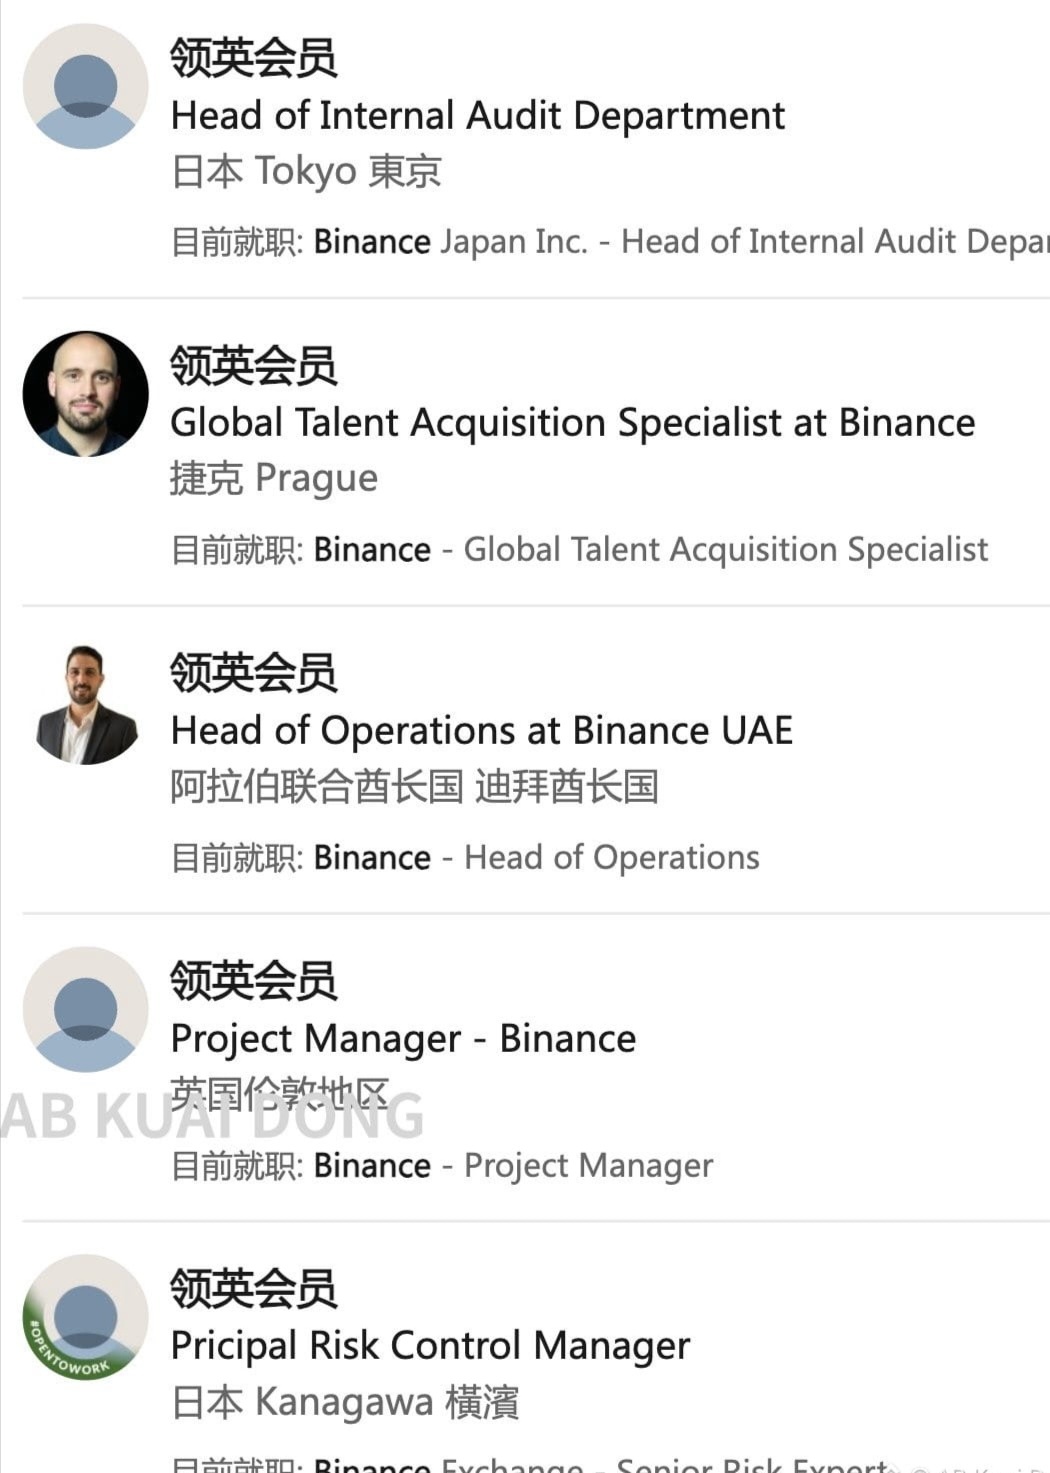
There are still countless public résumés from current Binance employees on job platforms such as LinkedIn!
This means:
North Korean hackers’ target list is still active!
Attacks using the same kind of highly targeted infiltration could be repeated at any time!
This was no random attack.
It was a sophisticated, replicable, scalable criminal playbook for systematically looting exchanges!
The truth that resonates with every crypto trader
We used to watch candlestick charts every day, analyze the market, brace for crashes, and weather volatility
We feared sharp drops, market manipulation, unfavorable policies, and getting dumped on
Only now do we finally understand: all the risks we were guarding against were minor!
The truly catastrophic risk has never been market movements.
It’s elite, state-sponsored hackers exploiting human weaknesses to precisely breach every financial defense.
Code can be iterated endlessly, and systems can be encrypted layer upon layer
but human complacency and routine workplace requests can never be completely blocked out!
That’s also why:
after the turmoil, all the A8 and A9 holders with tens or hundreds of millions
moved their funds straight into cold wallets as fast as they could—as long as withdrawals were available!
The big players understand better than most:
No matter how big the platform, how famous the name, or how strong the risk controls, nothing is absolutely safe.
You can earn back what you lose in the market, and wait for another chance if you miss a move
but once your principal is wiped out, there’s no coming back.
A $6.3 billion lesson for everyone working in crypto:
Always respect risk, and never place absolute trust in any centralized platform.
Protect your livelihood first; protect your capital before chasing profits,
Only those who survive a black swan event are truly winners in this industry!#币安10·30安全事件调查报告 #币安将恢复更多资产提现