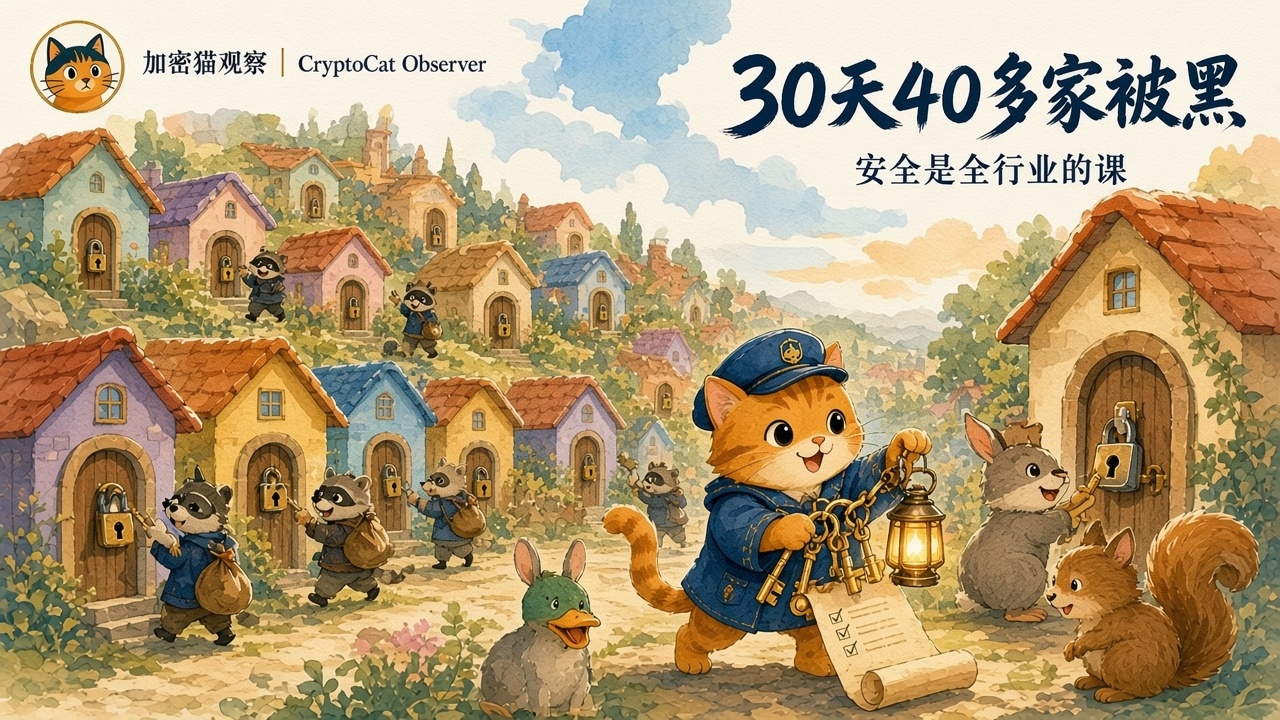
Early on the morning of November 4 (UTC+8), CZ reposted a list: in the 30 days from October 6 to November 2, more than 40 companies and crypto projects were hacked. Binance was just one of them. The list also included familiar names such as Polymarket, Ledger, Chainalysis, and GitBook, as well as a number of AI and developer-tool platforms.
After Binance published its preliminary investigation report on November 3, many people criticized its engineers for making a basic mistake. SlowMist founder Yu Xian said on X that it’s easiest to sit back and watch—but when you’re the one being targeted, you realize how many tricks the other side has: exploiting human nature, scouting in advance, and getting malicious code past antivirus software. Each step leads to the next.
The report made it clear that preparations for this attack began in June. First, the attackers placed altered versions of commonly used tools in search ads. Then, in September, they used a fake job interview to trick an engineer into running code with a backdoor hidden in it. Binance also noted that since the start of 2026, its security team has blocked 57 similar suspicious attacks.
Ordinary users should watch out for these tactics too: download software only from official websites, and don’t click ads in search results; don’t casually open “test assignments” or “documents” sent by strangers; and keep your seed phrase to yourself.
Binance has pledged to cover the losses, ensuring users won’t be affected, and withdrawals are being restored in stages. There’s no such thing as permanent security; the whole industry needs to learn from this incident.
#币安 #BNB #安全 does not constitute investment advice
After Binance published its preliminary investigation report on November 3, many people criticized its engineers for making a basic mistake. SlowMist founder Yu Xian said on X that it’s easiest to sit back and watch—but when you’re the one being targeted, you realize how many tricks the other side has: exploiting human nature, scouting in advance, and getting malicious code past antivirus software. Each step leads to the next.
The report made it clear that preparations for this attack began in June. First, the attackers placed altered versions of commonly used tools in search ads. Then, in September, they used a fake job interview to trick an engineer into running code with a backdoor hidden in it. Binance also noted that since the start of 2026, its security team has blocked 57 similar suspicious attacks.
Ordinary users should watch out for these tactics too: download software only from official websites, and don’t click ads in search results; don’t casually open “test assignments” or “documents” sent by strangers; and keep your seed phrase to yourself.
Binance has pledged to cover the losses, ensuring users won’t be affected, and withdrawals are being restored in stages. There’s no such thing as permanent security; the whole industry needs to learn from this incident.
#币安 #BNB #安全 does not constitute investment advice