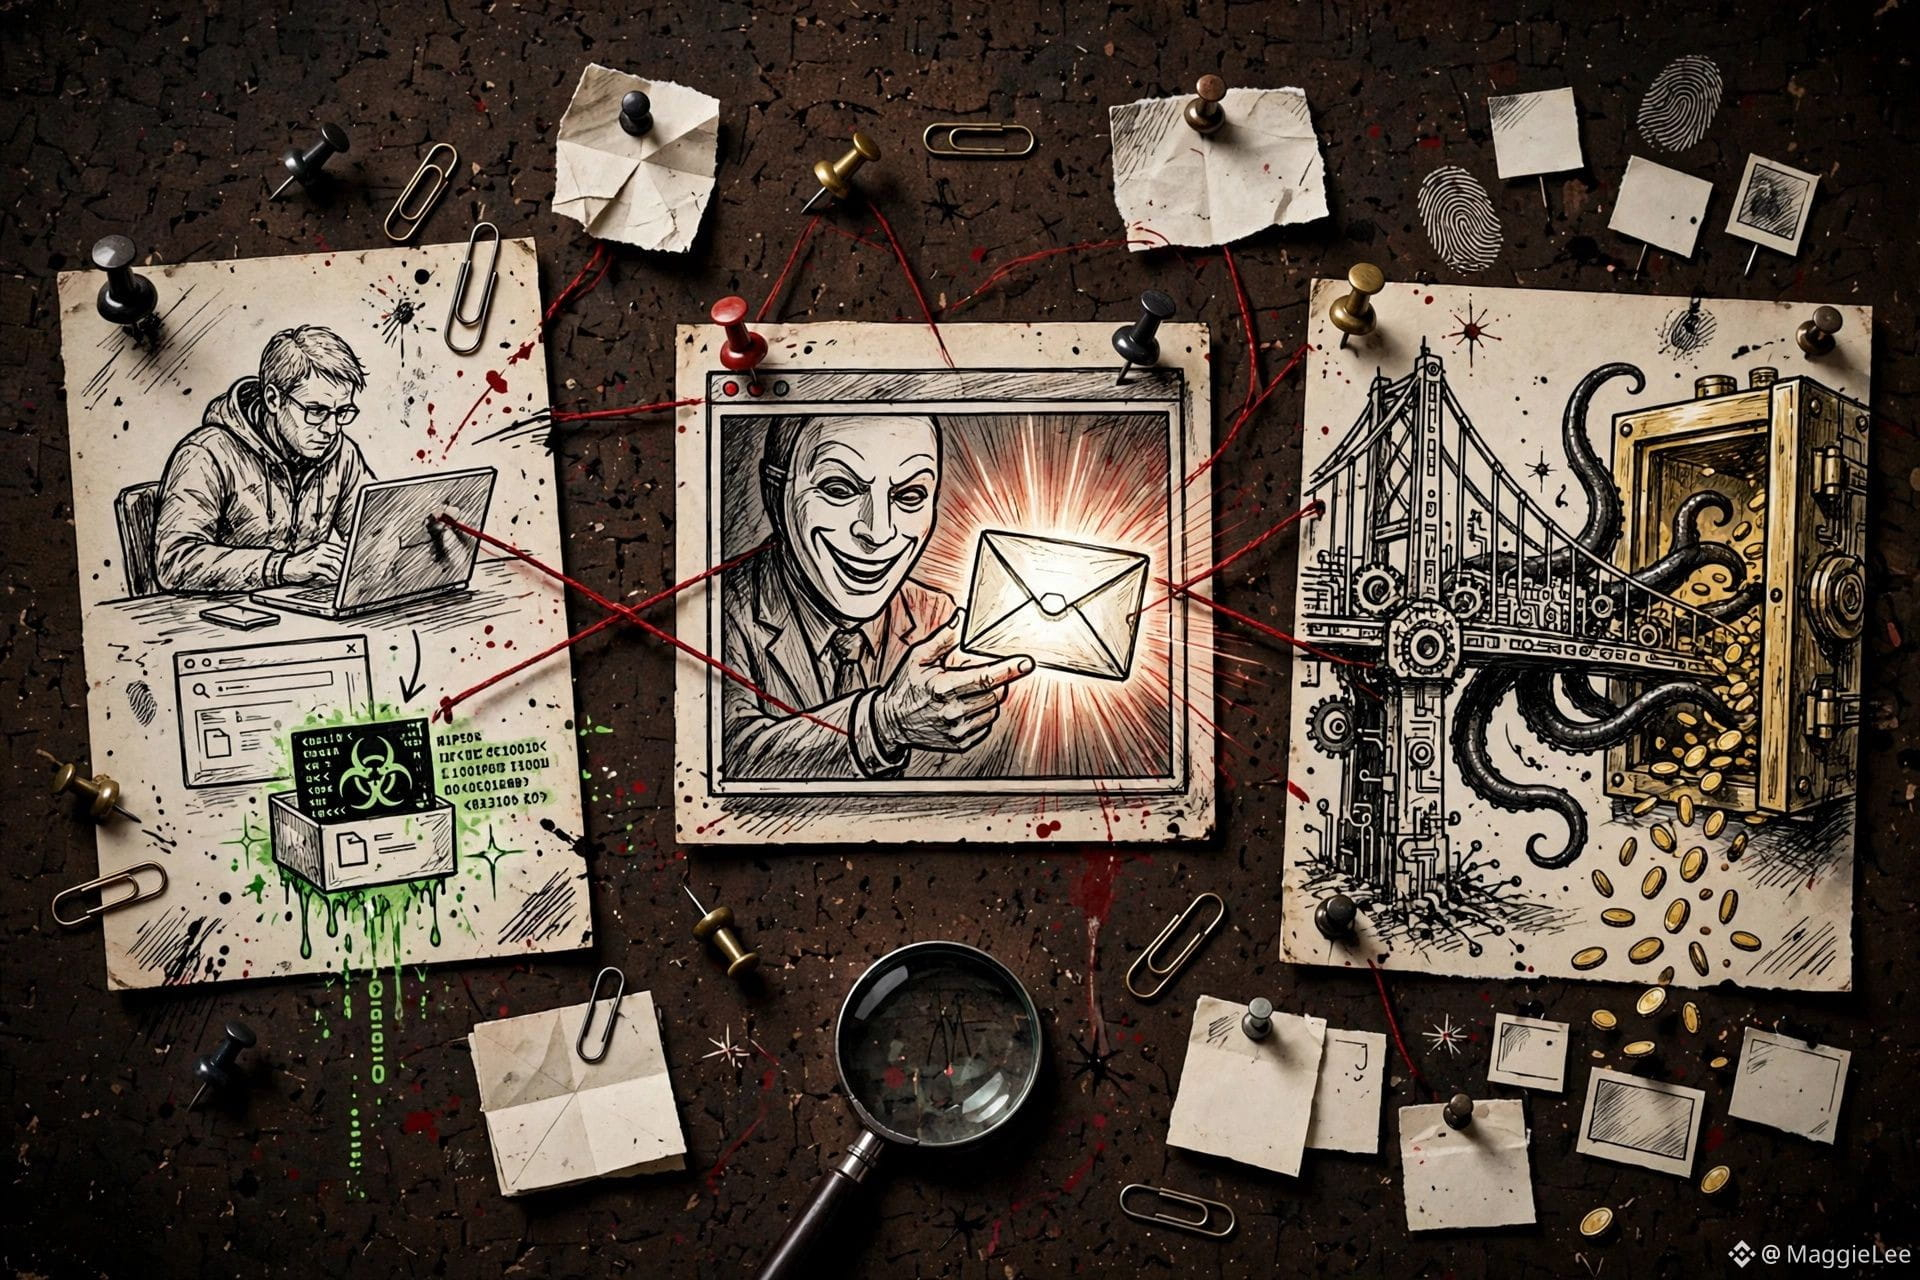
The full “play-by-play” of the $6.3 billion heist has finally been made public: it wasn’t an insider recruited by hackers, nor a one-computer mistake—it was a five-month infiltration, carefully planned step by step.
Binance released its incident review yesterday, reconstructing the full attack chain behind the largest crypto theft in history, on October 29:
Step one: June. A DevOps engineer on the wallet team searched for AI coding tools and downloaded a Homebrew installer poisoned through a malicious Google ad—the computer was compromised. Binance’s security team detected it at the time and replaced the device, but missed the second wave: the hackers deleted the legitimate pyenv executable, replaced it with a malicious version, and planted a backdoor. Endpoint protection software didn’t raise an alert.
Step two: September. A second engineer was lured in by a “fake interview” on a recruitment platform. First came a live video interview, and HR even shared a personal social media account with photos to build trust. The second round was with the “CEO of a company that didn’t exist.” Finally, they sent over a “coding assignment”—running it deployed a zero-day Trojan. Over the course of several months, the hackers gained access to multiple engineers’ accounts.
Step three: October 20. Using the second engineer’s computer and routing through an internal Binance AI tool, the hackers moved laterally into the machines of the first engineer and a third wallet engineer. From 17:15 to 19:56 on October 29, they logged into the third engineer’s computer, deployed containers, and ran malicious scripts. The outflow of $6.34 billion in assets began.
The report’s most thought-provoking explanation is this: Why couldn’t Binance stop the theft for nearly two hours after the first abnormal transfer? Because the hot wallet used multi-party computation (MPC)—there was no single private key that could “undo with one click” the malicious EIP-7702 authorization. A security design built to “eliminate single points of failure” became precisely the slowest link in the emergency response. For the first time, the trade-off between security and speed of loss containment came at such a high price.
The numbers: Around $2.85 billion has been frozen or blocked; 98% of affected assets have been replenished from company reserves, and users will bear no losses. He Yi has denied the “insider” theory, while Teng admitted on CNBC: “This shouldn't have happened. We take full responsibility.”
But don’t let “98% replenished” distract you. Binance can afford to make users whole because it’s Binance. An attack of the same scale hitting any small or mid-sized exchange would mean total wipeout—there’d be no 98% to replenish. The real lesson from this case isn’t “Binance is very secure”; it’s “only Binance can afford this tuition.”
One more thing: Binance says it has blocked 57 suspected North Korea-linked cyber threats this year. The FBI attributes the $6.3 billion heist to TraderTraitor, but the attack methods—fake interviews, poisoned development tools, and compromised AI tools—are all things developers use every day. The attack surface has changed; our defenses haven’t caught up.
Personal research; not investment advice.
$BNB $BTC
#币安 #黑客攻击 #网络安全 #ExchangeSecurity
Binance released its incident review yesterday, reconstructing the full attack chain behind the largest crypto theft in history, on October 29:
Step one: June. A DevOps engineer on the wallet team searched for AI coding tools and downloaded a Homebrew installer poisoned through a malicious Google ad—the computer was compromised. Binance’s security team detected it at the time and replaced the device, but missed the second wave: the hackers deleted the legitimate pyenv executable, replaced it with a malicious version, and planted a backdoor. Endpoint protection software didn’t raise an alert.
Step two: September. A second engineer was lured in by a “fake interview” on a recruitment platform. First came a live video interview, and HR even shared a personal social media account with photos to build trust. The second round was with the “CEO of a company that didn’t exist.” Finally, they sent over a “coding assignment”—running it deployed a zero-day Trojan. Over the course of several months, the hackers gained access to multiple engineers’ accounts.
Step three: October 20. Using the second engineer’s computer and routing through an internal Binance AI tool, the hackers moved laterally into the machines of the first engineer and a third wallet engineer. From 17:15 to 19:56 on October 29, they logged into the third engineer’s computer, deployed containers, and ran malicious scripts. The outflow of $6.34 billion in assets began.
The report’s most thought-provoking explanation is this: Why couldn’t Binance stop the theft for nearly two hours after the first abnormal transfer? Because the hot wallet used multi-party computation (MPC)—there was no single private key that could “undo with one click” the malicious EIP-7702 authorization. A security design built to “eliminate single points of failure” became precisely the slowest link in the emergency response. For the first time, the trade-off between security and speed of loss containment came at such a high price.
The numbers: Around $2.85 billion has been frozen or blocked; 98% of affected assets have been replenished from company reserves, and users will bear no losses. He Yi has denied the “insider” theory, while Teng admitted on CNBC: “This shouldn't have happened. We take full responsibility.”
But don’t let “98% replenished” distract you. Binance can afford to make users whole because it’s Binance. An attack of the same scale hitting any small or mid-sized exchange would mean total wipeout—there’d be no 98% to replenish. The real lesson from this case isn’t “Binance is very secure”; it’s “only Binance can afford this tuition.”
One more thing: Binance says it has blocked 57 suspected North Korea-linked cyber threats this year. The FBI attributes the $6.3 billion heist to TraderTraitor, but the attack methods—fake interviews, poisoned development tools, and compromised AI tools—are all things developers use every day. The attack surface has changed; our defenses haven’t caught up.
Personal research; not investment advice.
$BNB $BTC
#币安 #黑客攻击 #网络安全 #ExchangeSecurity