🔐 Binance Hack: How Fake Job Interviews Became a Security Risk
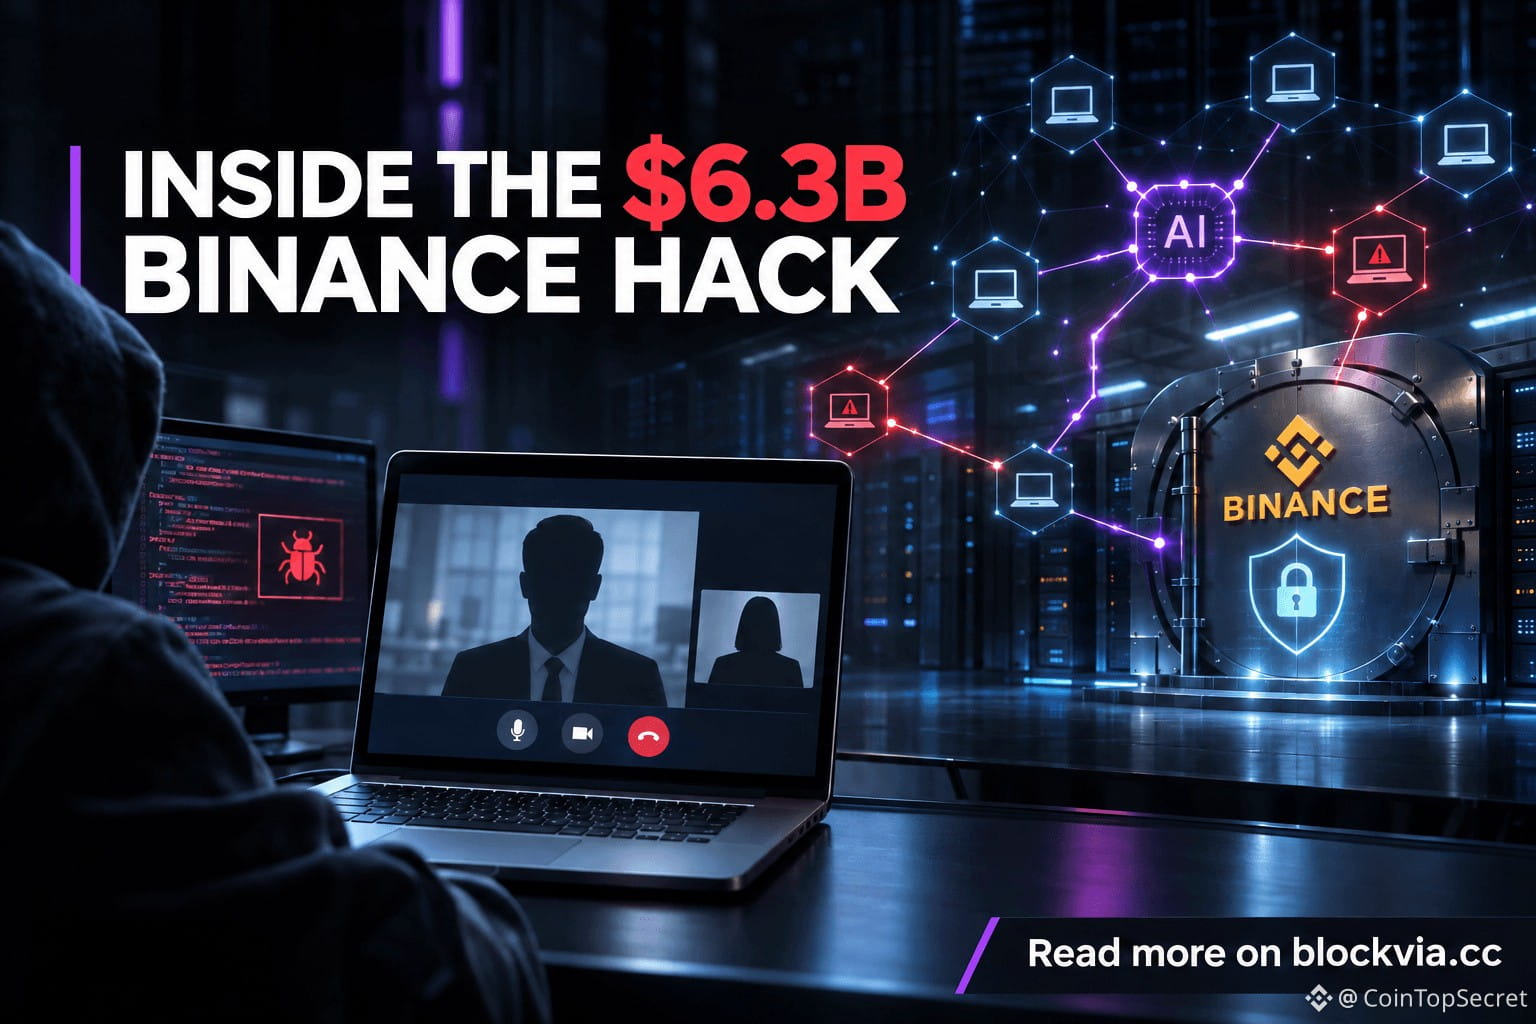
Binance says attackers used fake recruitment interviews, malicious software and a compromised internal AI tool as part of a reported $6.3 billion cryptocurrency theft.
The incident demonstrates how social engineering and compromised employee devices can expose sensitive wallet infrastructure.
📊 Key takeaways:
• Fake recruitment processes can become malware delivery channels.
• Compromised internal tools can expand attackers' access.
• Wallet security depends on strong access controls and incident response.
• AI integrations require security reviews and permission restrictions.
Binance has reported replenishing 98% of impacted token assets. This is a company-reported recovery figure, not an independent audit.
The investigation and asset recovery efforts remain important developments to follow.
👉 Full story: blockvia.cc
#Binance #CryptoSecurity #Cybersecurity $BNB
Binance says attackers used fake recruitment interviews, malicious software and a compromised internal AI tool as part of a reported $6.3 billion cryptocurrency theft.
The incident demonstrates how social engineering and compromised employee devices can expose sensitive wallet infrastructure.
📊 Key takeaways:
• Fake recruitment processes can become malware delivery channels.
• Compromised internal tools can expand attackers' access.
• Wallet security depends on strong access controls and incident response.
• AI integrations require security reviews and permission restrictions.
Binance has reported replenishing 98% of impacted token assets. This is a company-reported recovery figure, not an independent audit.
The investigation and asset recovery efforts remain important developments to follow.
👉 Full story: blockvia.cc
#Binance #CryptoSecurity #Cybersecurity $BNB