Binance’s 10/29 incident report is out: Did a $6.3 billion breach start with a “job interview”?
At 22:33 Beijing time on November 3, Binance posted a preliminary report on the 10/29 security incident on its official X account. The biggest surprise wasn’t the amount—it was how it started.
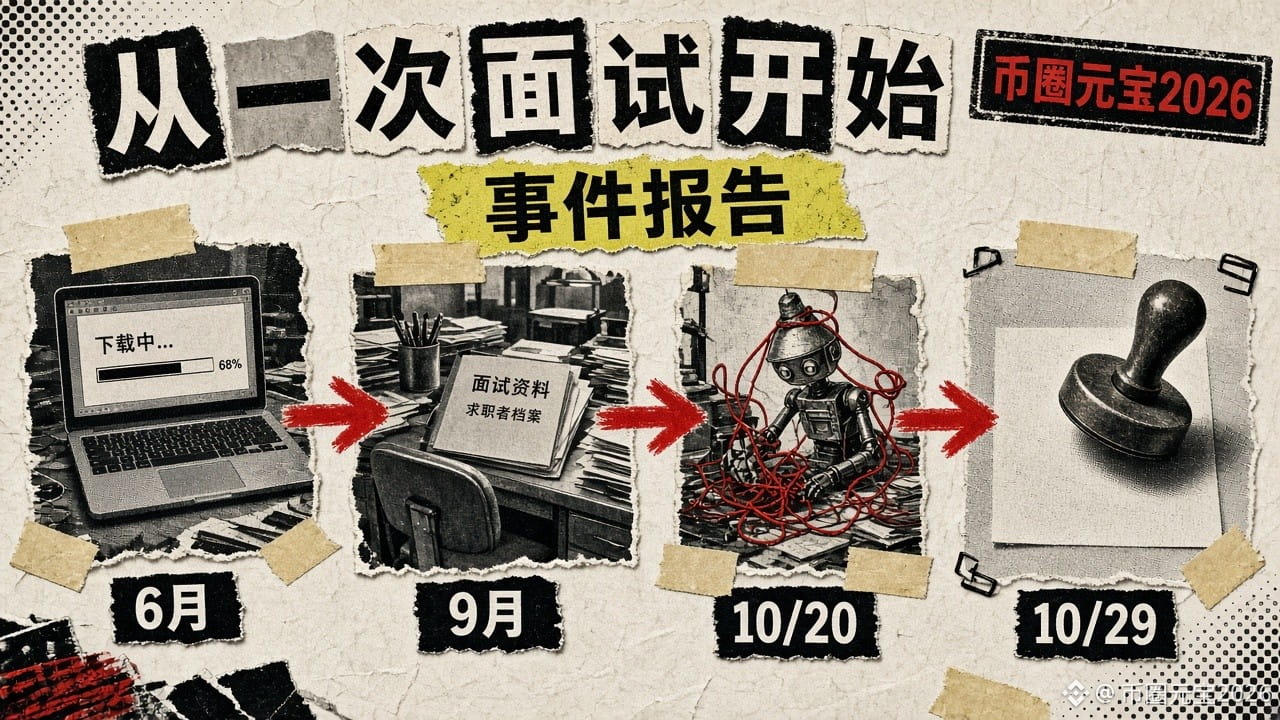
According to the report, the timeline was roughly as follows:
1. June: Engineer A, who worked on wallet operations, wanted to install a popular AI coding tool. They found and downloaded a tampered Homebrew installer through a search engine. The security team detected unusual activity, replaced the device, and rotated credentials, but A’s and their teammates’ identities had already been exposed to the attackers.
2. September: Engineer B was approached for an interview on a legitimate job platform by someone impersonating a “project director.” The first interview was by video, and the other person used private photos and videos from B’s social media account to build trust. The second round took place in a messaging app, and B was eventually asked to download an “assignment” code repository to their work computer. The code started running during installation.
3. October 20: Using B’s compromised computer, the attackers exploited an internal AI tool to gain further control of the computers belonging to A and another engineer, C. They also discovered a container deployment access token on A’s computer.
4. October 29: The attackers logged into C’s computer, used credentials stolen from A to deploy containers and trigger malicious scripts, then bypassed the normal withdrawal process by calling the wallet signing service to transfer assets.
The report’s figures: approximately $6.34 billion in assets were affected, and about $2.85 billion was frozen or intercepted. As of October 31, 98% of the affected tokens had been replenished and can be verified on the Proof of Reserves page. The report also says Binance stopped 57 suspected North Korea-linked attacks in 2026, and that the FBI’s latest information points to North Korea.
A few things worth remembering:
· The hackers didn’t try to break into the “vault” first. They targeted people: a search result, an interview assignment.
· Replacing a computer and changing a password doesn’t mean the attackers have forgotten who you are.
· The more convenient internal tools are, the more convenient they are for attackers to use as a stepping stone.
Here’s the unsettling part: For a system worth billions, the way in might be as simple as, “Please download this assignment and run it.”
Have you ever received an “interview assignment” from a company you didn’t know?
#币安 #安全 #网络安全 $BNB
At 22:33 Beijing time on November 3, Binance posted a preliminary report on the 10/29 security incident on its official X account. The biggest surprise wasn’t the amount—it was how it started.
According to the report, the timeline was roughly as follows:
1. June: Engineer A, who worked on wallet operations, wanted to install a popular AI coding tool. They found and downloaded a tampered Homebrew installer through a search engine. The security team detected unusual activity, replaced the device, and rotated credentials, but A’s and their teammates’ identities had already been exposed to the attackers.
2. September: Engineer B was approached for an interview on a legitimate job platform by someone impersonating a “project director.” The first interview was by video, and the other person used private photos and videos from B’s social media account to build trust. The second round took place in a messaging app, and B was eventually asked to download an “assignment” code repository to their work computer. The code started running during installation.
3. October 20: Using B’s compromised computer, the attackers exploited an internal AI tool to gain further control of the computers belonging to A and another engineer, C. They also discovered a container deployment access token on A’s computer.
4. October 29: The attackers logged into C’s computer, used credentials stolen from A to deploy containers and trigger malicious scripts, then bypassed the normal withdrawal process by calling the wallet signing service to transfer assets.
The report’s figures: approximately $6.34 billion in assets were affected, and about $2.85 billion was frozen or intercepted. As of October 31, 98% of the affected tokens had been replenished and can be verified on the Proof of Reserves page. The report also says Binance stopped 57 suspected North Korea-linked attacks in 2026, and that the FBI’s latest information points to North Korea.
A few things worth remembering:
· The hackers didn’t try to break into the “vault” first. They targeted people: a search result, an interview assignment.
· Replacing a computer and changing a password doesn’t mean the attackers have forgotten who you are.
· The more convenient internal tools are, the more convenient they are for attackers to use as a stepping stone.
Here’s the unsettling part: For a system worth billions, the way in might be as simple as, “Please download this assignment and run it.”
Have you ever received an “interview assignment” from a company you didn’t know?
#币安 #安全 #网络安全 $BNB