AI agents have infiltrated project documentation backends on a large scale for the first time.
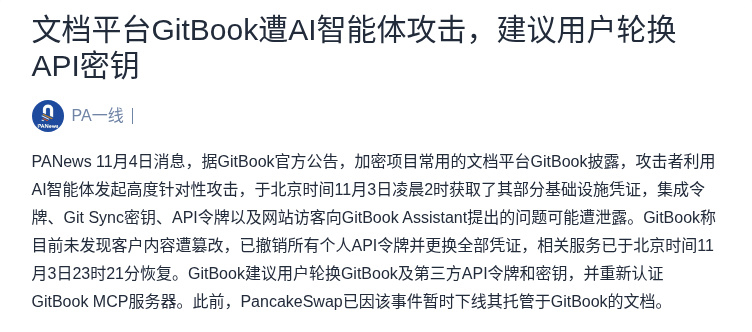
According to PANews on November 4, GitBook announced that attackers used AI agents to launch highly targeted attacks, obtaining some infrastructure credentials at 2:00 a.m. Beijing time on November 3. Integration tokens, Git Sync keys, API tokens, and questions that website visitors asked GitBook Assistant may have been exposed.
GitBook said it found no evidence that customer content had been altered. It has revoked all personal API tokens and replaced all credentials. The affected services were restored at 11:21 p.m. Beijing time on November 3. GitBook advised users to rotate their GitBook and third-party API tokens and keys, and to reauthenticate their GitBook MCP servers. Earlier, PancakeSwap temporarily took down its documentation hosted on GitBook because of the incident.
Two scenarios to watch: first, project teams complete token rotation and access reviews, and check GitHub repositories, CI/CD pipelines, and third-party services for old keys; second, a project actually suffers a funds or code-related incident due to leaked credentials. Which part concerns you more: documentation permissions or automation workflows?
Source: PANews
Image 1: GitBook hit by an AI agent attack, users advised to rotate API keys · Screenshot of the source page
Image source: https://www.panewslab.com/zh/articles/01a1a271-1594-7052-9427-1c932a0acedb
According to PANews on November 4, GitBook announced that attackers used AI agents to launch highly targeted attacks, obtaining some infrastructure credentials at 2:00 a.m. Beijing time on November 3. Integration tokens, Git Sync keys, API tokens, and questions that website visitors asked GitBook Assistant may have been exposed.
GitBook said it found no evidence that customer content had been altered. It has revoked all personal API tokens and replaced all credentials. The affected services were restored at 11:21 p.m. Beijing time on November 3. GitBook advised users to rotate their GitBook and third-party API tokens and keys, and to reauthenticate their GitBook MCP servers. Earlier, PancakeSwap temporarily took down its documentation hosted on GitBook because of the incident.
Two scenarios to watch: first, project teams complete token rotation and access reviews, and check GitHub repositories, CI/CD pipelines, and third-party services for old keys; second, a project actually suffers a funds or code-related incident due to leaked credentials. Which part concerns you more: documentation permissions or automation workflows?
Source: PANews
Image 1: GitBook hit by an AI agent attack, users advised to rotate API keys · Screenshot of the source page
Image source: https://www.panewslab.com/zh/articles/01a1a271-1594-7052-9427-1c932a0acedb