Honestly, the first thing that came to my mind when I saw the Binance news was how quickly things can change in crypto. One day, people are trading as usual, talking about the next big opportunity, and celebrating the growth of the market. Then something serious happens, and suddenly everyone starts asking the same question: how safe is my money? That is what makes this situation so concerning to me. It is not just about a huge amount of cryptocurrency being stolen. It is about the trust people place in the companies they depend on every day.
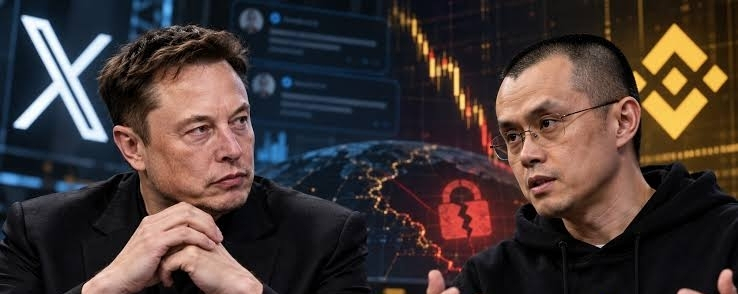
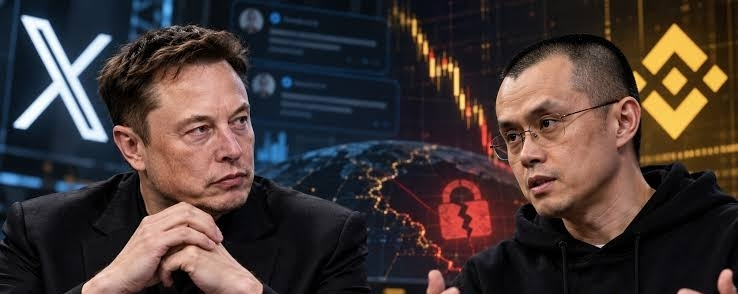
The reported $6.3 billion Binance incident is the kind of event that forces the entire industry to stop and pay attention. According to Reuters and blockchain analytics firm Elliptic, approximately $6.43 billion in crypto assets was stolen on October 29, 2026, making it larger than the major crypto thefts previously recorded. The attack reportedly happened across multiple blockchains, with a significant portion of the funds moving out within a very short period. The speed of the incident is especially disturbing because it shows how quickly a technical weakness can turn into a financial disaster. <Cite refs={["turn370446news36","turn370446search2"]}/>
What makes this even more serious is that Binance is not some small exchange that appeared yesterday. It is one of the biggest names in the crypto market, serving traders who depend on its platform for buying, selling, transferring, and managing digital assets. People use major exchanges because they want convenience and access to liquid markets. They do not want to worry about every technical detail behind the service. Most users simply expect the platform to work when they need it.
That expectation is understandable, but this incident is a reminder that size alone cannot guarantee security. A company can have enormous resources, experienced employees, and advanced technology and still face a serious vulnerability. Sometimes the problem is not a weakness in the blockchain itself. It can be a problem with the systems used to approve transactions, the software connecting different services, or the permissions given to people and devices inside an organization.
According to Binance's initial explanation, the attack involved a compromised laptop belonging to a DevOps engineer. As the investigation continued, the company disclosed that it had found additional points of compromise and that the incident was more complex than first understood. Investigators also examined how attackers exploited Ethereum's EIP-7702 account-delegation feature, which allows an ordinary wallet to operate using smart-contract code under certain conditions. The feature itself was designed to make wallets more flexible, but this incident raised difficult questions about how powerful permissions should be verified before they are approved. <Cite refs={["turn370446search5","turn370446search0"]}/>
This is the part I find especially important. People often imagine a crypto hack as someone guessing a password or stealing a private key. In reality, attacks can be much more complicated. An attacker may target an employee, exploit a software weakness, manipulate a transaction approval, or find a way around the checks designed to protect a wallet. Once the attacker gains the necessary access, the blockchain may process the resulting transactions exactly as instructed. The technology can work as designed while the process controlling it has already been compromised.
That is why security cannot be treated as a one-time project. Companies need to keep checking their systems, limiting permissions, reviewing unusual activity, and testing how their defenses respond when something goes wrong. They also need to think carefully about what happens if one security measure fails. If a single compromised device or approval can lead to billions of dollars moving out, that raises questions about whether enough independent safeguards were in place.
The attack has also been linked to North Korea's state-sponsored TraderTraitor group. Reuters reported that the FBI attributed the incident to that group, while cybersecurity researchers pointed to similarities with previous attacks associated with North Korean hackers. Such groups have been linked to major cryptocurrency thefts in the past, but understanding the exact methods used in this incident remains important. Attribution helps investigators understand who may be responsible, yet it does not replace a complete technical explanation of how the breach happened. <Cite refs={["turn370446news38","turn370446news40"]}/>
I think this is where crypto needs to be more honest with itself. The industry has become very good at attracting attention, launching new products, and convincing people that the next technological development will change everything. But security is less exciting to talk about. It rarely creates the same enthusiasm as a new token listing or a sudden price rally. Unfortunately, it is often the less exciting work that determines whether users can trust a platform in the long run.
We have seen similar questions arise during earlier market crises. When FTX collapsed in 2022, many users discovered how dangerous it could be to trust a company's reputation without fully understanding how it operated behind the scenes. The circumstances were different from the Binance incident, and the two should not be treated as identical. FTX became associated with serious failures involving the handling of customer funds, while the Binance case is being investigated as a major security breach. Still, both situations remind us that a familiar name does not remove the need for accountability.
For me, the real test of any exchange begins when something goes wrong. Does the company explain what happened as clearly as it can? Does it tell users what is known and what remains uncertain? Does it provide evidence that customer balances are protected? And does it make meaningful changes instead of simply asking everyone to move on?
These questions matter because trust is easy to build when prices are rising and everyone is making money. It becomes much harder to maintain when withdrawals are suspended and people begin worrying about access to their assets. At that point, reassuring words are not enough. Users need working services, transparent updates, and evidence that the company has taken the problem seriously.
Binance said it would cover the losses rather than leave customers to absorb the damage. Reuters reported on October 31 that the exchange had arranged resources to replace approximately 90% of the stolen assets. On November 1, Binance said it had covered or recovered approximately 95% of the affected amount and planned to resume withdrawals in phases. The company attributed the remaining shortfall to less-liquid assets that could take longer to obtain in the necessary quantities. These are important developments, but they should be understood as Binance's reported recovery and replacement figures, not proof that every stolen coin has been recovered from the attackers. <Cite refs={["turn370446news37","turn370446news38"]}/>
There is a meaningful difference between replacing stolen assets and recovering the original funds. If a company uses its own resources to restore customer balances, it may be able to meet its obligations even while the attacker still controls some of the stolen cryptocurrency. That is a significant distinction for anyone trying to understand what recovery actually means. The customers' financial position, the exchange's financial position, and the investigation into the stolen assets are related, but they are not the same thing.
Another part of the story that deserves attention is the response from other companies in the industry. Blockchain investigators have traced the movement of stolen funds, while stablecoin issuers and other partners have worked to freeze certain assets. Elliptic reported that it had verified approximately $2.84 billion in frozen funds in its October 30 analysis, with additional tracking continuing as the assets moved between wallets and networks. The exact figures can change as investigators identify more addresses and companies take further action. <Cite refs={["turn370446search2","turn370446search1"]}/>
This cooperation shows one of the useful features of public blockchains. Transactions leave records that investigators can examine, allowing them to follow the movement of funds even when the people behind the wallets are unknown. That does not mean tracing cryptocurrency is always easy or that every stolen asset can be recovered. Criminals can move funds through different networks, swap tokens, and use services that make the trail harder to follow. Still, public transaction records can provide investigators with valuable evidence.
At the same time, freezing stolen assets highlights a contradiction within crypto that I think deserves a more balanced discussion. The industry often talks about financial freedom and the ability to transfer money without relying on traditional institutions. Yet some of the most widely used digital assets depend on centralized issuers that can freeze tokens under certain circumstances.
There are understandable reasons for this. If stolen stablecoins can be frozen quickly, investigators may be able to prevent criminals from spending or moving part of the money. But this also means that users do not have the same level of control over every cryptocurrency. Bitcoin and ether do not have a central issuer with the same authority to freeze individual balances, while some centralized stablecoins do. Each model has different advantages and limitations, and people should understand those differences before deciding where to keep their money.
I also think this incident highlights a problem with the way many people measure the strength of a crypto project. Traders often focus on price, market capitalization, exchange listings, and trading volume. Those numbers can be useful, but they do not tell the whole story. A token can become popular because of a viral post, a generous reward campaign, or a sudden wave of speculation. That does not necessarily mean its underlying ecosystem is growing in a healthy way.
When I look at a project, I want to understand what people are actually doing with it. Are they using its applications because those applications solve a real problem? Are developers regularly improving the technology? Is the network being used when the market is quiet, or does activity disappear as soon as token prices begin falling? These questions may not produce an exciting headline, but they offer a better picture of whether a project has a future beyond speculation.
The same thinking applies to liquidity. Many traders assume that a large market capitalization means an asset will always be easy to buy or sell. That is not necessarily true. Market capitalization is calculated using a token's price and supply, while actual liquidity depends on how much buyers and sellers are willing to trade at different prices. A token can have a large reported valuation but still experience sharp price movements when someone tries to sell a substantial amount.
The Binance incident adds another dimension to this issue. An exchange may have enough financial resources to cover a loss but still need time to obtain particular tokens, especially if those assets trade in smaller markets. Buying a large quantity of a thinly traded token can push its price higher and make the process more difficult. This is one reason the quality of liquidity matters just as much as the headline figures surrounding a project.
Developer activity is another area I would watch closely. A project may attract a large community during a bull market, but the more important question is whether its developers continue working when attention moves elsewhere. Are they improving security? Are they fixing problems? Are they building tools that other developers can use? Are users finding new reasons to interact with the network?
Not every project with active developers will succeed, of course. Technical progress alone does not guarantee demand, and a product can be well built without finding a large audience. But when development slows, applications struggle to attract users, and activity depends almost entirely on rewards, it becomes harder to explain why an ecosystem should remain relevant over time.
Token utility deserves the same careful attention. Some tokens are needed to pay network fees or participate in particular applications. Others provide governance rights or play a role in an ecosystem's incentive structure. These uses can create demand, but only when people genuinely need or value them. A token does not automatically become useful simply because a project gives it several different functions on paper.
I have seen how easily the market can confuse popularity with lasting value. A project announces a new partnership, social media fills with excitement, and traders begin expecting the token price to rise. Sometimes that interest leads to real adoption. In other cases, the attention fades and very little changes in how the product is used. The difference usually becomes clearer with time, which is why I prefer to look at sustained activity rather than one exciting announcement.
The same applies to incentives. Rewards can be an effective way to attract early users, introduce a product, or encourage developers to experiment with a new network. There is nothing inherently wrong with that approach. The problem begins when the rewards become the main reason people participate. If users leave as soon as the incentives shrink, the project may have attracted activity without building much lasting demand.
Competition makes this even more complicated. Centralized exchanges offer convenience, customer support, and access to active markets. Decentralized exchanges allow users to trade through smart contracts and retain more direct control over their assets. Both models have important uses, but neither is completely safe. Centralized platforms can face internal security failures, while decentralized applications can suffer from coding errors, compromised interfaces, malicious token approvals, and other technical weaknesses.
I would not tell every trader to abandon centralized exchanges after one major incident. For many people, these platforms remain the easiest way to access crypto markets. Managing a personal wallet requires knowledge and responsibility, and mistakes can be difficult or impossible to reverse. Losing a recovery phrase or approving a harmful transaction can create serious problems without any customer support team able to restore access.
At the same time, keeping every asset on a single exchange may not suit every user. Some people prefer to hold long-term investments in wallets they control directly while keeping only the funds they need for trading on an exchange. Others may choose different arrangements depending on their experience, needs, and tolerance for risk. The important thing is to understand the trade-offs rather than assume that one method is perfect for everyone.
This is also why the response from other exchanges matters. Reuters reported that several crypto companies began reviewing their defenses after the Binance incident, with industry participants discussing stronger security measures and better information sharing. That is a useful development because attackers do not necessarily target only one company. If they discover a weakness in a widely used technology or exploit a common approach to transaction approvals, other platforms may face similar risks. <Cite refs={["turn370446news39"]}/>
In my view, the industry needs better ways to share warnings about active attacks, identify suspicious transactions, and coordinate responses without creating unnecessary risks for legitimate users. Companies also need to be more willing to learn from one another. Security should not be treated as a competition in which every platform keeps its problems hidden until an incident becomes impossible to ignore.
This brings me back to Elon Musk's reaction. His post saying “Everyday is Zeroday” attracted attention because it arrived while the Binance incident was unfolding. The phrase refers to the ongoing reality of cybersecurity threats, but the post itself did not establish how the attack happened or prove that a particular zero-day vulnerability was responsible. <Cite refs={["turn370446search9","turn370446search12"]}/>
I understand why the comment became part of the conversation. Musk has an enormous online audience, and his words can quickly become a story of their own. Some people saw humor in the situation, while others felt that joking during a major security crisis was insensitive. I can see why the timing bothered people, especially those who were trying to understand what the incident meant for their funds.
Still, I do not think his reaction should become the main measure of what happened. Whether someone likes Musk or dislikes him, a social media post cannot tell us whether Binance's systems are secure, whether its financial resources are sufficient, or whether the weaknesses behind the attack have been fixed. Those questions require evidence, technical investigation, and time.
Crypto has a habit of turning serious events into arguments about personalities. People choose sides, defend their favorite companies, criticize their rivals, and sometimes ignore information that does not fit their existing opinions. That kind of behavior may generate plenty of engagement, but it does not help users make better decisions. When billions of dollars are involved, understanding the facts should matter more than winning an online argument.
The longer-term question is whether incidents like this will change the way people approach digital assets. Some users may become more cautious about leaving funds on exchanges. Institutional investors may demand stronger security controls and clearer reporting. Developers may reconsider how wallet permissions and transaction approvals are designed. Exchanges may invest more in monitoring, independent testing, and systems that prevent a single failure from becoming a much larger problem.
These changes will not happen overnight, and not every promise of improvement will lead to meaningful progress. That is why I would rather judge the industry by what it actually changes than by what its executives say immediately after a crisis. Better security procedures, transparent reporting, and evidence of stronger controls would be more convincing than another round of confident statements.
The same principle applies to the wider crypto market. I want to see projects building products that people continue to use, developers who remain committed through difficult conditions, and ecosystems with enough genuine activity to support themselves beyond short-term incentives. I want to see liquidity that holds up when markets become uncertain and token designs that make sense for the products they support. None of these qualities guarantees success, but they offer more useful information than popularity alone.
What happened at Binance is a reminder that crypto is still developing as an industry. The technology offers opportunities that are difficult to ignore, but the systems surrounding it can still be vulnerable to human mistakes, technical weaknesses, and increasingly sophisticated attackers. Progress is not just about making transactions faster or launching more applications. It also means building services that people can rely on when something unexpected happens.
For now, I am watching how Binance follows through on its recovery commitments, what its investigation reveals, and whether independent evidence supports the security improvements it announces. I