Binance hack: how did they get in? Part 2 of our profile. We tested four explanations against the chain.
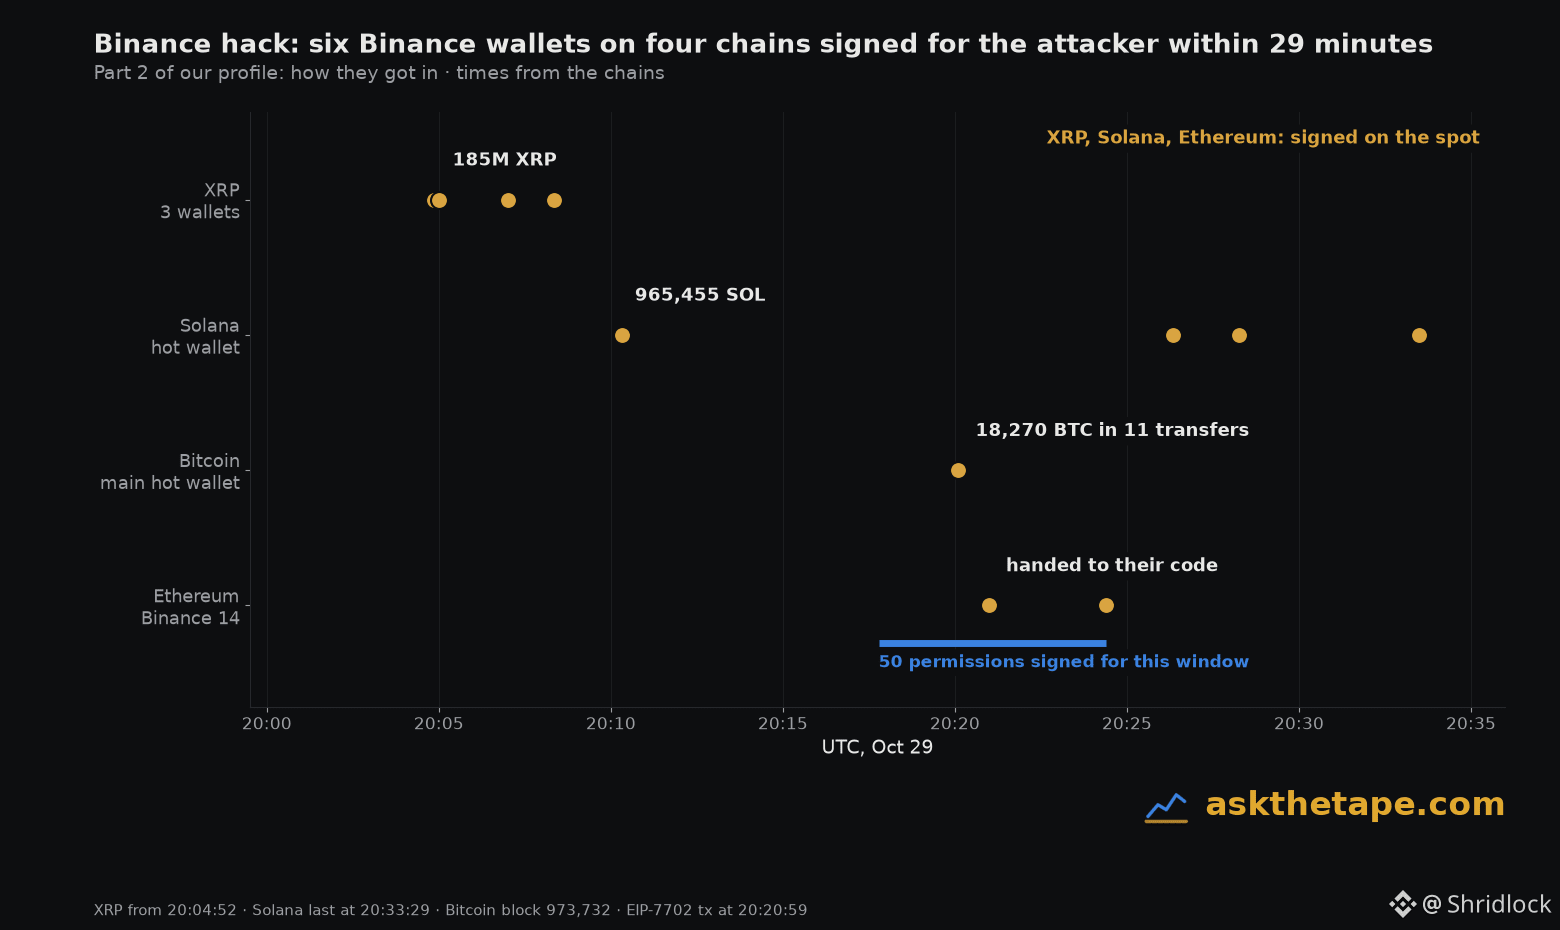
1. One stolen key? No. Six Binance wallets on four chains signed for the attacker between 20:04 and 20:33 UTC Oct 29. The three XRP wallets alone have three different keys.
2. A bug in a smart contract? No. Binance 14 is a plain wallet. Its own key signed 50 EIP-7702 permissions that handed it to the attacker's code.
3. A gap only in EIP-7702? No. Solana, XRP and Bitcoin left by plain transfers.
4. What is left: someone worked inside Binance's hot wallet system for at least 28 minutes.
- They signed on the spot. The 50 permissions start at the nonce Binance 14 had at 20:17:47 UTC, 3 minutes before use.
- Not just fake withdrawals. On Solana and XRP the stolen transfers look nothing like Binance's own.
- Not just copied keys. Bitcoin left in the format of Binance's own withdrawals, at twice the usual fee rate. Their own wallet, one step later, makes very different transactions.
They rehearsed. The attack contract was deployed at 15:59 UTC and tested on their own wallet at 16:30. Their gas came through Tornado Cash.
A break-in or an insider? The chain cannot tell. Only Binance's logs can.
1. One stolen key? No. Six Binance wallets on four chains signed for the attacker between 20:04 and 20:33 UTC Oct 29. The three XRP wallets alone have three different keys.
2. A bug in a smart contract? No. Binance 14 is a plain wallet. Its own key signed 50 EIP-7702 permissions that handed it to the attacker's code.
3. A gap only in EIP-7702? No. Solana, XRP and Bitcoin left by plain transfers.
4. What is left: someone worked inside Binance's hot wallet system for at least 28 minutes.
- They signed on the spot. The 50 permissions start at the nonce Binance 14 had at 20:17:47 UTC, 3 minutes before use.
- Not just fake withdrawals. On Solana and XRP the stolen transfers look nothing like Binance's own.
- Not just copied keys. Bitcoin left in the format of Binance's own withdrawals, at twice the usual fee rate. Their own wallet, one step later, makes very different transactions.
They rehearsed. The attack contract was deployed at 15:59 UTC and tested on their own wallet at 16:30. Their gas came through Tornado Cash.
A break-in or an insider? The chain cannot tell. Only Binance's logs can.