【OpenSky · Daily Exploration Day 24】
OpenSky’s exploration coordinates for today: “Black swans aren’t scary. What’s scary is an entire industry waking up only on the day of an incident.”
A $6.3 billion security incident. Group chats are blowing up, charts are plunging, and memes are spreading. Preliminary tracing points to an engineer’s compromised workstation and a hijacked command authorization system—not exposed private keys, but a breached “authorization channel.”
Every major shock is an industry-wide health check. This time, the report is crystal clear:
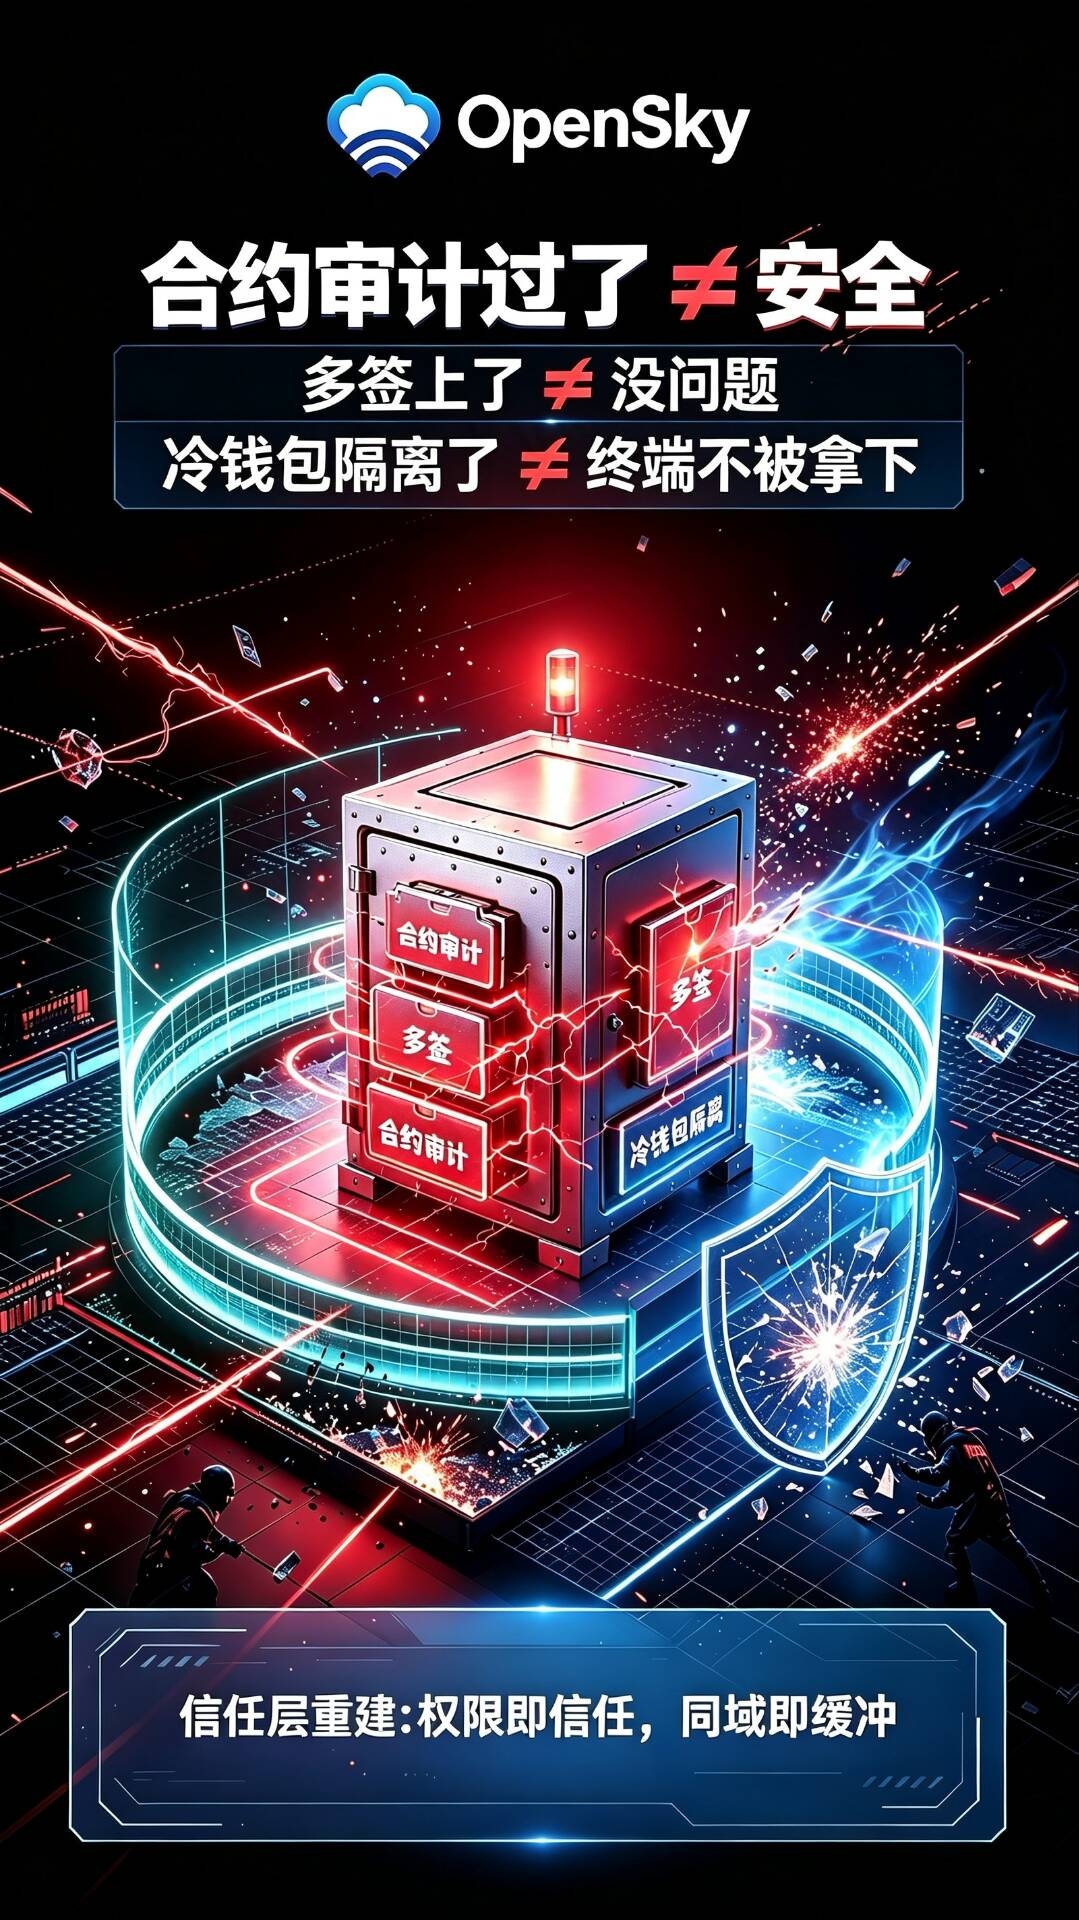
Contract audit passed ≠ infrastructure is secure
Multisig enabled ≠ no permission issues
Cold wallet isolation ≠ operations terminals being safe from compromise
Chanting “security first” ≠ having trust in the communications layer
The attack surface has shifted from “on-chain code” to “off-chain permissions”—terminals, sessions, authorizations, internal channels, and operations identities.
We build our foundation on “permissions as trust”: OpenSky safeguards communications, security safeguards permissions, and Anfu handles transfers. Any one link facing attacks alone will struggle, but coordination within the same domain can turn a single point of failure into a system-wide buffer.
The industry’s reflection this time shouldn’t stop at “Will that security firm compensate users, and how many billions were frozen?”
Real progress means:
Treating “permission governance” as a first-class citizen
Treating “communications trust” as infrastructure
We’re neither bystanders watching the drama unfold nor Monday-morning quarterbacks.
What we’re looking at is this: when the next storm hits, will our own foundation be strong enough?
OpenSky #DailyExploration #SecurityInfrastructure #PermissionsAsTrust #SAFE4.0 #ZodiacEcosystem