Another cross-chain bridge has been hit—this time, a ZK bridge.
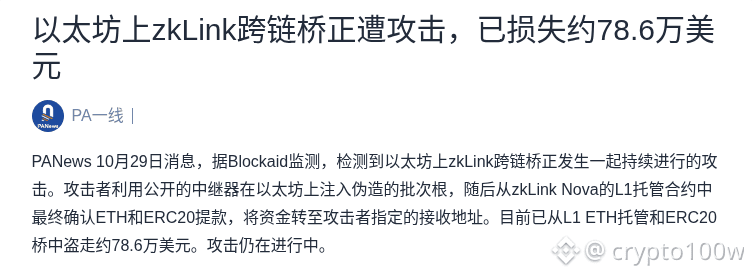
According to a report by PANews on October 29, Blockaid detected an ongoing attack on zkLink’s cross-chain bridge on Ethereum. The attacker exploited a public relayer to inject a forged batch root, then used it to confirm ETH and ERC-20 withdrawals from zkLink Nova’s L1 custody contract. Approximately $786,000 has been stolen, and the attack is still ongoing.
Observation 1: Once batch-root verification and relayer permissions are bypassed, assets held in L1 contracts are directly exposed. The complexity of ZK proofs has, ironically, become a new attack surface. Observation 2: The $786,000 loss is not large enough to shake the broader market, but this attack targets the core verification logic of a ZK bridge, so its significance matters more than the amount. This is bearish for zkLink (ZKL).
Users who have bridged assets through zkLink Nova or provided liquidity are advised to check their approvals and asset balances as soon as possible. If necessary, revoke approvals for the relevant contracts and move assets back to self-custody wallets. Do not deposit more into the bridge until the team confirms the issue has been fixed.
Are you more concerned about whether the attack is stopped in time, or about the progress of the patch and fund freeze?
Source: PANews
#ZKL
Image 1: zkLink cross-chain bridge attacked, approximately $786,000 lost · Screenshot of source page
Image source: https://www.panewslab.com/zh/articles/01a1857c-23f1-7035-8b60-e5fcd1efdefb
According to a report by PANews on October 29, Blockaid detected an ongoing attack on zkLink’s cross-chain bridge on Ethereum. The attacker exploited a public relayer to inject a forged batch root, then used it to confirm ETH and ERC-20 withdrawals from zkLink Nova’s L1 custody contract. Approximately $786,000 has been stolen, and the attack is still ongoing.
Observation 1: Once batch-root verification and relayer permissions are bypassed, assets held in L1 contracts are directly exposed. The complexity of ZK proofs has, ironically, become a new attack surface. Observation 2: The $786,000 loss is not large enough to shake the broader market, but this attack targets the core verification logic of a ZK bridge, so its significance matters more than the amount. This is bearish for zkLink (ZKL).
Users who have bridged assets through zkLink Nova or provided liquidity are advised to check their approvals and asset balances as soon as possible. If necessary, revoke approvals for the relevant contracts and move assets back to self-custody wallets. Do not deposit more into the bridge until the team confirms the issue has been fixed.
Are you more concerned about whether the attack is stopped in time, or about the progress of the patch and fund freeze?
Source: PANews
#ZKL
Image 1: zkLink cross-chain bridge attacked, approximately $786,000 lost · Screenshot of source page
Image source: https://www.panewslab.com/zh/articles/01a1857c-23f1-7035-8b60-e5fcd1efdefb