

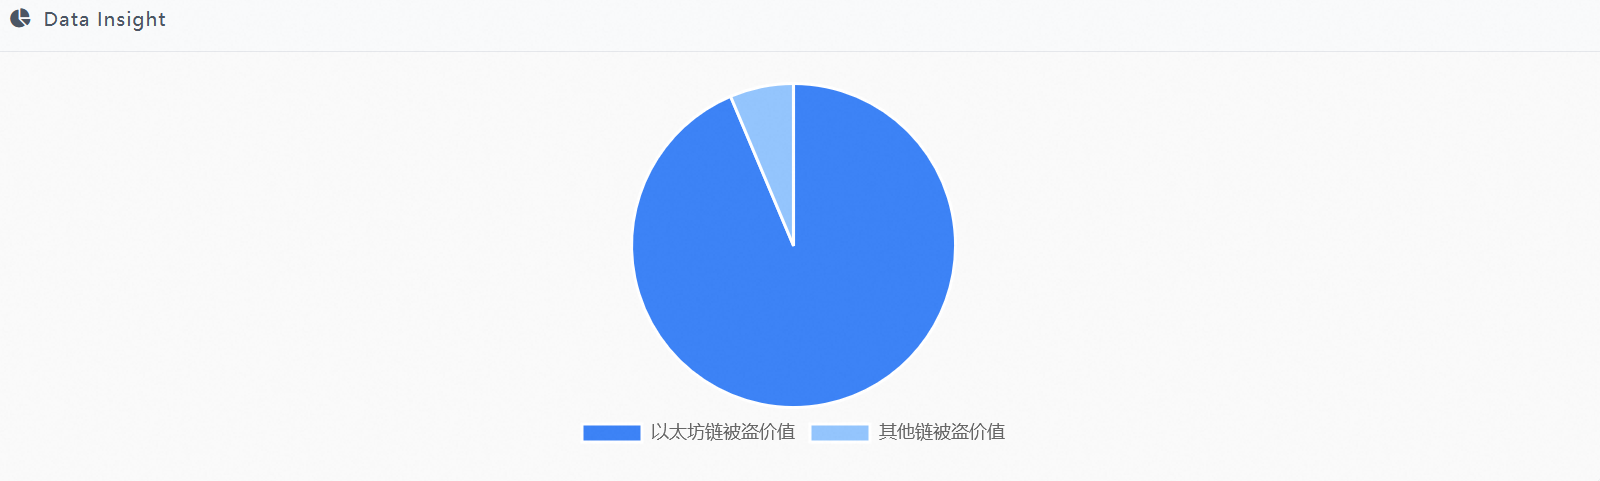
In the early hours of October 30, Binance suffered the largest hack in its history: approximately $6.3 billion in assets flowed out across eight chains within 40 minutes, with Ethereum bearing the brunt. The culprit was EIP-7702, introduced in the 2025 Pectra upgrade.
Attack path
On October 28, the attacker withdrew a small amount of funds from Tornado Cash to pay transaction fees. On the afternoon of the 29th, they deployed the final malicious contract (Solidity 0.8.28, which recognized only the attacker as its owner). From the evening of the 29th to the early hours of the 30th, they rehearsed the entire process twice using two test wallets. The final rehearsal was just 3.5 hours before the actual attack.
At 4:20:59 UTC, the attacker broadcast a transaction containing 50 EIP-7702 authorization requests, covering 50 consecutive nonces from 18914775 to 18914824. The nonce of Binance’s hot wallet was ticking forward every second, making it impossible to predict which one would be valid—so the attacker “sprayed” authorizations. During Ethereum execution, 49 invalid signatures were automatically discarded, and only the one that hit the live window took effect.
After that, the hacker no longer needed Binance’s private key. They called the contracts directly, sweeping all 64 tokens from Binance 14’s hot wallet in one go, including 167,464 ETH and 1.615 billion USDT. Twenty-four seconds later, Binance 16 used its private key to sign a routine transfer, sending 28,005.6 ETH to the same address. At 4:41, the attacker, acting as a Binance 14 administrator, instructed Binance 34 to transfer about 780 million USDC.
Where was the flaw?
The validation logic was “pass if any one nonce matches,” rather than “validate each item independently.” The authorization tuple contained only chain_id, address, and nonce—no recipient, amount, or call data—so the signing system had no way to distinguish a legitimate authorization from a malicious delegation. What’s more, once a delegation took effect, it persisted. Two hours after the incident, Shenyu was still warning: “The keys are clearly still in Binance’s hands, but that fatal authorization still hasn’t been revoked.”
The private key wasn’t lost; the signing system was manipulated
The hacker compromised a DevOps engineer’s laptop and gained access to a service container, allowing them to manipulate the signing system. HSM+MPC can ensure that private key shares aren’t extracted, but they can’t stop “the system from being instructed to sign something dangerous.”
Not the first time
In July 2025, Scam Sniffer reported an EIP-7702 phishing attack that caused losses of about $146,000. The October MORPHO theft also involved this mechanism.
When new features are rapidly deployed to mainnet but adversarial testing fails to keep up, they can become a new tool in attackers’ toolbox.