Running a node on Linux doesn’t mean you should dismiss the entire round of vulnerability alerts.
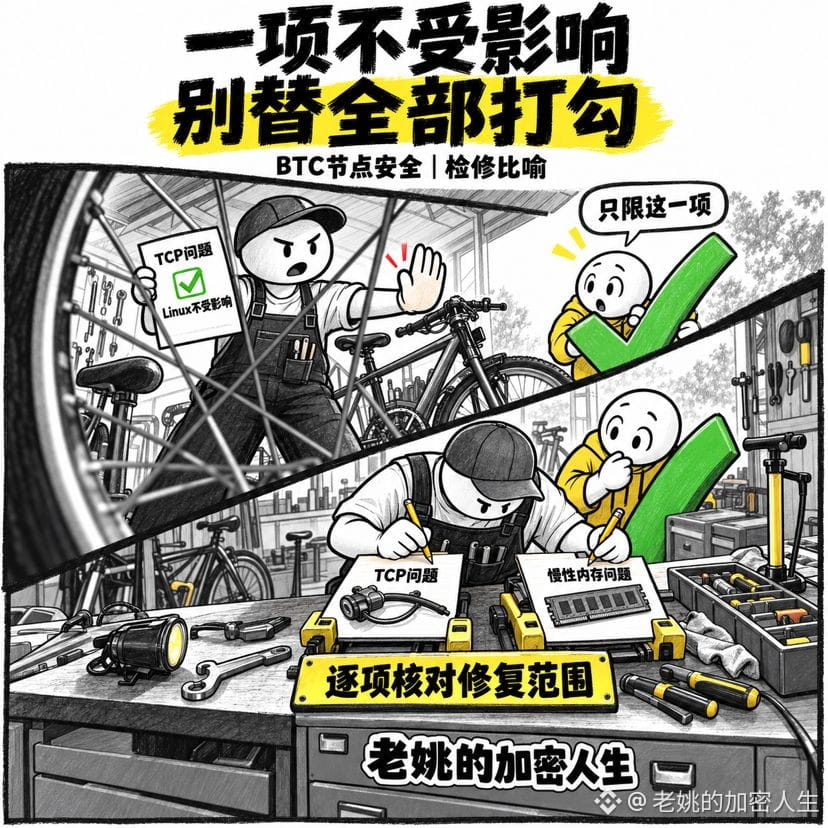
This afternoon, while following $BTC security discussions, Lao Yao checked the original Bitcoin Core announcement published on October 28: “Linux is not affected” refers specifically to the memory exhaustion issue triggered by TCP urgent data, because it involves a network processing path used by non-Linux platforms.
A separate advisory disclosed a chronic memory issue in which the queue continued to grow even after sending was paused, and listed versions 29.5, 30.4, 31.2, and 32.1 as fixes. The exemption for one operating system in the first issue cannot be applied directly to the other.
I’ll check the operating system, version in use, and scope of the fix for each specific vulnerability, rather than judging an entire node safe based on its operating system alone. Node operators should check each item against the advisory.
When you see “a certain operating system is not affected,” do you check which vulnerability that refers to?
For personal market observations only; not investment advice.#比特币Core发布32.1版本提高节点连接上限