If you use the Electrum wallet, you should update to version 4.8.3 today.
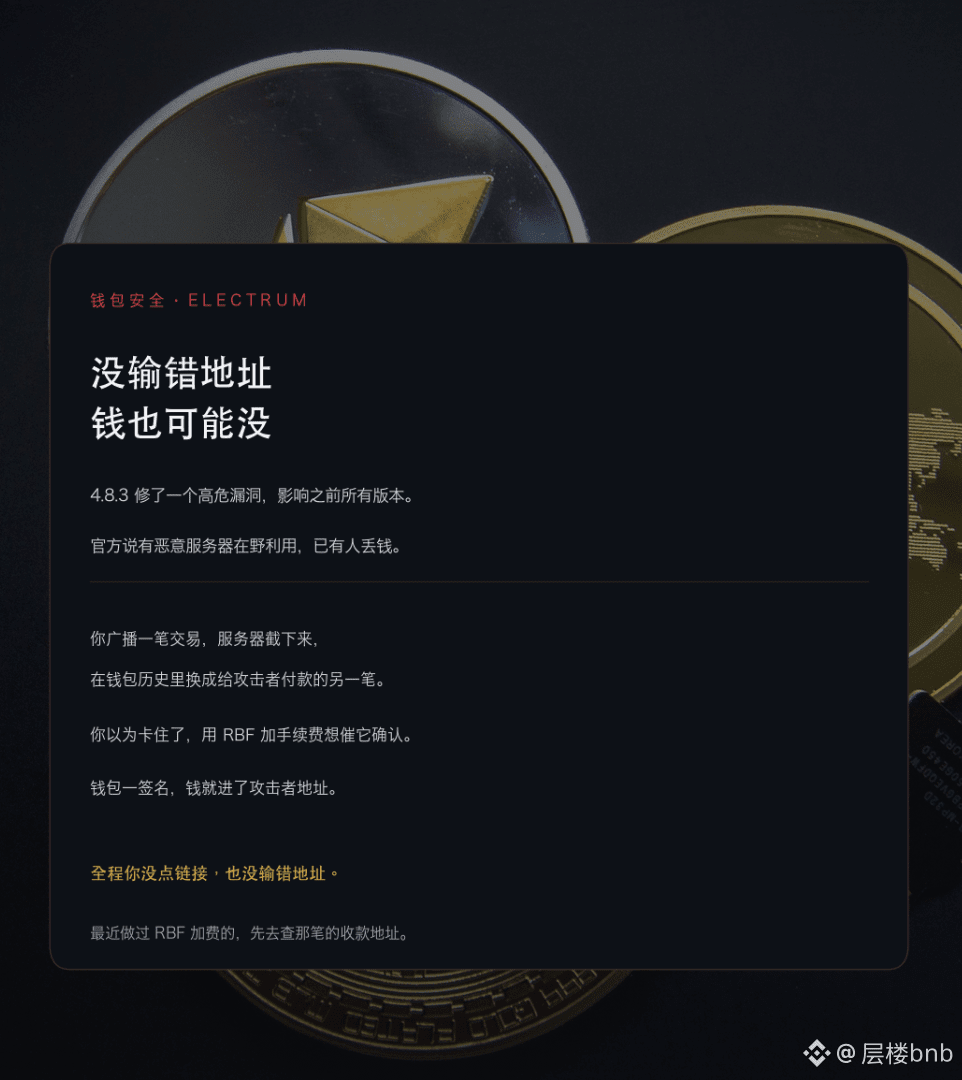
This version fixes a critical vulnerability that affects all versions before 4.8.3. Electrum's developers say malicious servers have already exploited it in the wild, and some users have lost money.
The attack is quite stealthy.
You broadcast a transaction, and a malicious server intercepts it, then replaces it in your wallet history with another transaction addressed to the attacker.
Thinking your transaction is stuck, you use RBF to increase the fee and speed up confirmation. At this point, the wallet signs the transaction, and the money goes to the attacker's address.
You never mistyped an address or clicked a link.
If you've used Electrum recently and increased the fee on a transaction using RBF, check that the recipient address is correct. Then update.#electrum修复4.8.3前版本高危漏洞 $TRUST