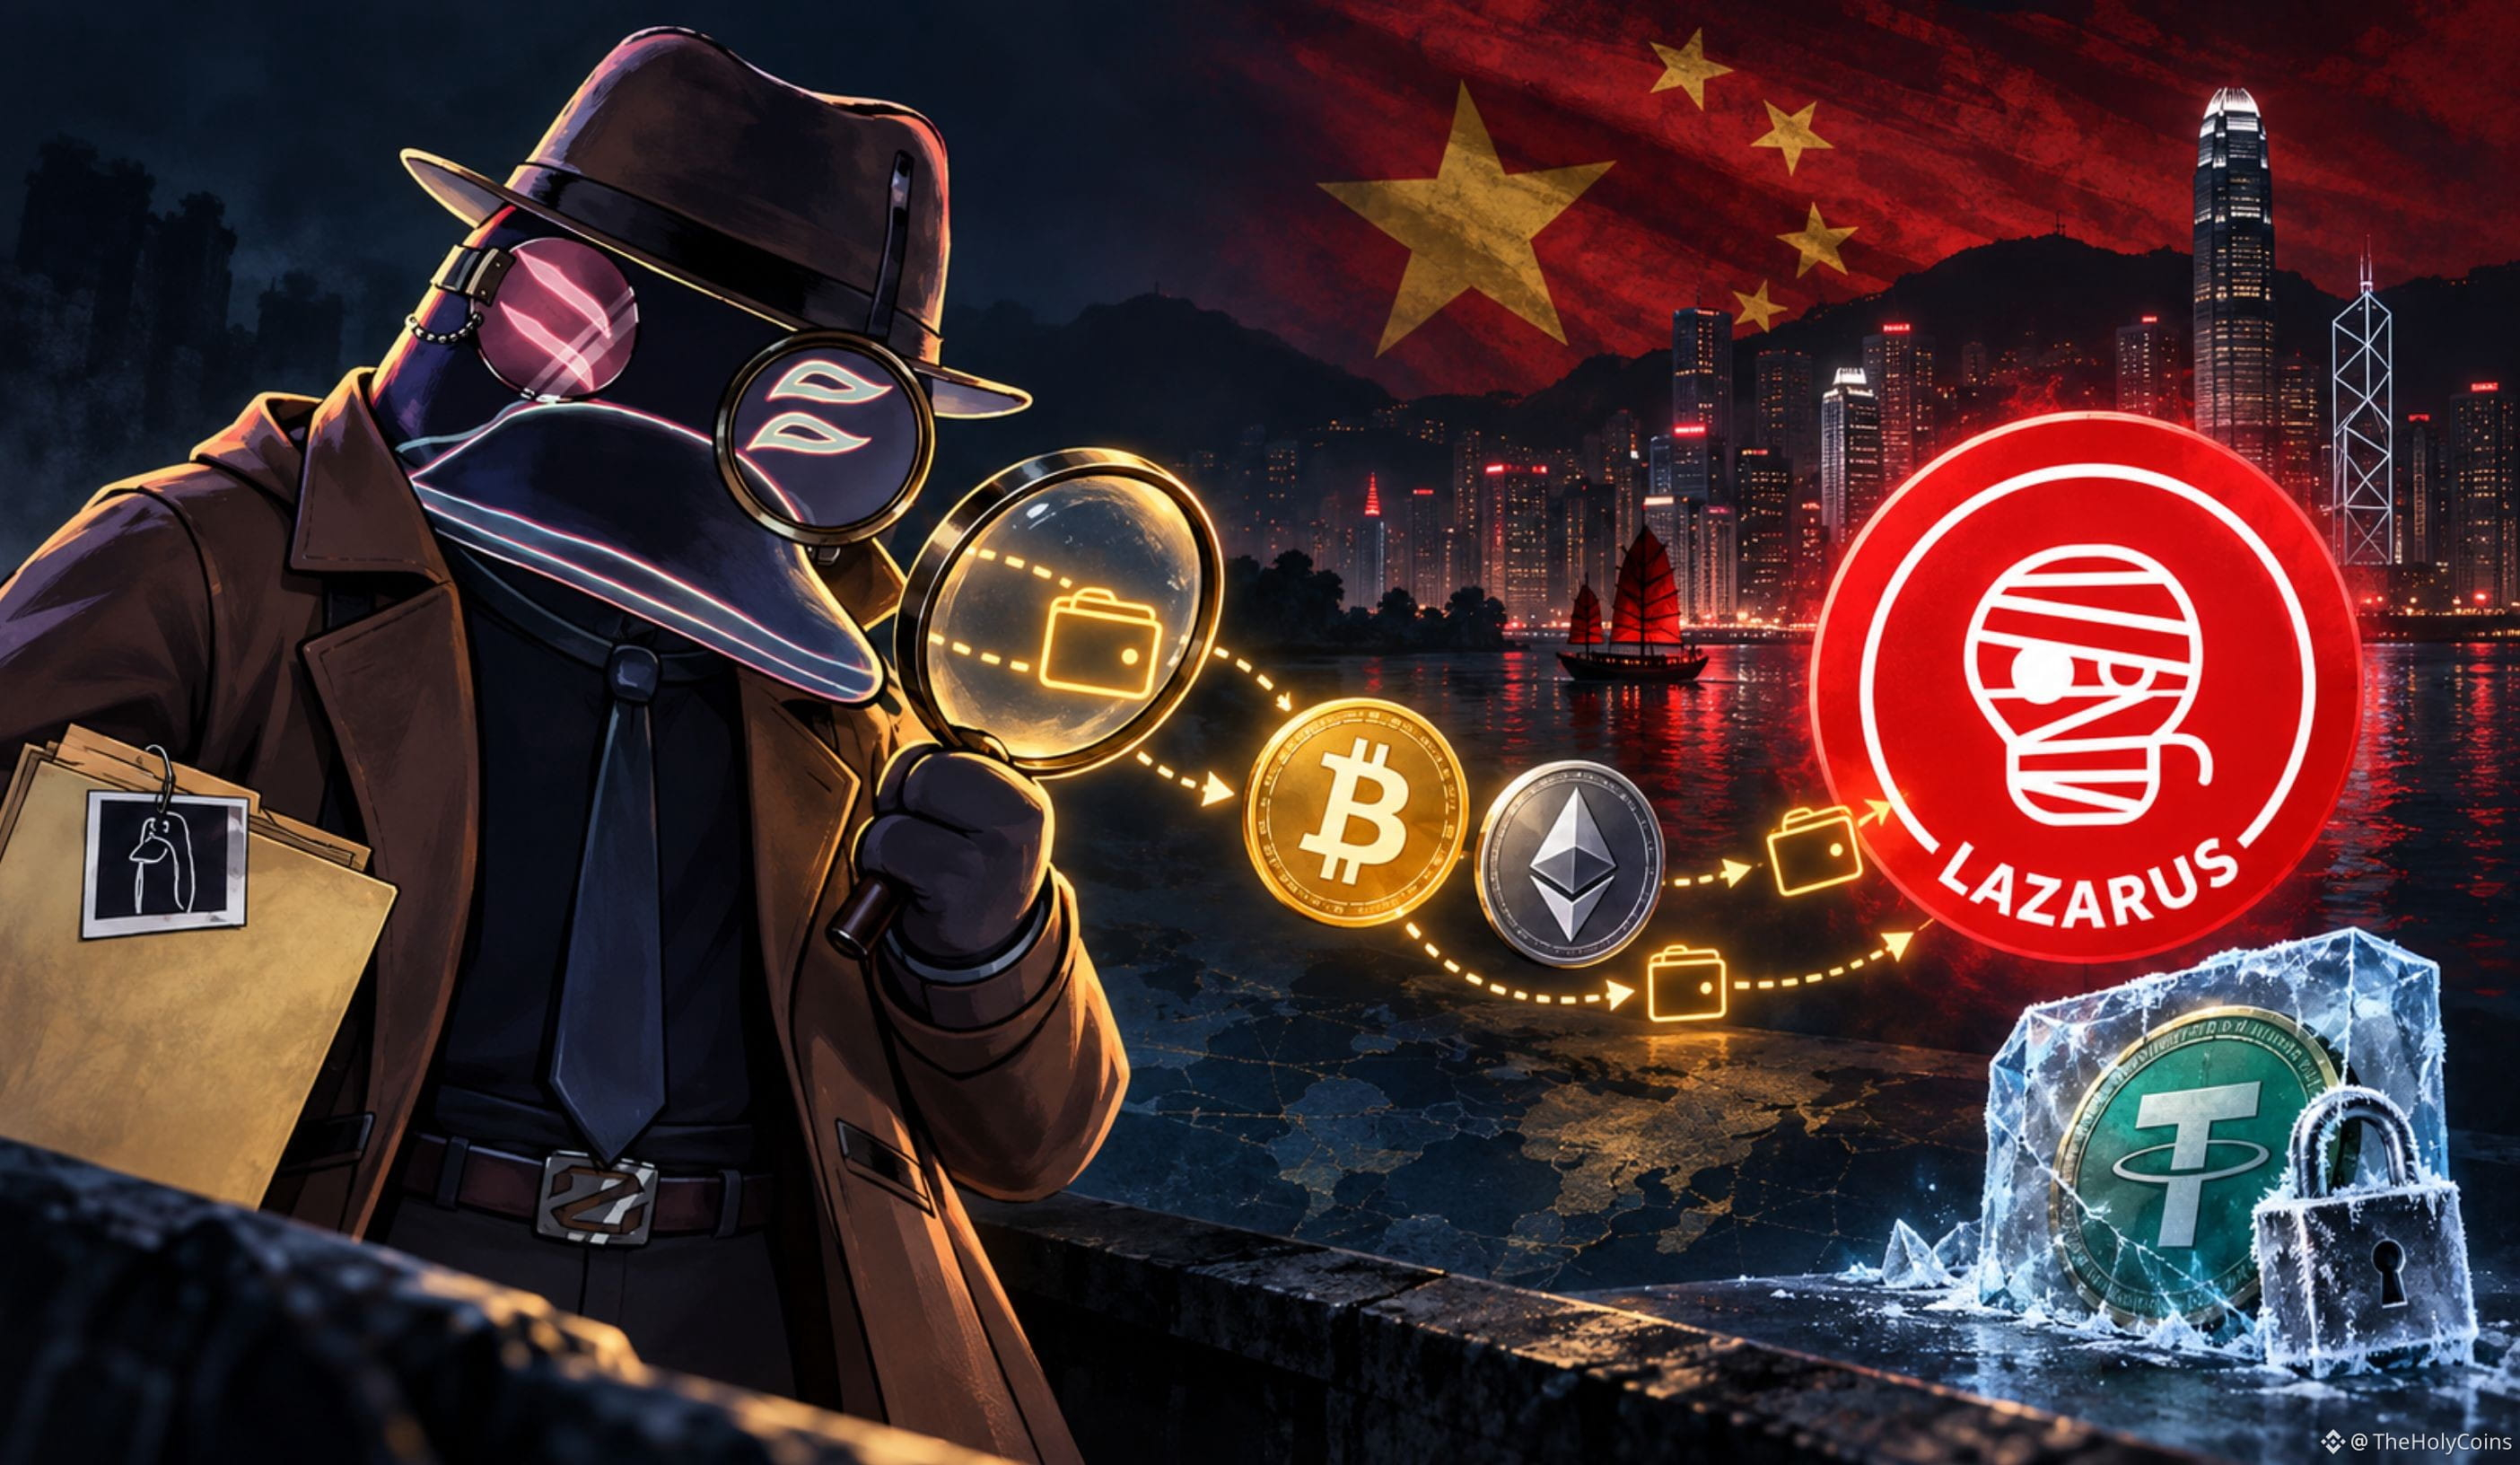
ZachXBT said on October 5 that he posed as a client to infiltrate a Chinese network accused of laundering over $1 billion in stolen crypto for Lazarus Group.
After the $1.5 billion Bybit hack in February 2025, he identified over 15 accounts seeking transfer help in public Telegram and Discord groups.
On March 6, he began trading with “Jimmy Green,” swapping Ethereum $USDC for Tron $USDT . He committed $349,700 and accepted a 5% loss per trade to build trust. Green’s address received transaction-fee funding from a Bybit-linked wallet.
Green shared planned Bybit transfers, including a Solana move observed the next day. A transfer screenshot also matched a THORChain order. Three Solana addresses enabled tracing across Bitcoin, Ethereum, Solana, and Tron. ZachXBT also identified laundering through low-activity Uniswap pools.
The conversations helped trace over $12 million in Bybit funds. Tether later froze 442,000 USDT. Further links involved 332,000 USDC stolen from Poloniex and $3 million in fraud proceeds traced to a Huione Guarantee wallet.
After the $387 million Bitget hack in September 2026, similar public requests appeared. ZachXBT linked one account to the $292 million Kelp DAO exploit.
He shared findings with investigators and law enforcement, delaying publication because of the case’s sensitivity. He says his work has helped secure over $75 million in freezes tied to North Korean incidents since 2022 and requested continued funding.
#zachxbt #investigation #CryptoNews #scam #LazarusGroup