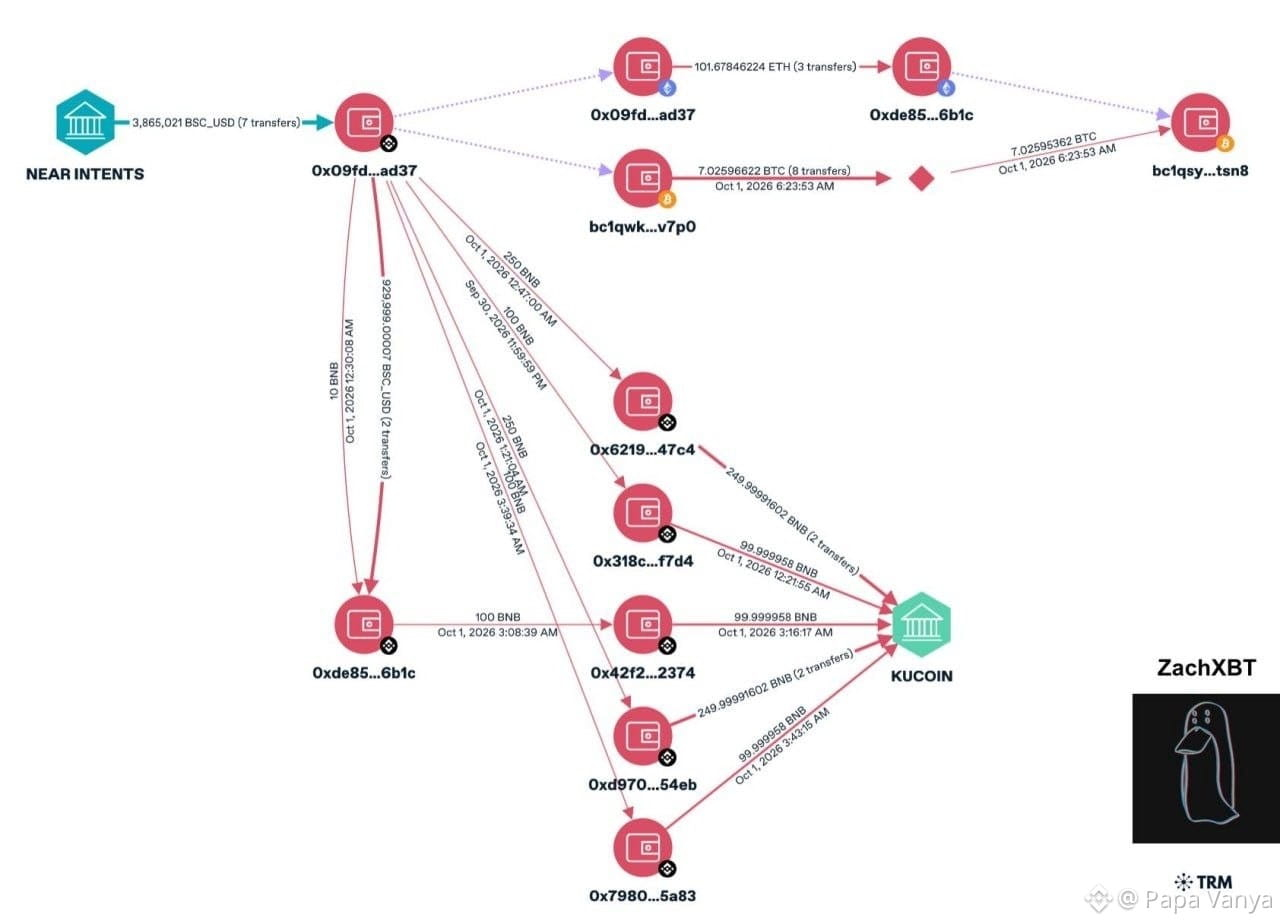
🚨 About $3.8M was stolen from NEAR Intents. The team promises compensation
Attackers exploited a bug in the interaction between the Omni input/output system and the NEAR Intents smart contract. After the issue was discovered, the service was paused.
According to the team, the vulnerability has already been fixed and user losses will be fully compensated.
The team promised to restore the core service within an hour of the announcement. At the same time, input and output on a number of networks, including BSC, Polygon, and TON, were planned to remain on hold for about 12 hours.