A single password no longer suffices to protect your cryptocurrency account.
For years, the code that arrived by text message seemed enough. It isn’t anymore. It travels over the phone carrier’s network, and that network can be hijacked without touching your phone. What does hold up is a code generated within the device itself, without going through any carrier: it can be an app or a physical key.
Think of an account with $BNB saved there. With just one key, the thief steals one thing. With a well-chosen second factor, they have to steal two—and one of them never leaves your pocket.
That’s two-factor authentication: a second lock that doesn’t share a key with the first.
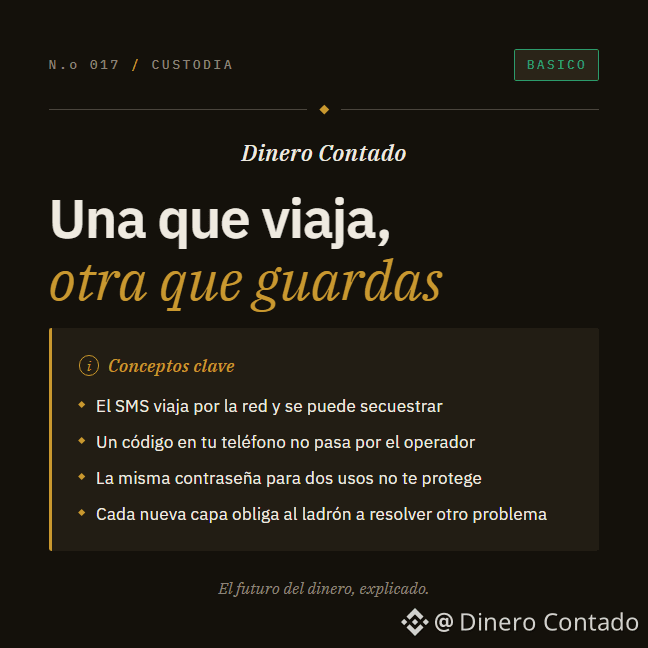
KEY CONCEPTS
- A text-message code no longer counts as a reliable second factor: it travels over a network that can be hijacked without touching your phone.
- A code generated inside the device—whether an app or a physical key—doesn’t depend on the phone carrier. That’s why it resists better.
- Using the same key for email and for the second factor isn’t double protection. It’s the same door painted twice.
- No method is invulnerable, but each different layer forces the attacker to solve a new problem, not the same one twice.
The same care you already use to store your private keys is what you should use to choose your second factor: not everything that promises to protect does so equally.
Transparency: Binance may pay us a commission if you trade after clicking an asset symbol or a price link from this publication.
#Autocustodia #SeguridadDigital #Criptomonedas #EarningsSeason #DobleFactor