#bitgethotwalletbreachtiedtothirdpartysecurityflaw
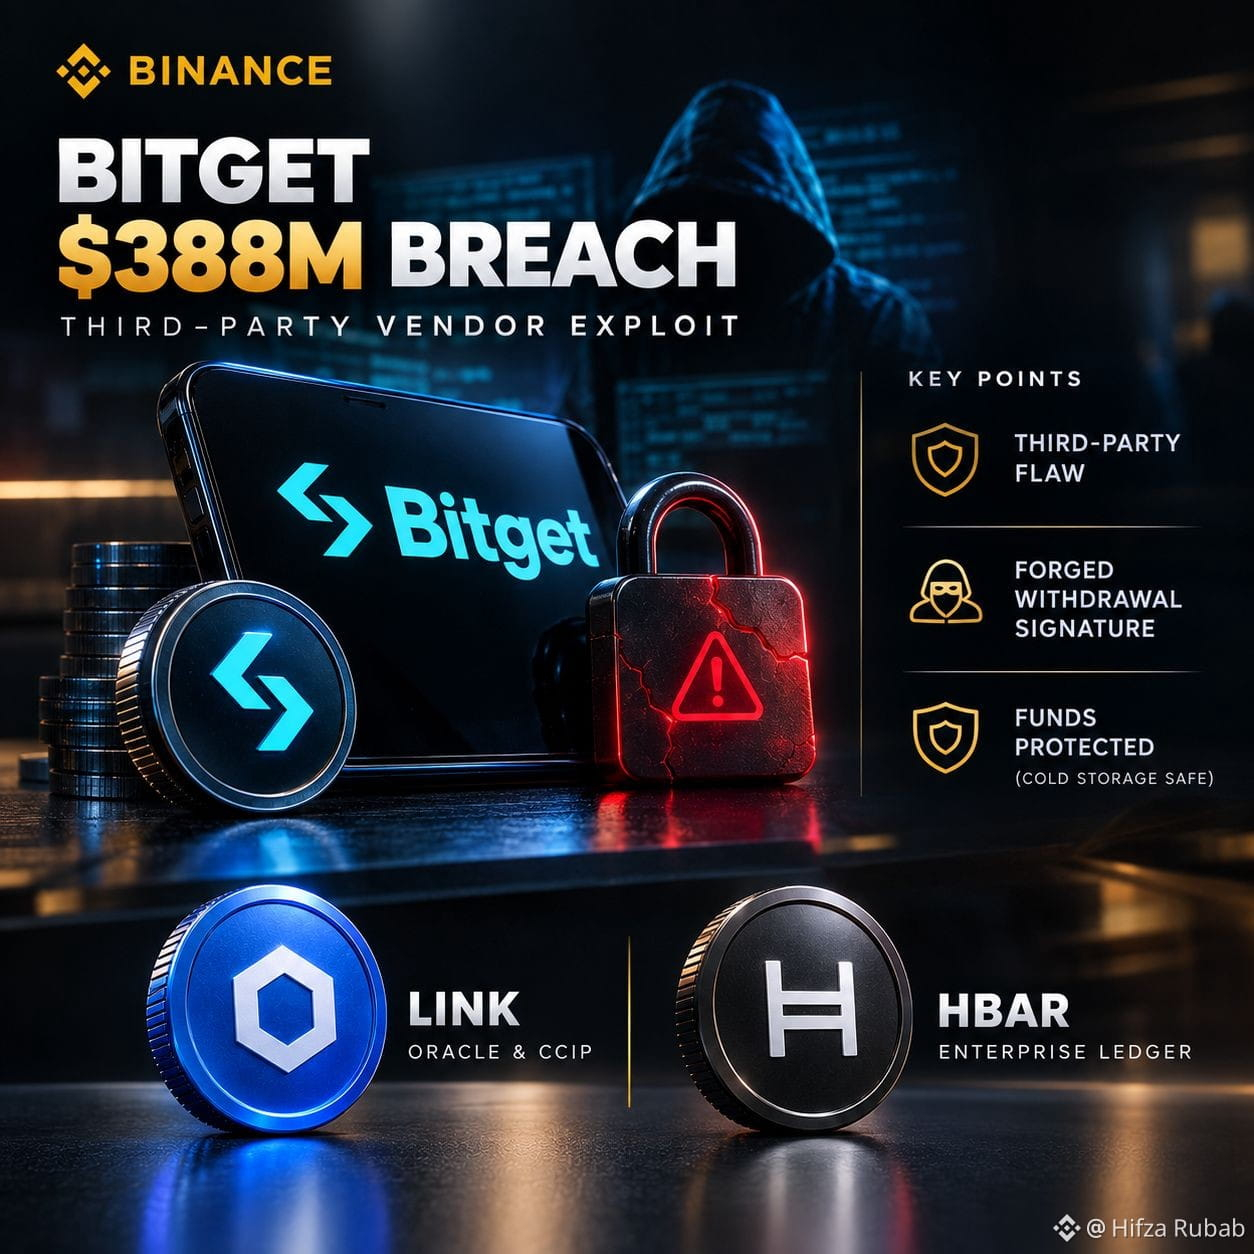
🚨 BITGET $388M HOT WALLET BREACH: THIRD-PARTY VENDOR EXPLOIT! 🛡️💥
Bitget has confirmed a major security incident involving ~$388M in unauthorized transfers from operational hot and warm wallets. However, user funds remain fully backed, and cold storage was completely unaffected! 🏦⚡
💡 Key Technical Takeaways & Insights:
🔹 Third-Party Flaw: Private keys were not compromised. Attackers exploited a critical vulnerability in a third-party security software tool to obtain high-level internal credentials.
🔹 Forged Withdrawal Signature: Armed with stolen credentials, the attacker sent counterfeit withdrawal commands that bypassed automated risk controls.
🔹 Full Protection Coverage: The exchange's $464M Protection Fund is covering all lost assets, and withdrawals are being restored in phases.
🎯 2 Security & Interoperability Coins to Watch:
🌐 $LINK (Chainlink) — Industry-standard decentralized oracle network and CCIP framework driving automated multi-signature security checks across Web3! ⚡🚀
🪐 $HBAR (Hedera) — Enterprise-grade distributed ledger protocol engineered for transparent, real-time supply chain and vendor security auditing! 🛡️📈
How should major crypto exchanges handle vendor security audits to prevent third-party exploits? Drop your thoughts below! 👇✨
#BitgetHotWalletBreachTiedToThirdPartySecurityFlaw
#JapanMOFStudyGroupOnTokenizedGovtBonds
#QNTRises287%
#TrumpRejectsAIRulesForVoluntaryAudits