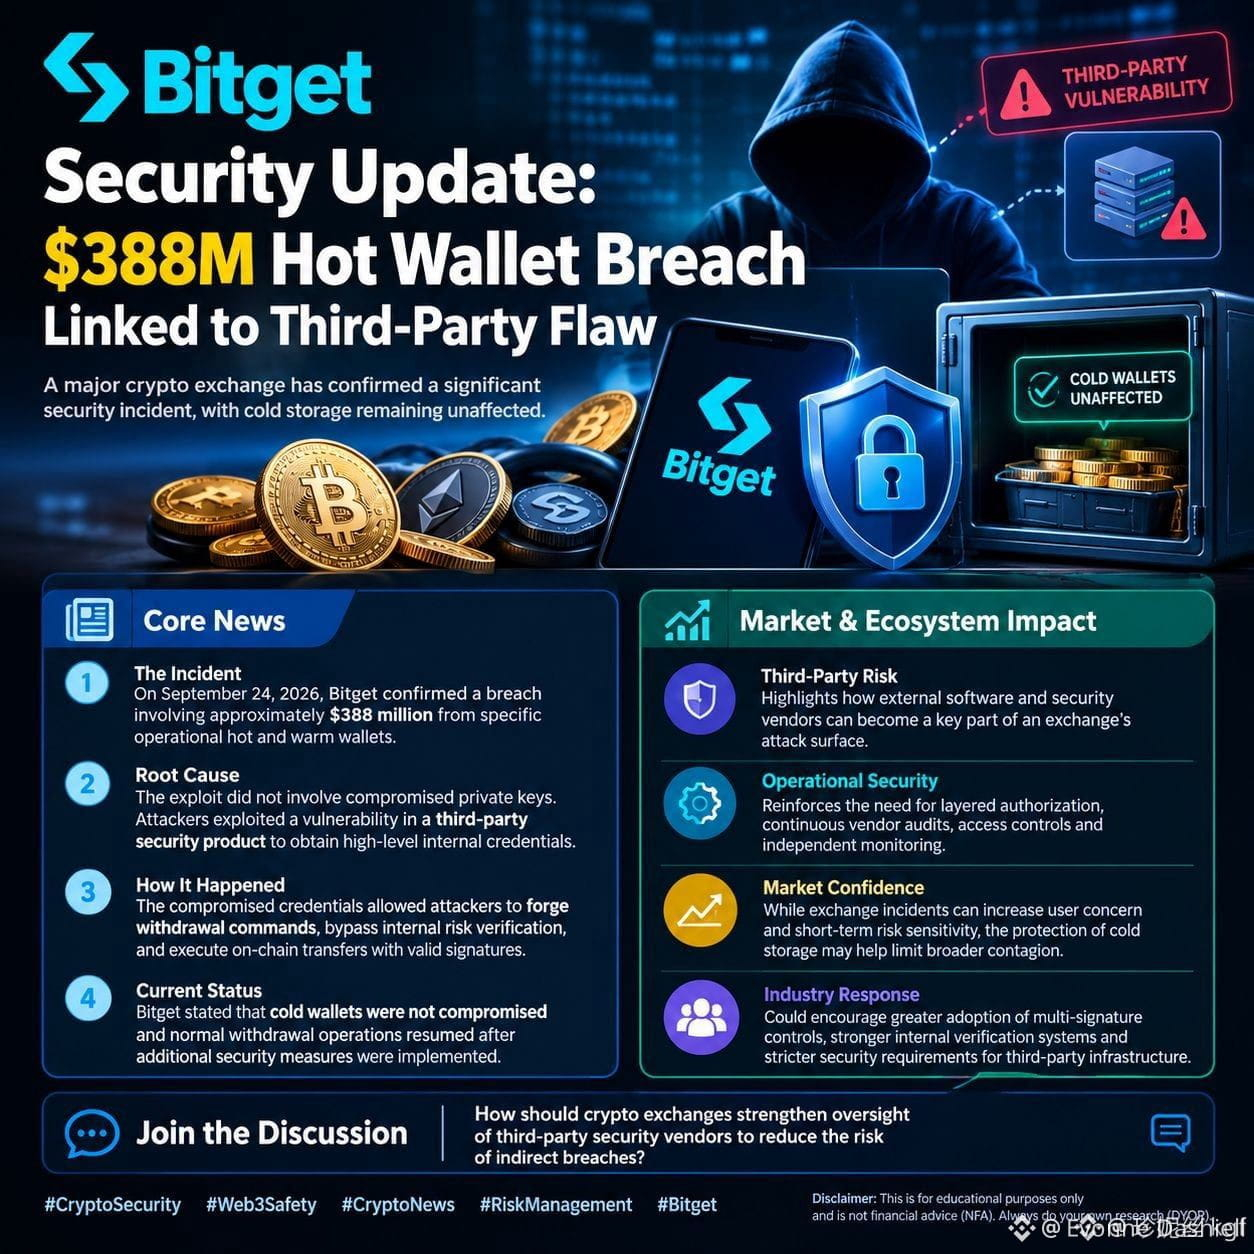
Most exchange hacks start with a vendor nobody even knew existed.
That sinking feeling hits when you realize your funds were one third-party bug away from vanishing, especially after stacking $USDT and $SOL in a hot wallet during this greed stretch. I've seen too many traders lose sleep over it across cycles.
I've traded through enough of these to recognize the pattern. Back in 2018, everyone treated hot wallets as safe because the exchange logo looked solid, until a vendor slip drained accounts overnight. The 2022 bridge exploits followed the same script. Third-party flaws keep evolving because platforms outsource keys, APIs, and monitoring they never fully control. Convenience always wins until it doesn't.
The real lesson from Bitget's situation is not panic. It is treating every hot wallet as a temporary on-ramp. Move size to cold storage when Fear and Greed sits at 67 and people are chasing $DOT without asking who else can sign. Survivors from past cycles did exactly that. They treated security as the one thing they actually owned.
How are you handling custody after seeing this kind of news?
#BitgetHotWalletBreachTiedToThirdPartySecurityFlaw #SECChairWantsStockMarketsOnChain #ChainlinkLaunchesBankSWIFTLedgerFramework