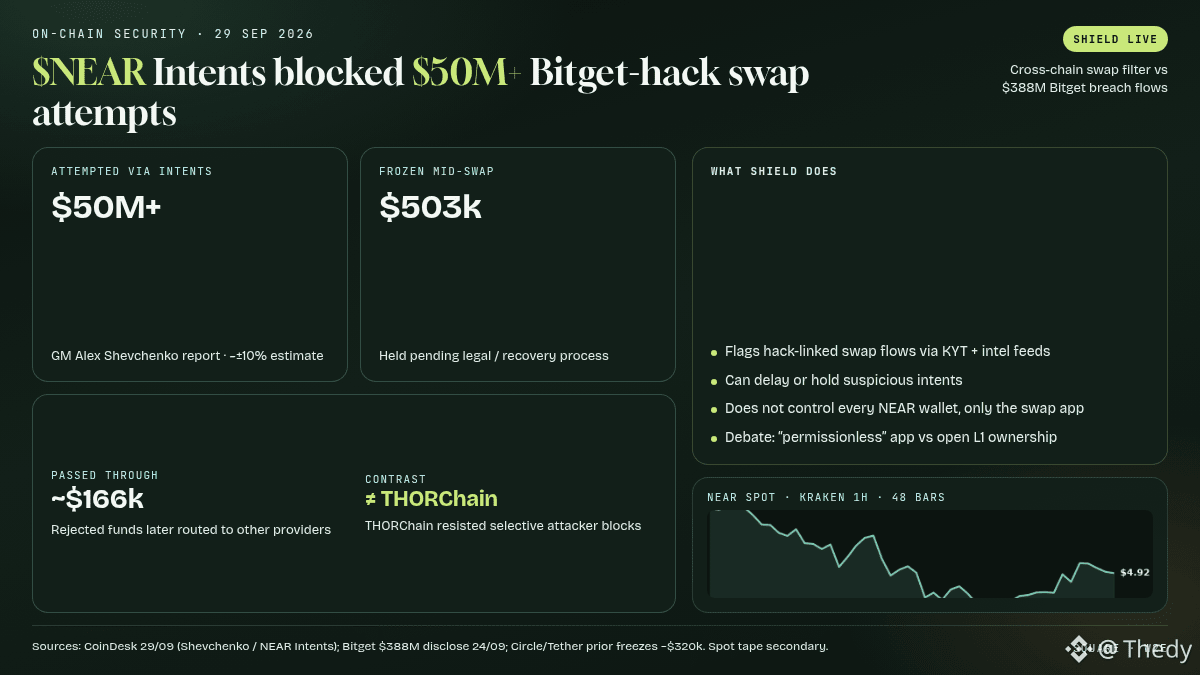
$NEAR Intents blocked more than $50M in swap attempts related to the Bitget hack.
Facts (CoinDesk 29/09, report by GM Alex Shevchenko):
• More than $50M in flows tied to the Bitget theft (~$388M announced on 09/24) attempted to route through NEAR Intents
• The SHIELD system blocked most of it; ~${503}k$ frozen mid-swap
• About $166k still got through; the rejected funds were then routed elsewhere (estimate ±10%)
• Unlike THORChain, which refused to selectively block addresses targeted by the attack
• Reminder: Circle and Tether had already frozen ~${320}k$ of stables linked to the breach
Interpretation: the debate is not “NEAR censors the chain.” Intents is a cross-chain swap app with KYT filters. Illia Polosukhin frames it like this: permissionless = being able to hold, transfer, or deploy without permission on the L1—not the obligation for every app to process every flow. Open question on the process side: who authorizes the release of frozen funds, and what recourse exists in case of a false positive.
Scenarios:
1. Recovery via legal channels Bitget / law enforcement: the ~503k$ enter a restitution process
2. The “permissionless” controversy weighs on the Intents narrative, without breaking the volume (~$100M+/day cited by Shevchenko)
3. Attackers route through other bridges/swaps with less filtering (already observed after rejection)
Spot (Kraken ~17:05 UTC): $NEAR ~4.93$ (+2% 24h), $BTC ~83.1k, Fear & Greed 73.
Do you prefer apps that filter hack proceeds, or neutrality like THORChain at all costs?
#NEAR #Crypto #Security