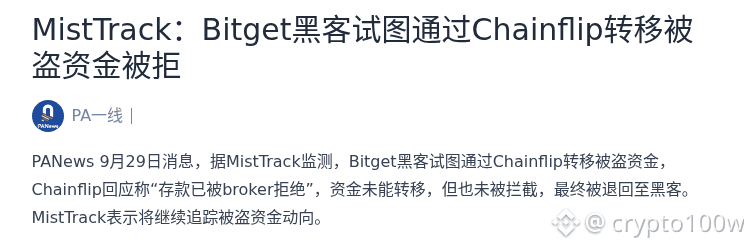
Bitget hackers tried to use Chainflip to route funds across, but the broker rejected it.
PANews on September 29 reports that, according to monitoring by MistTrack, the stolen funds were unable to complete the cross-chain transfer, were not directly blocked by the protocol side, and ultimately were returned to the hacker’s address. For trading platforms and cross-chain infrastructure, the bad news is that the suspicious funds are still moving; the good news is that they were not successfully laundered out this time.
Next, two points to watch: whether MistTrack will continue to trace these funds, whether Bitget will disclose more complete details of the handling progress, and whether Chainflip may further clarify its risk-control boundaries for suspicious fund flows. Which are you more concerned about—whether the funds were stopped, or whether they may find another route and continue to be dispersed?
Figure 1: Bitget hacker funds transfer rejected by Chainflip · Source page partial screenshot
Image source: https://www.panewslab.com/zh/articles/01a0eb20-432d-7160-b5c5-029357f9620c