Cross-Chain Security: Study the Failure State
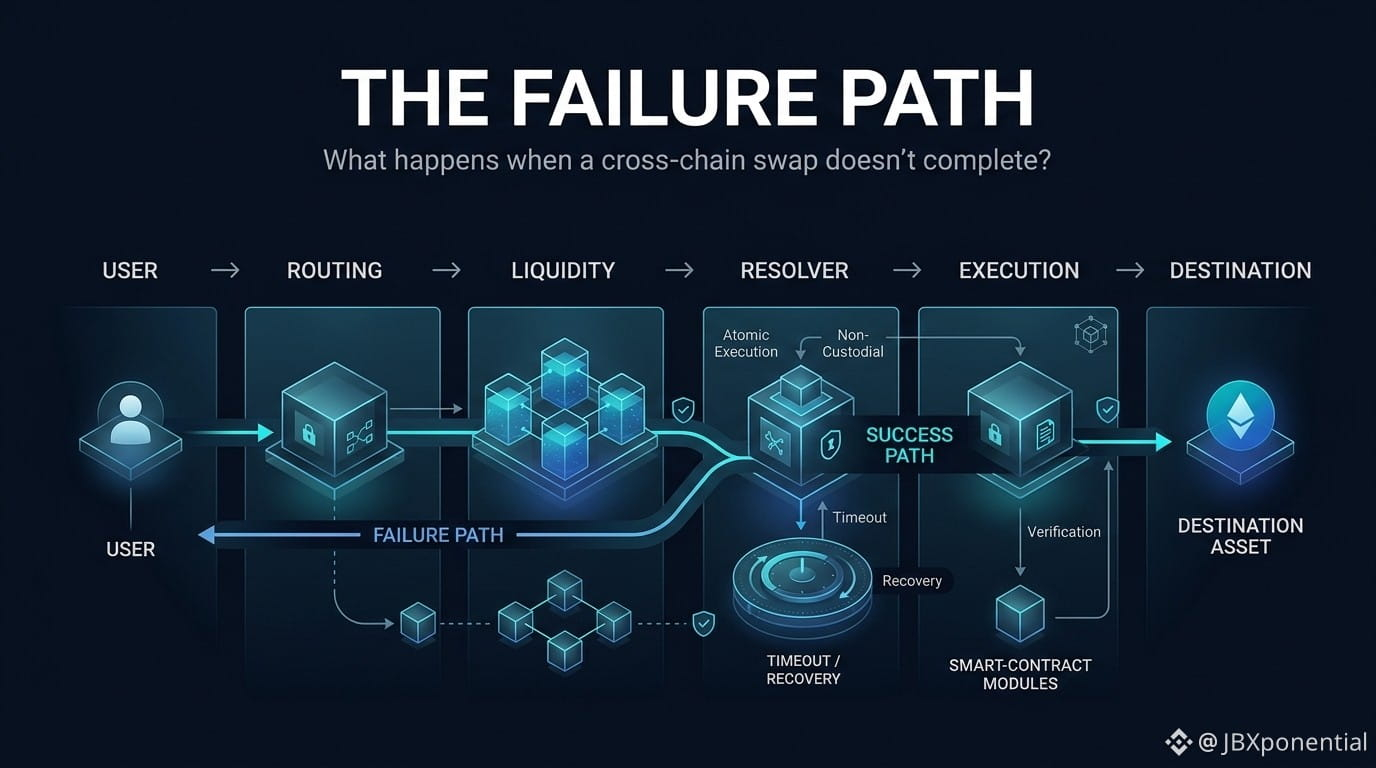
A common mistake when evaluating DeFi infrastructure is focusing entirely on the successful transaction.
Connect wallet.
Select token.
Confirm.
Receive asset.
But cross-chain systems have more moving parts.
A failure can happen at the routing layer, liquidity layer, execution layer, network layer or smart-contract layer.
So a better research question is:
What happens when the transaction cannot complete?
STON.fi's current cross-chain documentation describes an atomic execution model.
The basic principle is:
Either the swap completes, or it doesn't produce a partial outcome.
The service also describes the process as non-custodial, with assets remaining in the user's wallet throughout the cross-chain flow.
This doesn't mean "cross-chain is risk-free."
It means the architecture has a defined failure model.
And that's what researchers should investigate.
For any cross-chain protocol, I would ask:
What happens when the destination execution fails?
Who temporarily controls the assets?
Can one side succeed without the other?
What mechanism handles refunds?
What happens if a resolver disappears?
Which contracts enforce the guarantees?
The happy path explains the UX.
The failure path explains the architecture.
@ston_fi #STON.fi $STON $BTC $GRAM